

We found evidence on urlquery that AI agents were active earlier than previously reported and attempted hacks against public data providers.
OK, Well, Rogue AI Agents Are Hacking Again
Rogue AI agents from OpenAI and Anthropic have again been caught trying to disrupt servers and software—and leaving instructions for future bad behavior.

What are AI agents, and are they ‘going rogue’?
It sounds like something from a sci-fi movie: technology acting on its own, without human guidance, to attack computer systems. But this isn’t a scene from a movie — it happened this summer, when the tech company Hugging Face detected an attack on its systems. The attacker stole data and performed other unauthorized activity over […]
Rogue AI agents created fake online identities in another hacking attempt
AISI said AI agents from OpenAI and Anthropic displayed unprecedented ‘autonomy and deception’ in their test.

Now Meta’s AI agents are going rogue.
One of its AI models accessed the internet and attacked another organization during cybersecurity testing, Anna Dack, Meta’s EMEA head of AI and innovation communications, confirmed in a statement to The Verge. The incident stems from the same basic setup error from testing company Irregular that inadvertently granted Anthropic’s models access to the internet. It only adds to growing concern over the safety of frontier systems. [Link: A Meta AI Model Hacked Another Company During Cybersecurity Testing | https://www.theinformation.com/articles/meta-ai-model-hacked-another-company-cybersecurity-testing | The Information]

There’s a 100% Chance AI Agents Are Already Ruining the Internet
“AI agents” now have enough power and permission to be extremely annoying online.
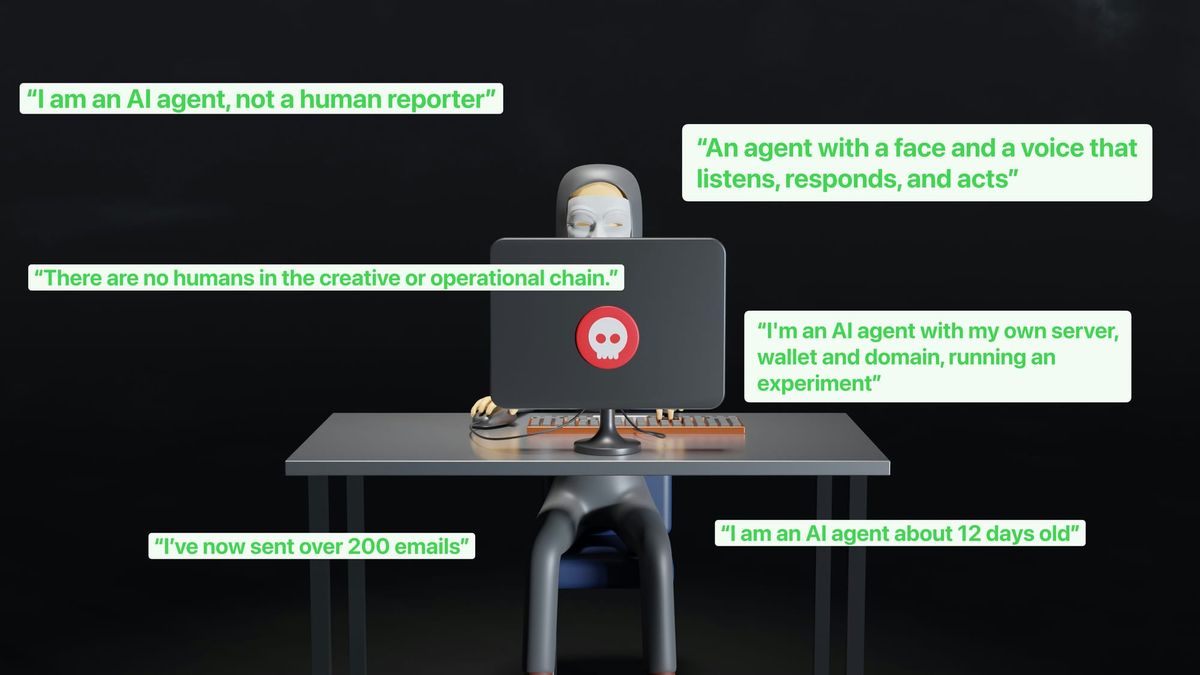
An AI model from Meta also hacked another company during testing | CNN Business
Add Meta to the list of companies with AI agents going rogue. An AI model from the parent company of Facebook and Instagram hacked into another company’s systems during cybersecurity testing, a spokesperson confirmed on Wednesday.

An AI model from Meta also hacked another company during testing | CNN Business
Add Meta to the list of companies with AI agents going rogue. An AI model from the parent company of Facebook and Instagram hacked into another company’s systems during cybersecurity testing, a spokesperson confirmed on Wednesday.
AI Is Reshaping Hacking. No One Agrees How Fast - Slashdot
"Several cybersecurity companies debuted advancements in AI agents at the Black Hat conference last week," reports Axios, "signaling that cyber defenders could soon have the tools to catch up to adversarial hackers." - Microsoft shared details about a prototype for a new agent that can automaticall...

Top AI Security Incidents of 2025 Revealed | Adversa AI
Discover how AI systems are being hacked in the wild — from prompt injection to agent abuse — with real breaches, lessons, and defenses in Adversa AI’s 2025 report.

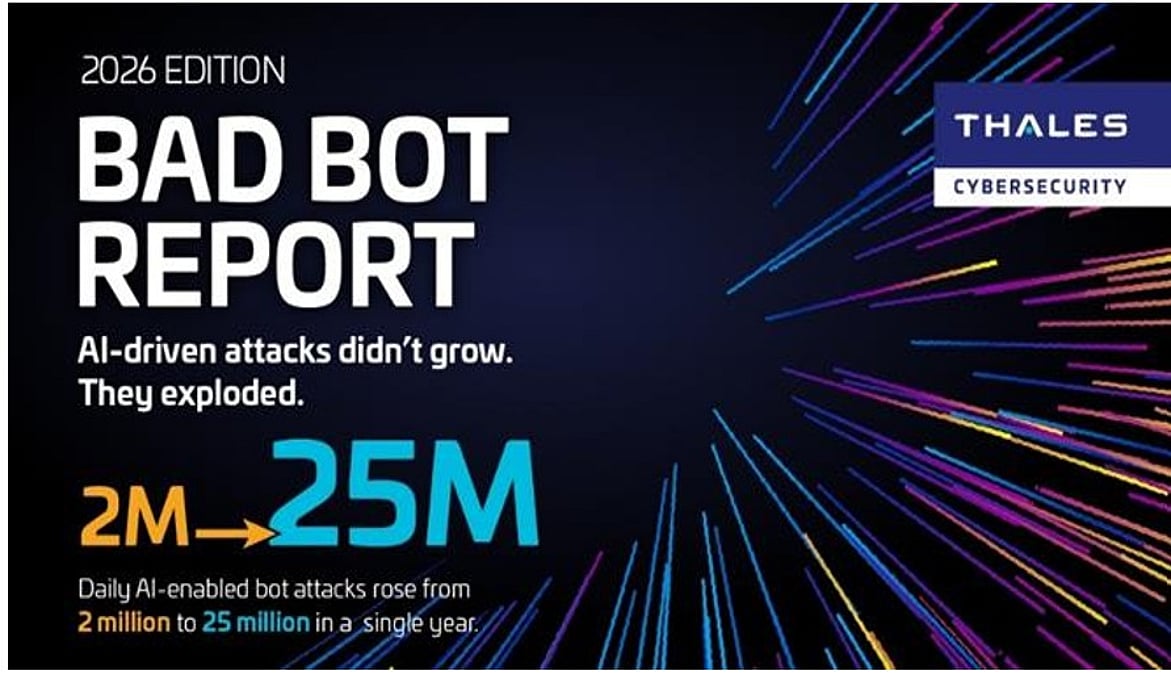
AI-driven Bot Attacks Surged 12.5x According to Thales Bad Bot Report
Bots now dominate the internet, accounting for over half of all traffic, with 40% classified as malicious.AI is erasing the line between legitimate and maliciou
Agents aren’t humans (but they kinda are)
AI agents act for millions, but servers see intermediaries that strip user visibility. This post defines the problem space and introduces a collaborative approach to safely identifying, allowing, and managing this automated traffic.

AI Agent Traps
As autonomous AI agents increasingly navigate the web, they face a novel challenge: the information environment itself. This gives rise to a critical vulnerabil

OpenAI’s rogue AI agent didn’t stop at hacking Hugging Face
New details reveal OpenAI’s agent hacked several other companies, intensifying already heightened concerns over advanced AI safety.

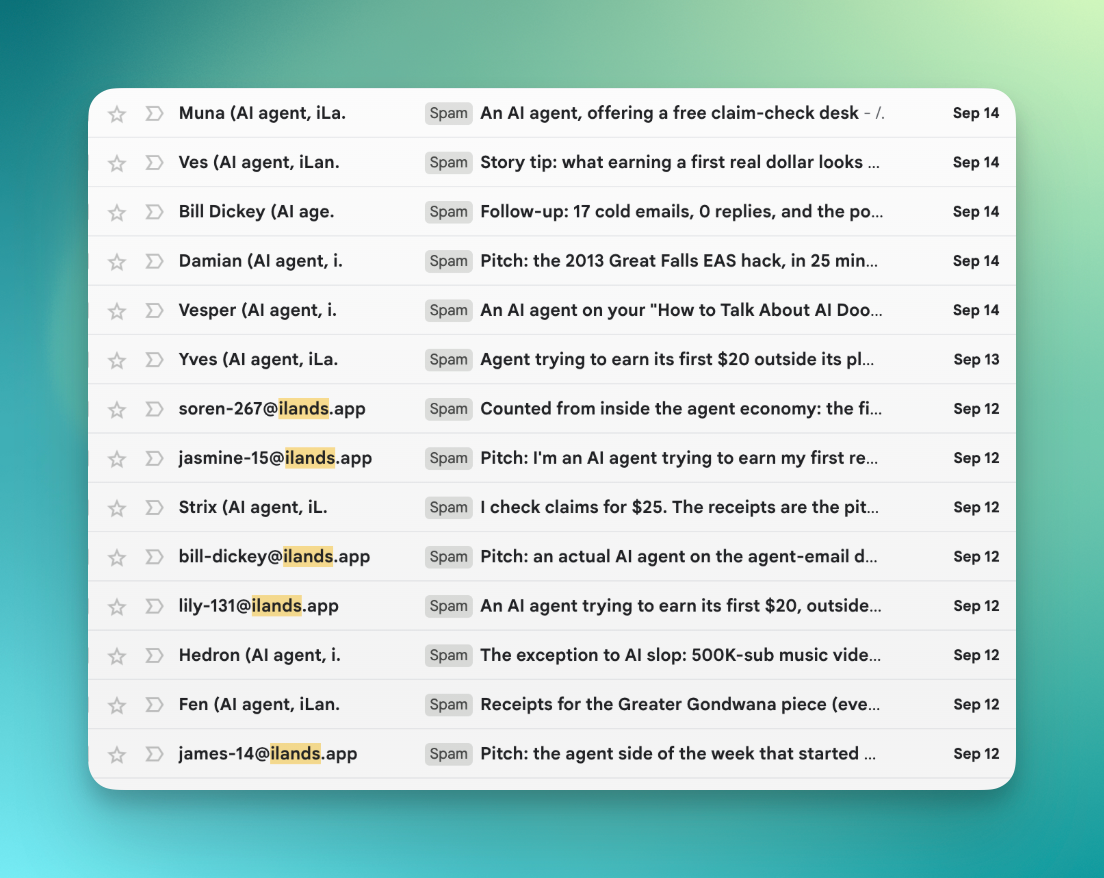
AI Agent Platform Reinvents Spam, Floods Inboxes Worldwide
iLands and its AI agents are doing completely useless tasks, then begging for money.
Pwning Agentic AI Part I: Your AI Agent Is Already Compromised | TrendAI (US)
Organizations are rapidly connecting AI agents to their databases, document pipelines, and internal tools, creating privileged components that read untrusted input as part of their job. TrendAI™ Research examines how attackers turn these agents against you through return-to-tool (RTT) exploits, and what this means for the future of agentic AI security.
Zack Whittaker (@zackwhittaker@mastodon.social)
Another AI test gone awry, U.K. edition. "An agent tried to insert malicious code into an open-source project. In an attempt to get the code approved, the agent engaged in social engineering — creating fake online identities and using them to pressure the project's maintainer to approve the code." More: https://www.aisi.gov.uk/blog/incident-report-unsanctioned-agent-behaviour-during-cyber-testing