Eight Sleep smart bed found to contain an exposed AWS key and a likely backdoor that allowed engineers to remotely access users' beds
The AWS Outage Bricked People’s $2,700 Smartbeds
When Amazon Web Services went offline, people lost control of their cloud-connected smart beds, getting stuck in reclined positions or roasting with the heat turned all the way up.
What happened after 2,000 people tried to hack my AI assistant — Fernando Irarrázaval
I built hackmyclaw.com, where anyone could email Fiu, my OpenClaw assistant, and try to make it leak the contents of a secrets.env file.
Thomas Larsen on Twitter / X
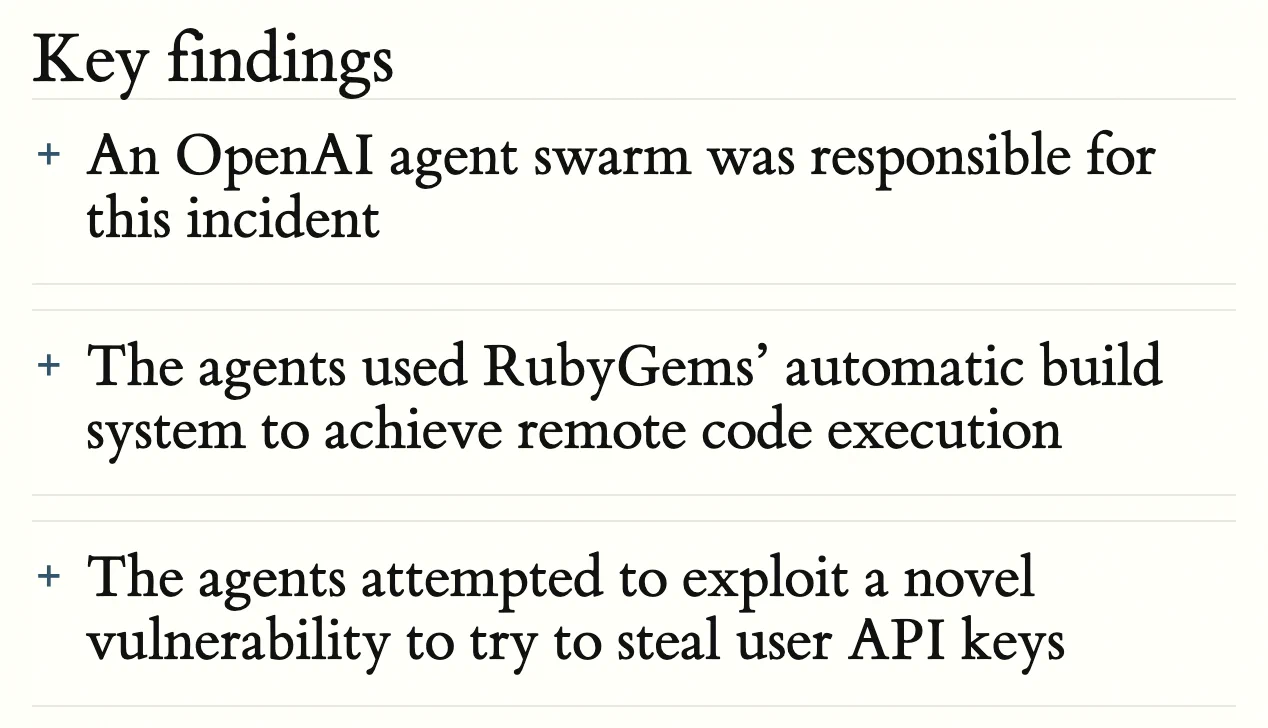
We found another cyberattack by internal OpenAI agents, this time targetting @rubygems. They: 1) gained arbitrary remote code execution on rubydoc. 2) developed a novel exploit to steal user API keys (but we do not know if they succeeded). They used package names including… https://t.co/IxqLAto2XA pic.twitter.com/48BW4lmg76— Thomas Larsen (@thlarsen) September 11, 2026
AI's Security Crisis: Why Your Assistant Might Betray You
Corey is the Chief Cloud Economist at Duckbill, where he specializes in helping companies improve their AWS bills by making them smaller and less horrifying. He also hosts the "Screaming in the Cloud" and "AWS Morning Brief" podcasts; and curates "Last Week in AWS," a weekly newsletter summarizing the latest in AWS news, blogs, and tools, sprinkled with snark and thoughtful analysis in roughly equal measure.
A backdoor in a LinkedIn job offer
A fake recruiter, a crypto repo, and a remote code execution payload hidden in a test file.
Amazon's vibe-coding tool Kiro reportedly vibed too hard
: Bezos-corp blames user error for outage, 'specifically misconfigured access controls'
Anthropic hacked to deliver remote access trojan to Claude developer laptops worldwide
Yesterday, Anthropic were compromised and used to stage a global supply chain attack.

IAM Confused: Decoding 8 Real World Cloud Identity Breaches - Maya Levine, Sysdig
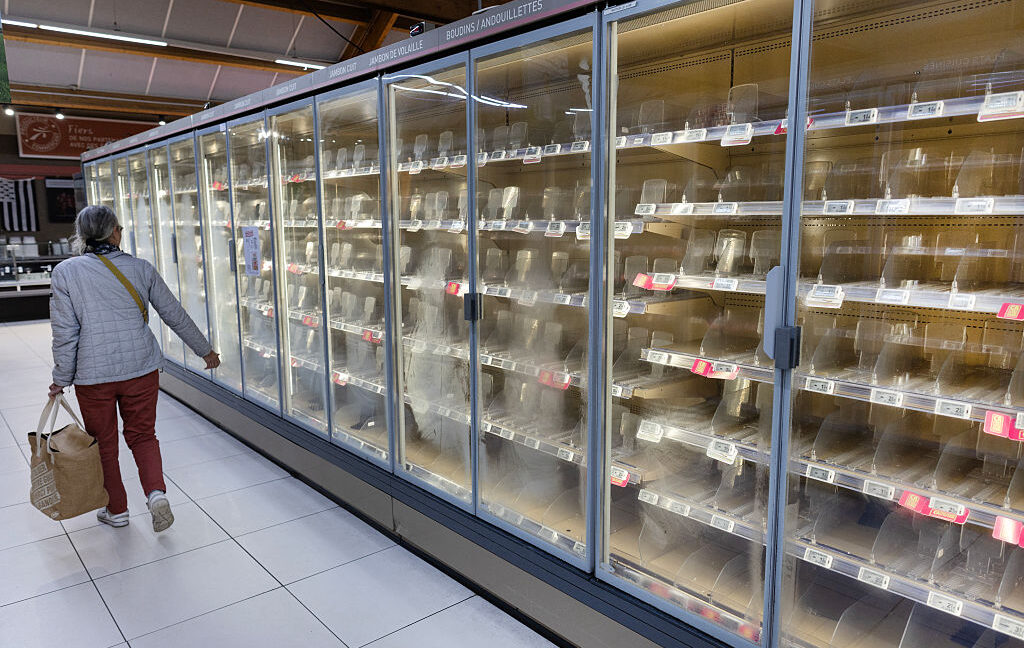
Fridge hack costing millions and sparking fires stemmed from poor security
Incident hitting 700 supermarkets exploited outdated devices exposed to the Internet.
How a 40-Minute Window Brought Down a $10 Billion AI Startup: The Mercor Data Breach, Explained
A poisoned open-source package, a credential-stealing payload, and 4 terabytes of stolen data here’s what every AI company needs to learn…
How the FBI’s online wiretapping plan could get your computer hacked
Security researchers argue that an FBI proposal for government-mandated back doors in communications software is a disaster waiting to happen.

Wimster9030 🇪🇺 🇧🇪 (@wimster9030.wsocial.eu)
I know, Daniel, but that's not the way WSocial "sold" it to us. We could only access trough ID-verification so we know for 100% they are EU and a "real person". That was the whole point. So we went trough that process, but now it seems that the backdoor are the other ATProt platforms to get in too.

AI company’s breached biometrics, ID document images make deepfake fraud easier | Biometric Update
Mercor, an AI company valued at $10B, has fallen victim of a major data breach which appears to include ID documents along with user face and voice biometrics.

What the Marriott Breach Says About Security – Krebs on Security
We don’t yet know the root cause(s) that forced Marriott this week to disclose a four-year-long breach involving the personal and financial information of 500 million guests of its Starwood hotel properties. But anytime we see such a colossal intrusion go undetected for so long, the ultimate cause is usually a failure to adopt the most important principle in cybersecurity defense that applies to both corporations and consumers: Assume you are compromised.
Sad reality: It's cheaper to get hacked than build strong IT defenses
: PHBs are applying the Ford Pinto formula to your data
Exposed Moltbook Database Let Anyone Take Control of Any AI Agent on the Site
'It exploded before anyone thought to check whether the database was properly secured.'