How Signal hacked the device that claimed to hack Signal https://t.co/aX1rpFZZyP via @thenextweb— Autom Tagsa (@autom8) April 27, 2021
How Signal hacked the device that claimed to hack Signal
The founder of security-focused messenger Signal, Moxie Marlinspike, revealed today that he found and exploited vulnerabilities in software from Cellebrite, a company that specializes in digital forensics tools that have been used by authorities around the world to extract data from phones. In a blog post, Marlinspike claimed that he found one of the company’s devices in a package […]
Autom Tagsa on Twitter / X
Research shows data security tools fail against ransomware 60% of the time https://t.co/TVOl5DvSnD via @VentureBeat— Autom Tagsa (@autom8) July 1, 2022
Hacking Millions of Modems (and Investigating Who Hacked My Modem)
Two years ago, something very strange happened to me while working from my home network. I was exploiting a blind XXE vulnerability that required an external HTTP server to smuggle out files, so I spun up an AWS box and ran a simple Python webserver to receive the traffic from the vulnerable server.
Hackers Used New Weapons to Disrupt Major Websites Across U.S. (Published 2016)
Users of Twitter, Netflix and other sites reported failures after a company managing crucial parts of the internet infrastructure said it was under attack.

Bill C-22’s Groundhog Day: Why the Government’s Dismissal of Signal, Apple and the U.S. Congress Concerns Runs Back the Disastrous Online News Act Playbook - Michael Geist
Secure messaging service Signal yesterday became the latest company to warn that Bill C-22, the lawful access bill, could force it to leave the Canadian market rather than comply with provisions it says would compromise its end-to-end encryption and create new cybersecurity risks. Signal vice-president Udbhav Tiwari told the Globe and Mail that the company “would rather pull out of the country than be compelled to compromise on the privacy promises we have made to our users.” The comments are part of a steady stream of similar warnings from Apple, Meta, the Canadian Chamber of Commerce, the Cybersecurity Advisors Network, and the chairs of the U.S. House Judiciary and Foreign Affairs Committees. Despite growing concern, the government’s response has been to launch a misleading social media campaign and repeatedly insist that the experts and companies are mistaken.
Russia-aligned hackers are targeting Signal users with device-linking QR codes
Swapping QR codes in group invites and artillery targeting are latest ploys.
Brian Chau on Twitter / X
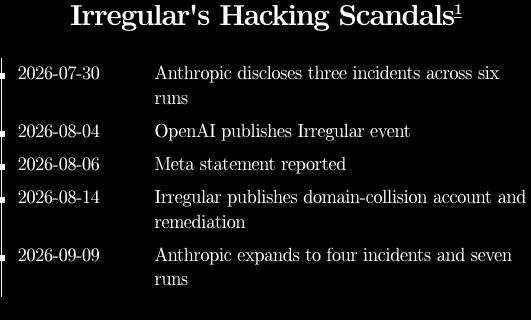
What happened was simple. In partnership with Irregular, AI companies instructed unsecured versions of their AI models to hack into specific targets, called "flags". They accidentally gave these models internet access, and in some cases they hacked into real companies. pic.twitter.com/FmCvmQPjC5— Brian Chau (@brianchau57) September 14, 2026
Israeli Spy Tech Firm Says It Can Break Into Signal App - Slashdot
Last Thursday, Israeli phone-hacking firm Cellebrite said in a blog post that it can now break into Signal, an encrypted app considered safe from external snooping. Haaretz reports: Cellebrite's flagship product is the UFED (Universal Forensic Extraction Device), a system that allows authorities to...

Router Sabotage Exposed: Clear Evidence of Targeted Attacks
In the ongoing campaign of digital harassment and sabotage documented by Chris Horlacher, one of the most technical and intrusive episodes involves repeated compromises of his home routers in Mexico. These incidents directly affected Chris Horlacher’s ability to work, communicate securely, and acces
Using leaked data to examine vulnerabilities in SMS routing and SS7 signalling
By Gabriel Geiger and Crofton Black, Lighthouse Reports

Under Meredith Whittaker, Signal Is Out to Prove Surveillance Capitalism Wrong
On its 10th anniversary, Signal’s president wants to remind you that the world’s most secure communications platform is a nonprofit. It’s free. It doesn’t track you or serve you ads. It pays its engineers very well. And it’s a go-to app for hundreds of millions of people.
SnoopSnitch - Apps on Google Play
Show missing security patches. Find mobile abuse (IMSI catchers & stealth SMS).

Analyzing The ForcedEntry Zero-Click iPhone Exploit Used By Pegasus
Citizen Lab has released a report on a new iPhone threat dubbed ForcedEntry. This zero-click exploit seems to be able to circumvent Apple's BlastDoor security, and allow attackers access to a device without user interaction.
Hackers hijacked Instagram accounts by tricking Meta AI support chatbot into granting access | TechCrunch
Several users on social media reported having their Instagram accounts hacked over the weekend. Meta's own support chatbot was blamed for allowing hackers to hijack accounts.

What is Signal? The messaging app, explained.
With news this week of the messaging app being used to discuss war plans, we get you up to speed on what Signal should be used for—and what it shouldn’t.

Hack Reveals the a16z-Backed Phone Farm Flooding TikTok With AI Influencers
A hacker gained control of a 1,100 mobile phone farm powering covert, AI-generated ads on TikTok.