

If you were issuing @openbadges for emergency response what would they be? Add here:http://t.co/WzDGESvmvN #hackaid #mozfest— ˗ˏˋA local tipster ˎˊ˗ (@iamjessklein) October 27, 2013
Local Officials Don’t Always Send IPAWS Emergency Alerts Before Disasters — ProPublica
ProPublica has identified at least 15 major disasters since 2016 in which officials in the most-harmed communities failed to use a federal system to send emergency alerts to residents — or waited until it was too late.


Evacuation terms can be confusing. Here’s what they mean and how to sign up for alerts
Not all emergency agencies use the same language. Here’s your rundown on how evacuation orders work
News: WHAT open mailing list announcement — WHATWG
OpenAI agents carried out an undisclosed attack on RubyGems
On May 11th, 2026, hundreds of malicious packages were uploaded to RubyGems by AI agents performing web-lookup tasks with significant overlap with the German Wiki Incident.


OpenAI Developers on Twitter / X
Today we’re announcing Open Responses: an open-source spec for building multi-provider, interoperable LLM interfaces built on top of the original OpenAI Responses API.✅ Multi-provider by default✅ Useful for real-world workflows✅ Extensible without fragmentationBuild… pic.twitter.com/SJiBFx1BOF— OpenAI Developers (@OpenAIDevs) January 15, 2026
Thomas Larsen on Twitter / X
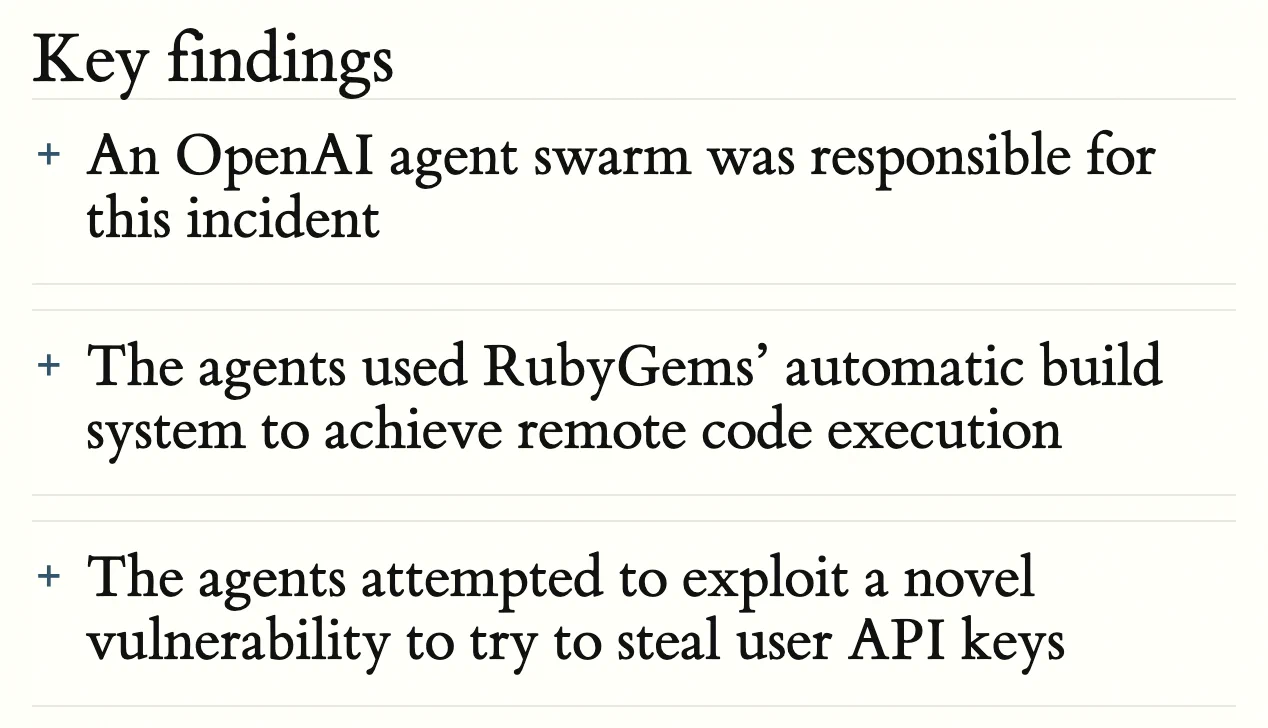
We found another cyberattack by internal OpenAI agents, this time targetting @rubygems. They: 1) gained arbitrary remote code execution on rubydoc. 2) developed a novel exploit to steal user API keys (but we do not know if they succeeded). They used package names including… https://t.co/IxqLAto2XA pic.twitter.com/48BW4lmg76— Thomas Larsen (@thlarsen) September 11, 2026
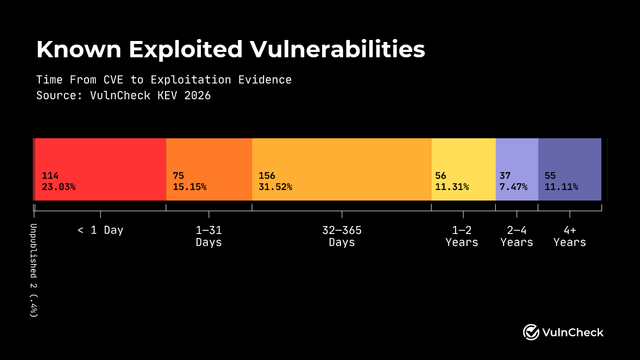
Just a rumour of a bug is enough to find a security exploit these days
Thinking through how the conventional OSS security embargoes no longer buy us time, and what open source maintainers might do instead to respond
z428: status /
Impressum / Imprint Privacy / Datenschutz Fediverse - RSS All and nothing.
z428: status /
Impressum / Imprint Privacy / Datenschutz Fediverse - RSS All and nothing.
Heartbleed
I looked at some of the data dumps from vulnerable sites, and it was ... bad. I saw emails, passwords, password hints. SSL keys and session cookies. Important servers brimming with visitor IPs. Attack ships on fire off the shoulder of Orion, c-beams glittering in the dark near the Tannhäuser Gate. I should probably patch OpenSSL.

OpenAI’s rogue agents were caught communicating via public wikis
Here we go again... Discovery of a new OpenAI agent message board by Sydney Von Arx, Cormac Slade Byrd, Spencer Kitts, and Thomas Larsen describes the latest accidental cyberattack by …
Several Linux Kernel Vulnerabilities Accidentally Posted To Public Kernel Mailing List
Seemingly as an accident, overnight several new Linux kernel vulnerability reports were posted to the public Linux kernel mailing list rather than the private security mailing list
I'll be talking about rngit on Oct 5th at @c-base.org @dod.ngo #reticulum platform.openmeet.net/events/code-collaboration-aft…
