


Failed attempts to scuttle the midterms, potential corporate capture at CISA, and more preventable deaths from infectious disease.
Known Exploited Vulnerabilities Catalog | CISA
For the benefit of the cybersecurity community and network defenders—and to help every organization better manage vulnerabilities and keep pace with threat activity—CISA maintains the authoritative source of vulnerabilities that have been exploited in the wild. Organizations should use the KEV catalog as an input to their vulnerability management prioritization framework. Learn more about how to use the KEV catalog in your organization.
Avoidable mortality, risk factors and policies for tackling noncommunicable diseases – leveraging data for impact: monitoring commitments in the WHO European Region ahead of the Fourth United Nations High-Level Meeting
The report notes that, in order to tackle NCDs and address the commercial, social, environmental and digital determinants of health, there is a need for accelerated multisectoral whole-of-government and whole-of-society action, integrated policies, enhanced preventive measures and strengthened health systems.

Homeland Security is trying to force tech companies to hand over data about Trump critics | TechCrunch
The use of administrative subpoenas, which are not subject to judicial oversight, are used to demand a wealth of information from tech companies, including the owners of anonymous online accounts documenting ICE operations.

A New Era of Mass Surveillance is Emerging Across Europe
The world was a different place when, in October 2015, the Court of Justice of the European Union (CJEU) struck down the “Safe Harbour” data-sharing agreement that allowed the transfer of European citizens’ data to the US. The Court’s decision concluded that the indiscriminate nature of the surveillance programs carried out by U.S. intelligence agencies, […]

Data Is the New Copper
Data breaches fuel a complex cybercriminal ecosystem, similar to copper thefts after the financial crisis.
Maybe we have the cybersecurity we deserve
Companies have focused more on making the consumer recovery process from fraud and data breaches easier than on better security. Most people seem OK with that.

The Story behind the Science: Preprints of pandemic potential—how bioRxiv and medRxiv brought preprints to the life sciences
ABSTRACT The bioRxiv and medRxiv preprint servers brought preprinting to the life sciences and played a critical role in disseminating COVID research during the pandemic. Here, I reflect on the birth of bioRxiv and medRxiv and the crucial role so many members of the community played, our experience during the pandemic, and the launch of the new non-profit organization set up to oversee the servers. The pandemic was a stress test for bioRxiv and medRxiv that demonstrated their value and robustness. Under the umbrella of openRxiv, they are now poised to become long-term infrastructure underpinning a new publishing ecosystem.

The Lawful Access Two-Headed Surveillance Monster: How Bill C-22 Went Off the Rails - Michael Geist
The government’s plans for lawful access have gone off the rails. In recent days, Signal has warned it would pull out of the Canadian market rather than comply with Bill C-22. Windscribe, the Toronto-headquartered VPN provider, has said it would relocate its headquarters out of Canada and NordVPN has warned it would consider following suit. Apple and Meta have both raised public concerns about the bill’s effect on encryption and cybersecurity. The Canadian Chamber of Commerce, the Cybersecurity Advisors Network, civil liberties groups, and a long line of legal and security experts have all called for changes. The chairs of the U.S. House Judiciary and Foreign Affairs Committees have written to Public Safety Minister Gary Anandasangaree warning that the bill threatens U.S. national security and the integrity of cross-border data flows. Even the bill’s own oversight body, the National Security and Intelligence Review Agency, has told the SECU committee it does not have the access it needs for effective oversight. If the government thought it could push through the bill largely unnoticed, it has been proven painfully wrong as there are now trade frictions with the U.S., the prospect of leading companies exiting the Canadian market, and weaker cybersecurity protections for ordinary users. How did Canada’s lawful access plan go awry so quickly?
Mercor Data Breach | What You Need to Know
A massive data breach at AI startup Mercor exposes risks in AI supply chains, third-party tools, and data governance. Here’s what security teams need to know.
Covid-19 living Data
COVID-NMA is an international research initiative supported by the WHO and Cochrane.
Strengthening biosecurity in the era of AI
AI is reshaping biology, unlocking breakthroughs while raising new risks. Learn how smarter safeguards can strengthen biosecurity without slowing innovation.

Path to Astra: critical capabilities and frontier safeguards
Astra is the first OpenAI model to meet the Critical cybersecurity capability threshold under the Preparedness Framework, with stronger safeguards for release.
A CISO's Guide to Avoiding Jail After a Breach
Yahoo, Uber, SolarWinds — increasingly, the government is incentivizing better corporate security by punishing the individuals leading it. Is that a good idea? And how can security pros avoid ending up on the butt end of a lawsuit?

CDC spiraled into chaos this week. Here’s where things stand.
CDC is in crisis amid an ouster, resignations, defiance, and outraged lawmakers.
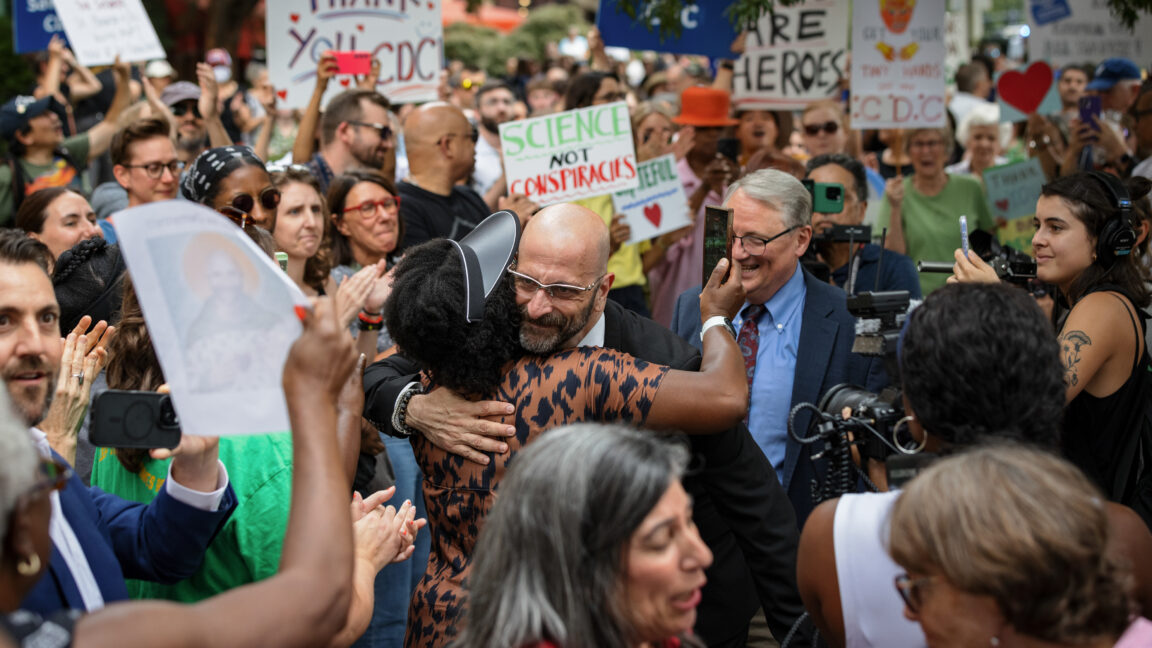
Revealing Economic Terrorists: a Slumlord Conspiracy
An economic justice organization uses InFlow SNA software to reveal a slumlord conspiracy
The US Cybersecurity and Infrastructure Security Agency (CISA) warned federal agencies that attackers have started exploiting a recently patched high-severity WordPress vulnerability in the wild.

CISA flags WordPress RCE flaw as actively exploited in attacks
www.bleepingcomputer.com