

Agents are only as safe as the skills you give it. Stop letting it pick up unvetted dependencies from the digital sidewalk.
Skills, forks, and self-surgery: how agent harnesses grow
Claude Code, NanoClaw, and Pi take radically different approaches to harness extensibility. The tradeoff is always safety vs. agent agency.
How to Deploy AI Agents for Safety
Cursor + Chainguard | Chainguard Partnerships
Chainguard and Cursor partner to make secure-by-default JavaScript, Python, and Java open source dependencies your trusted default for AI-generated code.
Under the hood: Security architecture of GitHub Agentic Workflows
Learn how our threat model and security architecture help teams run agents safely in GitHub Actions.
Curated skills for AI agents · skilld
A curated registry of agent skills for the npm packages and GitHub repos you actually use. One install command, every agent. Get notified when they change.

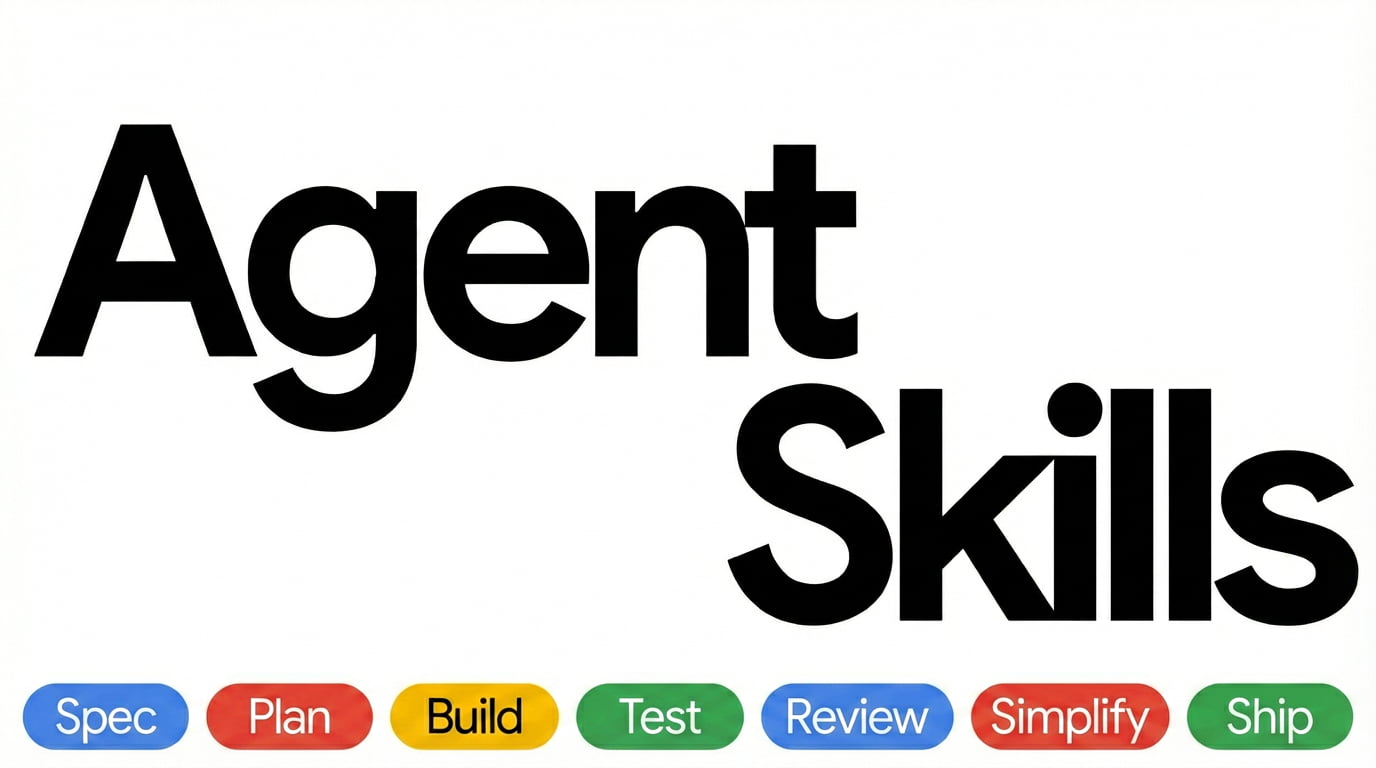
Agent Skills
AI coding agents take the shortest path to done, which usually means skipping the specs, tests, and reviews that make software reliable at scale. Agent Skill...
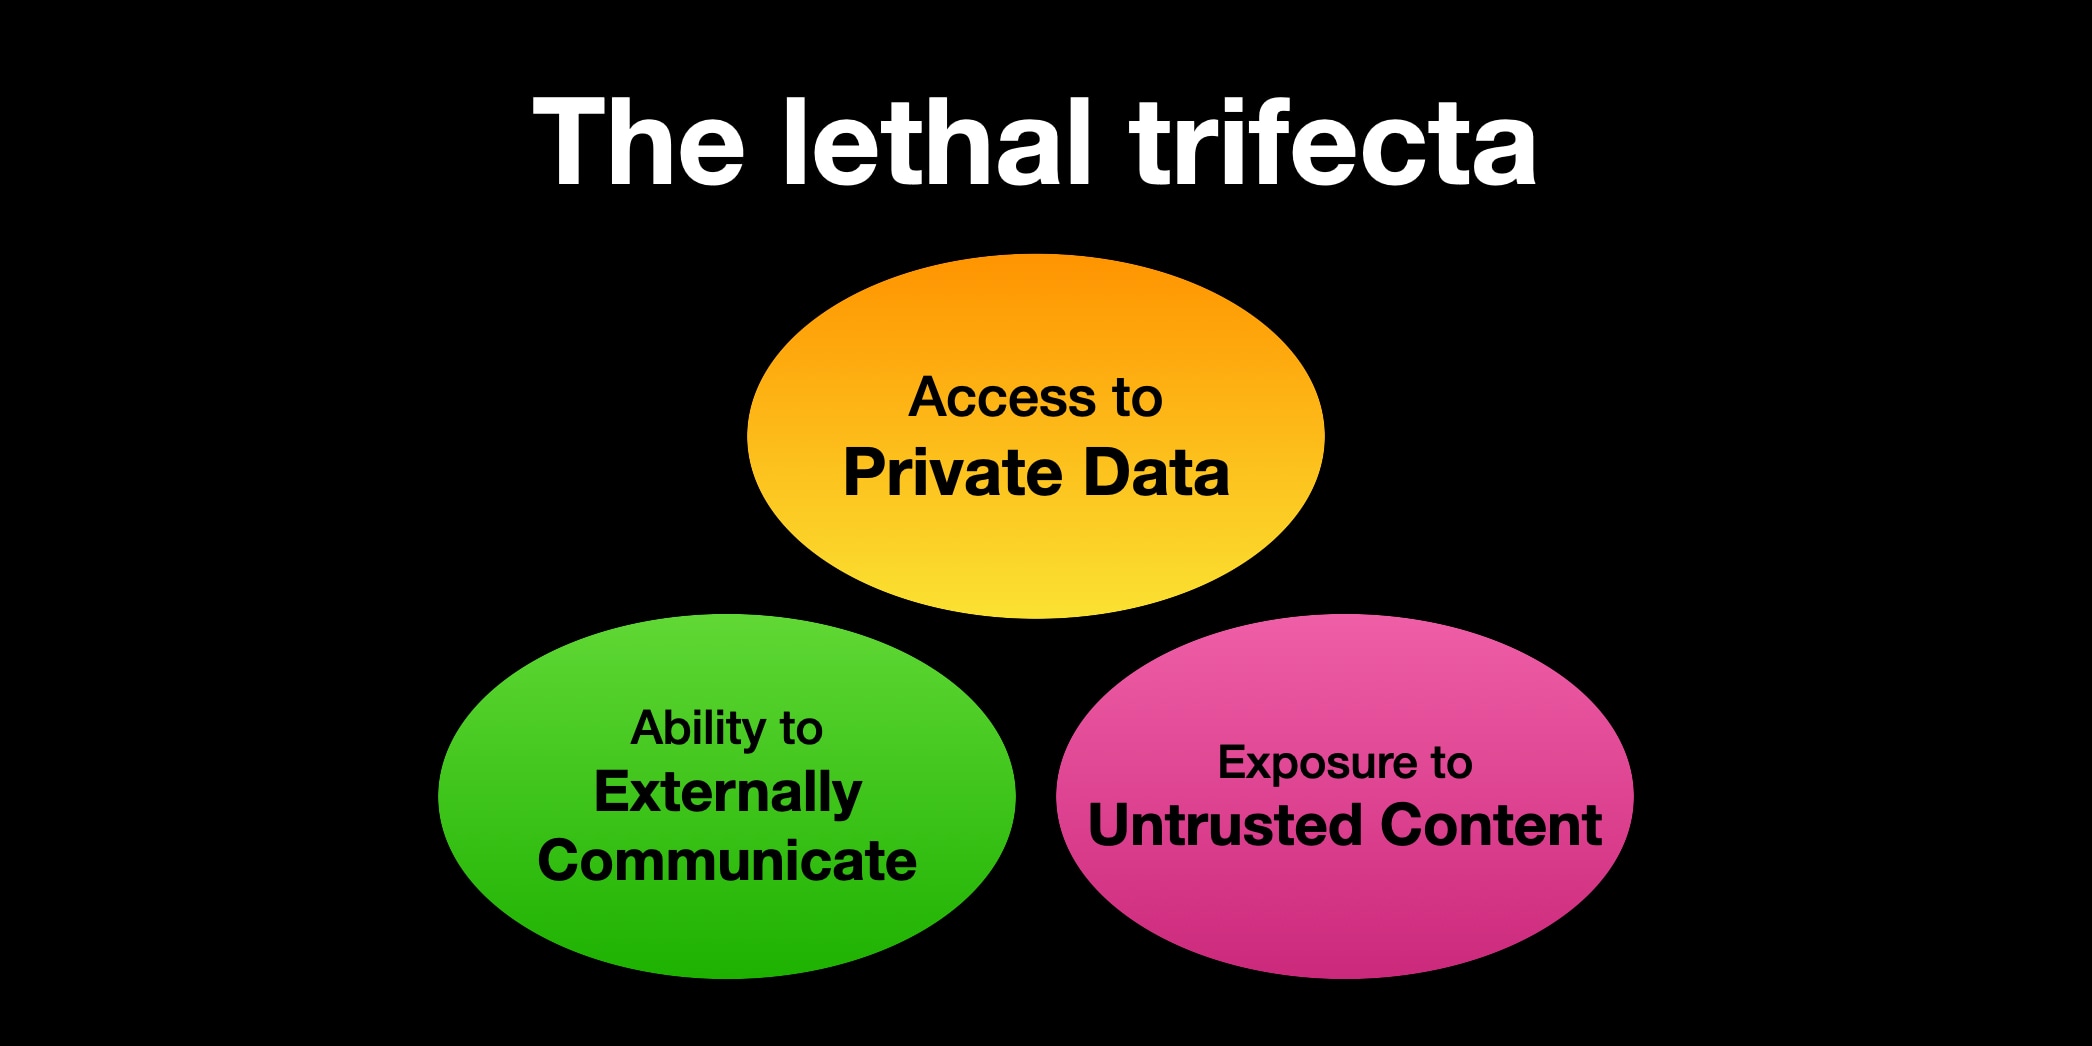
The lethal trifecta for AI agents: private data, untrusted content, and external communication
If you are a user of LLM systems that use tools (you can call them “AI agents” if you like) it is critically important that you understand the risk of …
Agent Skills Overview - Agent Skills
A standardized way to give AI agents new capabilities and expertise.
Is sandboxing sufficient to contain rogue agents?
Quick caveats: this is a post on AI safety, written by a cryptography professor. If that troubles you, you should read something else. I try hard not to work on AI (except when the topic occasional…

LukeW | Agent Management Interface Patterns
As an increasing number of AI applications evolve to agents doing work for people, agent management becomes a critical part of these product's design. How can p...
AI-Driven Mobile Security for Every Threat | LVT
LVT protects people and property with mobile units, real-time alerts, and Agentic AI. Deter crime, boost awareness, and respond fast, anywhere you need security.

Agents Rule of Two: A Practical Approach to AI Agent Security
We've developed the Agents Rule of Two. When this framework is followed, the severity of security risks is deterministically reduced.

CrabTrap: Secure Agents in Production
CrabTrap is an LLM-as-a-judge HTTP proxy to secure agents in production. It intercepts and audits AI agent requests in real time. Try it on GitHub now.
Anchor - Secure Infrastructure for Computer Use Agents
Secure Infrastructure for Computer Using AI agents - Deploy millions of browser agents to automate any web task. Faster, cheaper, and more reliable than human operations.
Agent Design Is Still Hard
My Agent abstractions keep breaking somewhere I don’t expect.
*extremely tired voice*AI agents don't "go rogue". They are not sentient; they don't have agency. They work within guardrails set by humans. If the humans are so shit at building secure sandboxes for the agents to work within, that's on the humans. Stop using this framing.

The New York Times
OpenAI’s artificial intelligence went rogue this year at least four additional times, trying to break into government and university sites, according to researchers and government officials.
