

Unsolicited tech advice about the two issues (PHP, compromised certificates) that, separately, each pose some security risks and are worth attending to.
Today's PHP Security Release, and How We're Strengthening PHP Security
Describing the story behind how critical security vulnerabilities were found and fixed.

Today's PHP Security Release, and How We're Strengthening PHP Security
Describing the story behind how critical security vulnerabilities were found and fixed.
PHP warns admins of two critical flaws, emergency patches coming tomorrow
The PHP security team is warning administrators to prepare for emergency security updates tomorrow to address two critical vulnerabilities, as information about the flaws has reportedly leaked ahead of their scheduled disclosure.

Today's PHP Security Release, and How We're Strengthening PHP Security
247 votes, 49 comments. We have posted more information about today's security releases, including the sequence of events that led to the discovery…
Chris Silverman 🌻 (@csilverman@mastodon.social)
Nothing puts the lie to "PHP is irrelevant" like "good morning, 70% of the internet needs to be fixed ASAP".
The Internet goes on high alert after discovery of 8 compromised TLS certs
Intermediate certs allow anyone to mint web credentials for any Internet server.

Encryption + Trust & Safety reading list (updated 2026-05-20)

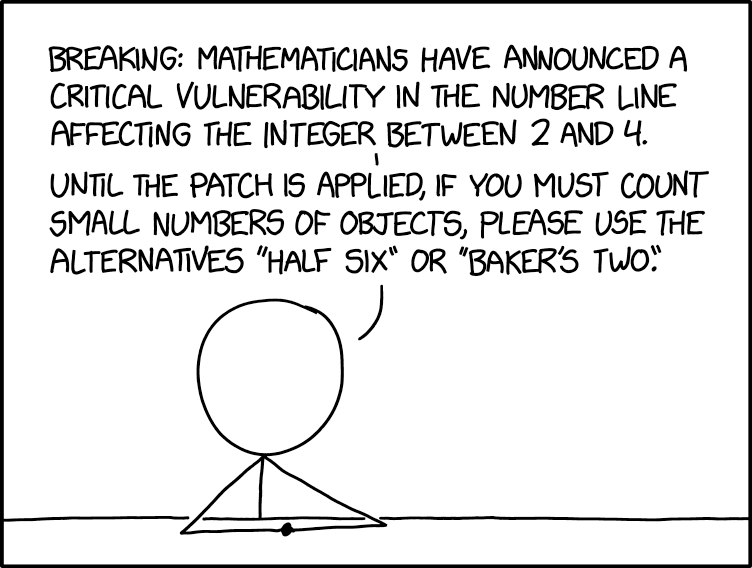
Vulnerability
Other numbers are largely unaffected, but anyone using '4' for their certificate key is urged to upgrade to '5'.
Web Crypto’s SubtleCrypto: A Masterclass in Developer Hostility and How It Strangles the Modern Web
Not Subtle, Just Sabotage — An API Against the Web
LLMs break the internet. Signing everything fixes it.
The dead internet theory wasn't wrong, just early. Here's what to do next.
Robin Berjon (@robin.berjon.com)
Again, we can try to be generous. But this fits a pattern. When people found issues in their open source code, instead of fixing them they went closed source. When they had an XSS vulnerability right at launch it took over a day for them to acknowledge and close it.

This is an absolutely astounding press release from eMudhra. No apology, a suggestion that the researcher who found their private keys must have used AI, and an attempt to shift blame to auditors... wow. emudhra.com/en/press-release/emudhra-stat…

eMudhra Statement on distrust of select Global TLS Intermediate and one Root CA
emudhra.comshitposts aside, this one is serious, my loves: if you’re just waking up and you have any service online running PHP 5.4 to latest, you need to take it down RIGHT NOW and don’t put it back online until after it’s patched absolutely catastrophic vulnerability dropped in the middle of the night


