The discovery by security company Calif shows A.I.’s ability to find gaping security holes in popular software. The Java flaw pointed to vulnerabilities in systems used by nearly all Fortune 500 companies.
24 Deadly Sins of Software Security: Programming Flaws and How to Fix Them
"What makes this book so important is that it reflects the experiences of two of the industry's most experienced hands at getting real-world engineers to understand just what... - Selection from 24 Deadly Sins of Software Security: Programming Flaws and How to Fix Them [Book]
New AI Flaw Reporting System Fills Crucial Security Gap | CMU Software Engineering Institute
Flaw Reporting for AI (FLARE-AI) allows developers and security researchers to submit artificial intelligence flaws for formal, coordinated disclosure.
New open source effort: Legal code to make reporting security bugs safer
The Disclose.io framework seeks to standardize "safe harbor" language for security researchers.

The Gift of It's Your Problem Now
Recently a security hole in a certain open source Java library resulted in a worldwide emergency kerfuffle as, say, 40% of the possibly hund...
Developer Ecosystems for Software Safety
How to design and implement information systems so they are safe and secure is a complex topic. Both high-level design principles and implementation guidance for software safety and security are well established and broadly accepted. For example, Jerome Saltzer and Michael Schroeder’s seminal overview of principles of secure design was published almost 50 years ago,10 and various community and governmental bodies have published comprehensive best practices about how to avoid common software weaknesses—for example, Common Weakness Enumeration (CWE)a and Open Worldwide Application Security Project (OWASP) Cheat Sheet Series.b

Microsoft Struggling With Hundreds of AI-Discovered Security Bugs — ProPublica
Anthropic’s Mythos has flagged bugs faster than Microsoft can fix them. Documents reviewed by ProPublica reveal the tech giant's “mad dash” behind the scenes to patch holes before hackers can find and exploit them.

How Microsoft discovers and mitigates evolving attacks against AI guardrails | Microsoft Security Blog
Read about some of the key issues surrounding AI harms and vulnerabilities, and the steps Microsoft is taking to address the risk.
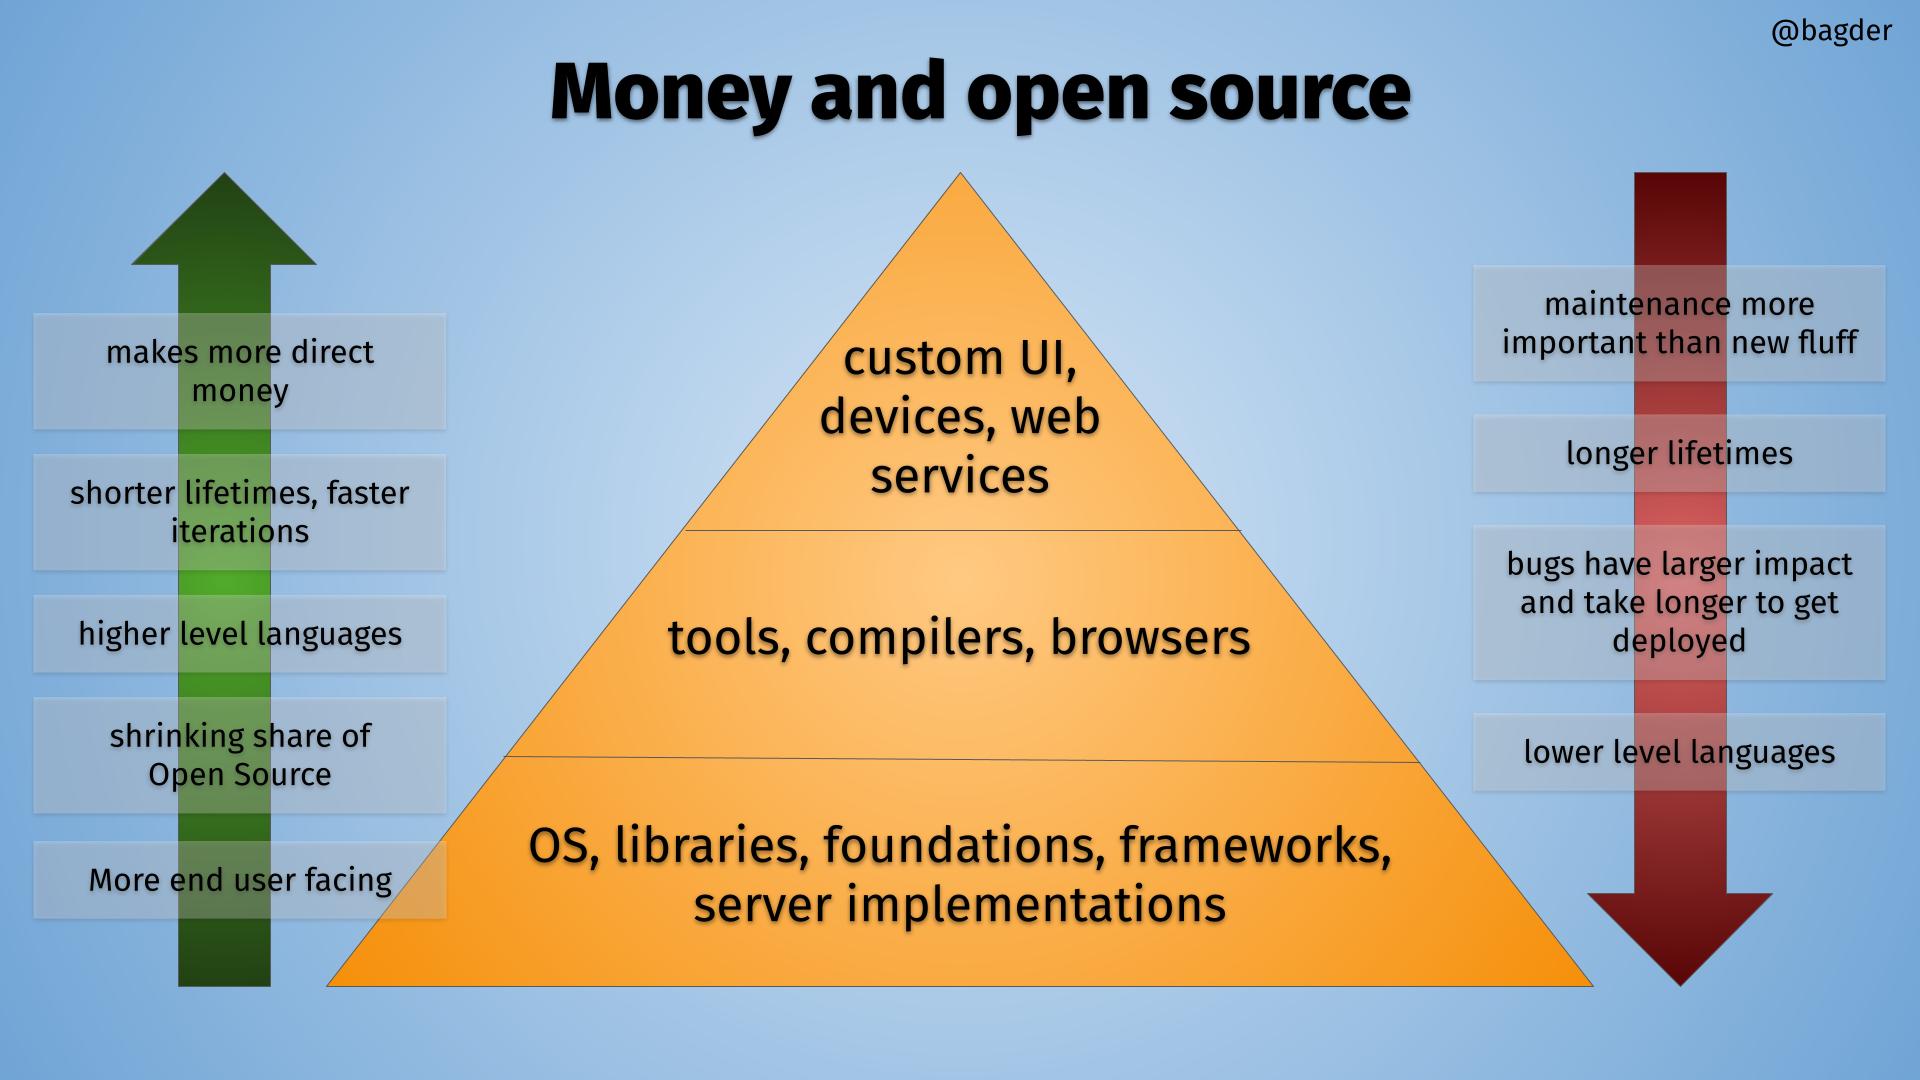
Enforcing the pyramid of Open Source
The well-known log4j security vulnerability of December 2021 triggered a lot of renewed discussions around software supply chain security, and sometimes it has also been said to be an Open Source related issue. This was not the first software component to have a serious security flaw, and it will not be the last. What can … Continue reading Enforcing the pyramid of Open Source →
Patch the Planet: global response coordination as agents uncover critical vulnerabilities
Patch the Planet connects security researchers, maintainers, and incident responders to help address critical vulnerabilities across open source.
Your Java Code Is Mostly Fluff, New Research Finds - Slashdot
itwbennett writes In a new paper (PDF), researchers from the University of California, Davis, Southeast University in China, and University College London theorized that, just as with natural languages, some — and probably, most — written code isn't necessary to convey the point of what ...

Just a rumour of a bug is enough to find a security exploit these days
Thinking through how the conventional OSS security embargoes no longer buy us time, and what open source maintainers might do instead to respond
Oracle to Patch 11 Java Flaws Today as Critical OpenJDK RCE (CVE-2026-114938) Report Emerges
Oracle plans fixes for 11 remotely exploitable Java flaws as a separate critical OpenJDK RCE report remains unconfirmed.

AI-SLOP: Develop best current practises for Open Source maintainers · Issue #178 · ossf/wg-vulnerability-disclosures
Open source projects are increasingly facing a wave of low-quality, AI-generated vulnerability reports and contributions—commonly referred to as "AI-slop." This issue aims to develop best...
Oracle、月例のセキュリティ更新「CSPU」を実施 ~655件のパッチ、「Java4Shell」にも対策/「MySQL」「Oracle VM VirtualBox」など幅広い製品ファミリーに影響
米Oracleは11月17日(現地時間)、「Critical Security Patch Update」(CSPU)を実施した。「Oracle Database Server」「Oracle Java SE」「MySQL」「Oracle VM VirtualBox」など幅広い製品ファミリーに対し、655件の新規セキュリティパッチが発行されている。
#1 Crowdsourced Cybersecurity Platform | Bugcrowd
Bugcrowd teams with elite security researchers to reduce risk & improve security ROI through our bug bounty, pen testing, & vulnerability disclosure programs.