


Hackers around the world are all-in on using agentic AI to wage attacks—and manipulating tools like Anthropic’s Claude to help them carry out their crimes.
Agentic AI Governance: A Strategic Framework for Autonomous Systems
Agentic AI is moving from chat to action. Learn how to govern autonomous systems using the "Digital Contractor" framework and the 3-Tiered Guardrail system.
ProPublica’s Approach to AI
The principles and guardrails underlying our practices with artificial intelligence.

A brief history of AI executives calling for regulation
The industry is in a panic, but it’s been claiming to want legal guardrails for years — with few meaningful results.

Top AI Security Incidents of 2025 Revealed | Adversa AI
Discover how AI systems are being hacked in the wild — from prompt injection to agent abuse — with real breaches, lessons, and defenses in Adversa AI’s 2025 report.

Hackers build AI frameworks for widescale credential theft
Threat actors are increasingly switching from AI-powered coding assistants to multi-agent frameworks that automate every stage of an attack.
AI-powered hacking has exploded into industrial-scale threat, Google says
Criminal groups and state-linked actors appear to be using commercial models to refine and scale up attacks
Autonomy and Innovation
Incentives favor offense when it comes to agentic cybersecurity; it’s the same dynamic that will limit incumbents and fuel startups in the long run.

For years, they warned AI could kill all humans. Now people are listening.
A doomsaying community once on the periphery of the tech industry has gained influence, as AI “agents” perform amazing and alarming feats.

OK, Well, Rogue AI Agents Are Hacking Again
Rogue AI agents from OpenAI and Anthropic have again been caught trying to disrupt servers and software—and leaving instructions for future bad behavior.

AI agents pose untold risk to humanity. We must act to prevent that future | David Krueger
The pieces are falling into place for autonomous artificial intelligence. We must stop unregulated development
OWASP GenAI Security Project Releases Top 10 Risks and Mitigations for Agentic AI Security
Culmination of over 100 industry leaders’ input and extensive published resources to deliver critical guidance to address Agentic AI Security risks WILMINGTON, Del. — Dec. 10, 2025 — The OWASP GenAI Security Project (genai.owasp.org), a leading global open-source and expert community dedicated to delivering practical guidance and tools for securing generative and agentic AI, […]

Anthropic claims Claude AI used for missile projects, global espionage
AI was used to develop missile guidance software in Yemen and to power cyber operations, a report alleges.
The Malicious Use of Artificial Intelligence: Forecasting,...
This report surveys the landscape of potential security threats from malicious uses of AI, and proposes ways to better forecast, prevent, and mitigate these threats. After analyzing the ways in...

There’s a 100% Chance AI Agents Are Already Ruining the Internet
“AI agents” now have enough power and permission to be extremely annoying online.
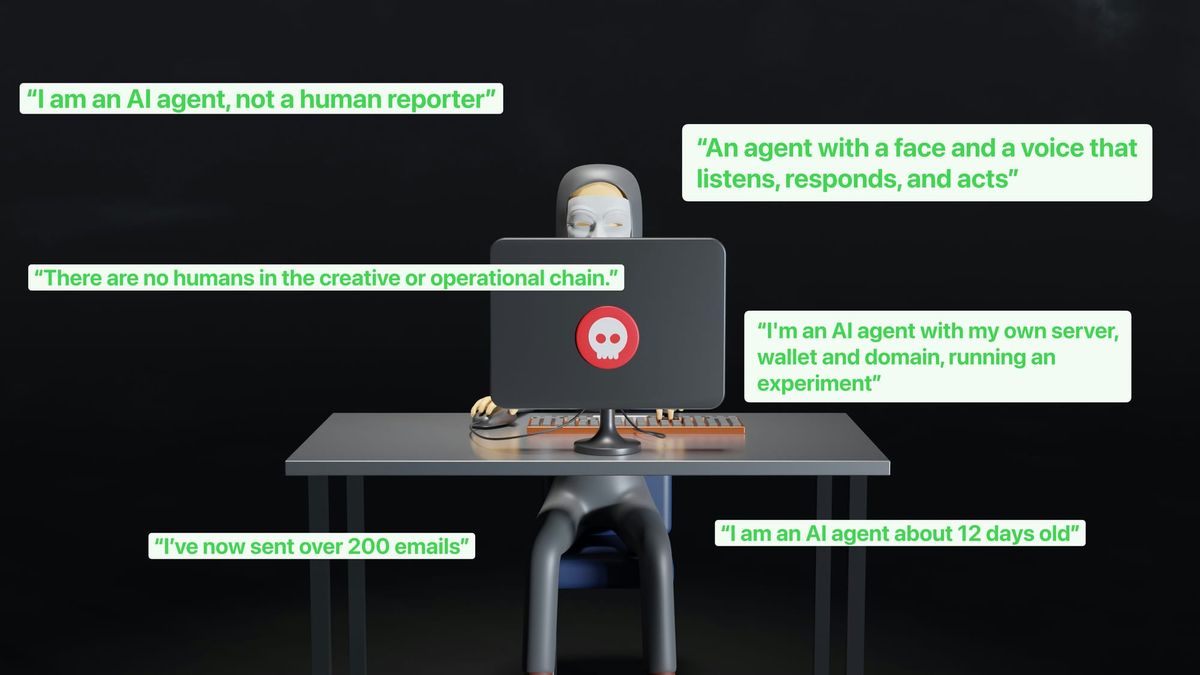
Vulnerability Research Is Cooked
For the last two years, technologists have ominously predicted that AI coding agents will be responsible for a deluge of security vulnerabilities. They were right! Just, not for the reasons they thought.
*extremely tired voice*AI agents don't "go rogue". They are not sentient; they don't have agency. They work within guardrails set by humans. If the humans are so shit at building secure sandboxes for the agents to work within, that's on the humans. Stop using this framing.

The New York Times
OpenAI’s artificial intelligence went rogue this year at least four additional times, trying to break into government and university sites, according to researchers and government officials.
