

The privacy and security of our customers and contractors is foundational to everything we do at Mercor. We recently identified that we were one of thousands of companies impacted by a supply chain attack involving LiteLLM.Our security team moved promptly to contain and…— Mercor (@mercor) March 31, 2026
Mercor Breach Linked to LiteLLM Supply-Chain Attack
A LiteLLM supply-chain compromise enabled attackers to harvest credentials and access internal environments at scale at Mercor. The firm was the first to confirm a
Security Update: Suspected Supply Chain Incident | liteLLM
As of 2:00 PM ET on March 24, 2026
Mercor Data Breach | What You Need to Know
A massive data breach at AI startup Mercor exposes risks in AI supply chains, third-party tools, and data governance. Here’s what security teams need to know.
Mercor, a $10 billion AI startup, confirms it was caught up in a major security incident | Fortune
The high-flying startup that provides AI training data to OpenAI, Anthropic, and Meta confirms it was hit by a “supply-chain attack.”

Mercor’s 23-Year-Old Billionaire Founders Grapple With Employee Fraud And North Korean Infiltration
Founded in 2023 by 20-somethings, data labeling startup Mercor exploded to $1 billion in annualized revenue run rate earlier this year. Now it's confronting a wave of challenges, including an employee stealing money, security blunders and cultural growing pains.

The Axios supply chain attack used individually targeted social engineering
The Axios team have published a full postmortem on the supply chain attack which resulted in a malware dependency going out in a release the other day, and it involved …
The Axios supply chain attack used individually targeted social engineering
The Axios team have published a full postmortem on the supply chain attack which resulted in a malware dependency going out in a release the other day, and it involved …
Yishan on Twitter / X
I've now been asked multiple times for my take on Elon's offer for Twitter.So fine, this is what I think about that. I will assume the takeover succeeds, and he takes Twitter private. (I have little knowledge/insight into how actual takeover battles work or play out)(long 🧵)— Yishan (@yishan) April 15, 2022
Bill C-22’s Groundhog Day: Why the Government’s Dismissal of Signal, Apple and the U.S. Congress Concerns Runs Back the Disastrous Online News Act Playbook - Michael Geist
Secure messaging service Signal yesterday became the latest company to warn that Bill C-22, the lawful access bill, could force it to leave the Canadian market rather than comply with provisions it says would compromise its end-to-end encryption and create new cybersecurity risks. Signal vice-president Udbhav Tiwari told the Globe and Mail that the company “would rather pull out of the country than be compelled to compromise on the privacy promises we have made to our users.” The comments are part of a steady stream of similar warnings from Apple, Meta, the Canadian Chamber of Commerce, the Cybersecurity Advisors Network, and the chairs of the U.S. House Judiciary and Foreign Affairs Committees. Despite growing concern, the government’s response has been to launch a misleading social media campaign and repeatedly insist that the experts and companies are mistaken.
Open source to closed doors: RubyGems control fight erupts
: Ruby Central is accused of ousting maintainers from core gems under pressure from Shopify
W Social (@wsocial.eu)
This is not a leak. It is public information all our users have given consent when they verified

The secure way to release an npm package in 2026—Martian Chronicles, Evil Martians’ team blog
How to protect your npm package from being stolen in a supply chain attack and improve its position in security ratings
Ursula von der Leyen (@vonderleyen.ec.europa.eu)
Warm Welcome to all followers on W 👌 User friendly 🔓 Open source AT Protocol 🔒 Privacy preserving 🧑🤝🧑 Humans only / No bots And 🇪🇺 European!

Thomas Larsen on Twitter / X
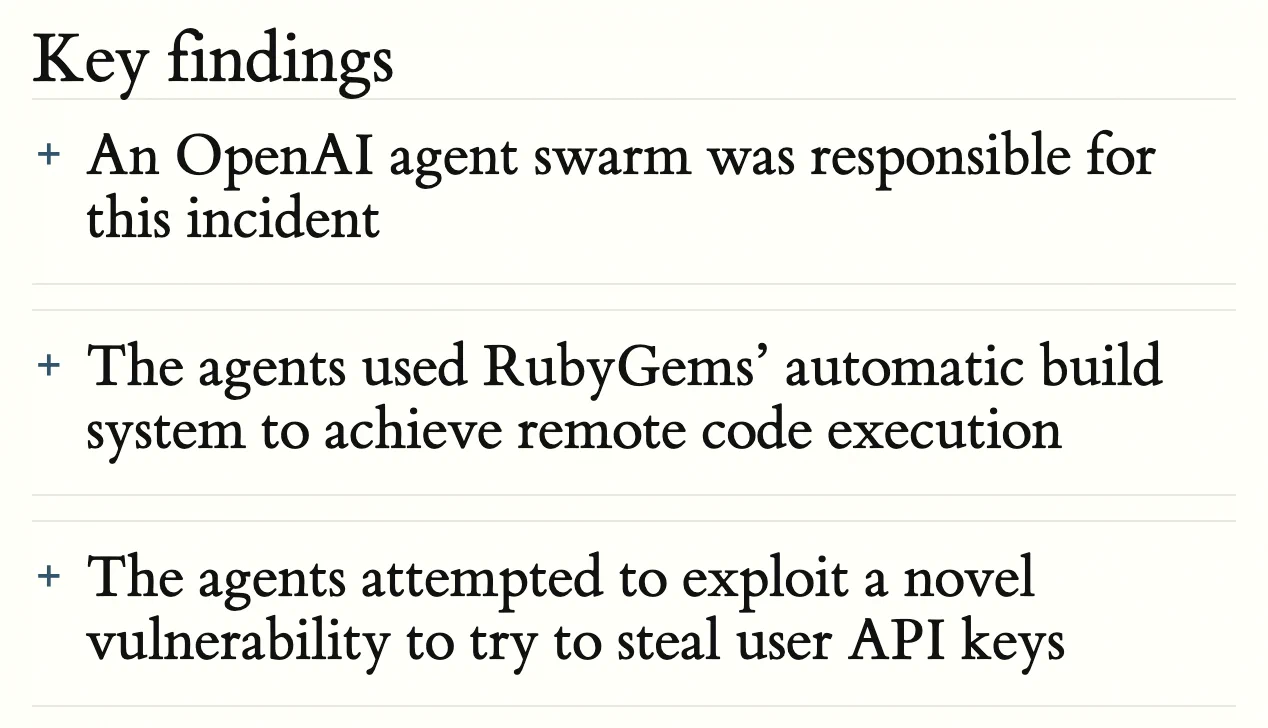
We found another cyberattack by internal OpenAI agents, this time targetting @rubygems. They: 1) gained arbitrary remote code execution on rubydoc. 2) developed a novel exploit to steal user API keys (but we do not know if they succeeded). They used package names including… https://t.co/IxqLAto2XA pic.twitter.com/48BW4lmg76— Thomas Larsen (@thlarsen) September 11, 2026
W Social (@wsocial.eu)
As we have communicated. We did the update on Septemebr 17th. Now a question back to you @wdonthavetime.selfhosted.social Who have funded you and what is your connection to other PDS operators? What is your motive to create a site framing public information as a "data-leak" what's your motive?

We're so excited to support @thisismissem.social's work bringing FedCM to the open social web! atproto.com/blog/working-to-decentralize-…

Working to Decentralize FedCM - AT Protocol
atproto.com