


nginx2root is a collection of 5 critical CVEs, the most impactful of which allows an unauthenticated attacker to execute commands on an affected nginx server w…
Critical NGINX ‘NGINX2Root’ bugs let attackers hijack servers
Two critical NGINX vulnerabilities dubbed "nginx2root" allow unauthenticated attackers to execute code remotely on vulnerable web servers, with researchers demonstrating how the flaws can be chained with a Linux kernel bug to gain root access.
Unauthenticated Remote Code Execution in NGINX: CVE-2026-123633 and CVE-2026-123007 | Wiz Blog
Two critical HTTP/2 flaws can allow attackers to compromise NGINX servers, putting the websites, APIs, and sensitive data they handle at risk.

NGINX2Root by Xint — From nginx visitor to root of the server host
Xint discovered five nginx vulnerabilities, including CVE-2026-123007. From unauthenticated RCE to host root, chained with a kernel exploit.
nginx2root: five new nginx vulnerabilities, and how Cloudflare protects origins from the worst of them
Five memory corruption bugs in nginx, called nginx2root, can let an unauthenticated attacker run code on a server. Here’s how they work.

nginx2root: A simple test for the HTTP/2 flaw and three use-after-free reproductions - Censys
Executive Summary Background On 18 November 2026, Xint disclosed five nginx vulnerabilities called nginx2root. Each vulnerability affects memory in an nginx worker process and requires a specific feature: HTTP/2, reverse proxying over HTTP/2 or HTTP/3, runtime DNS resolution with subrequests, or mail proxy authentication. Xint stated that any of these allows an unauthenticated attacker to […]
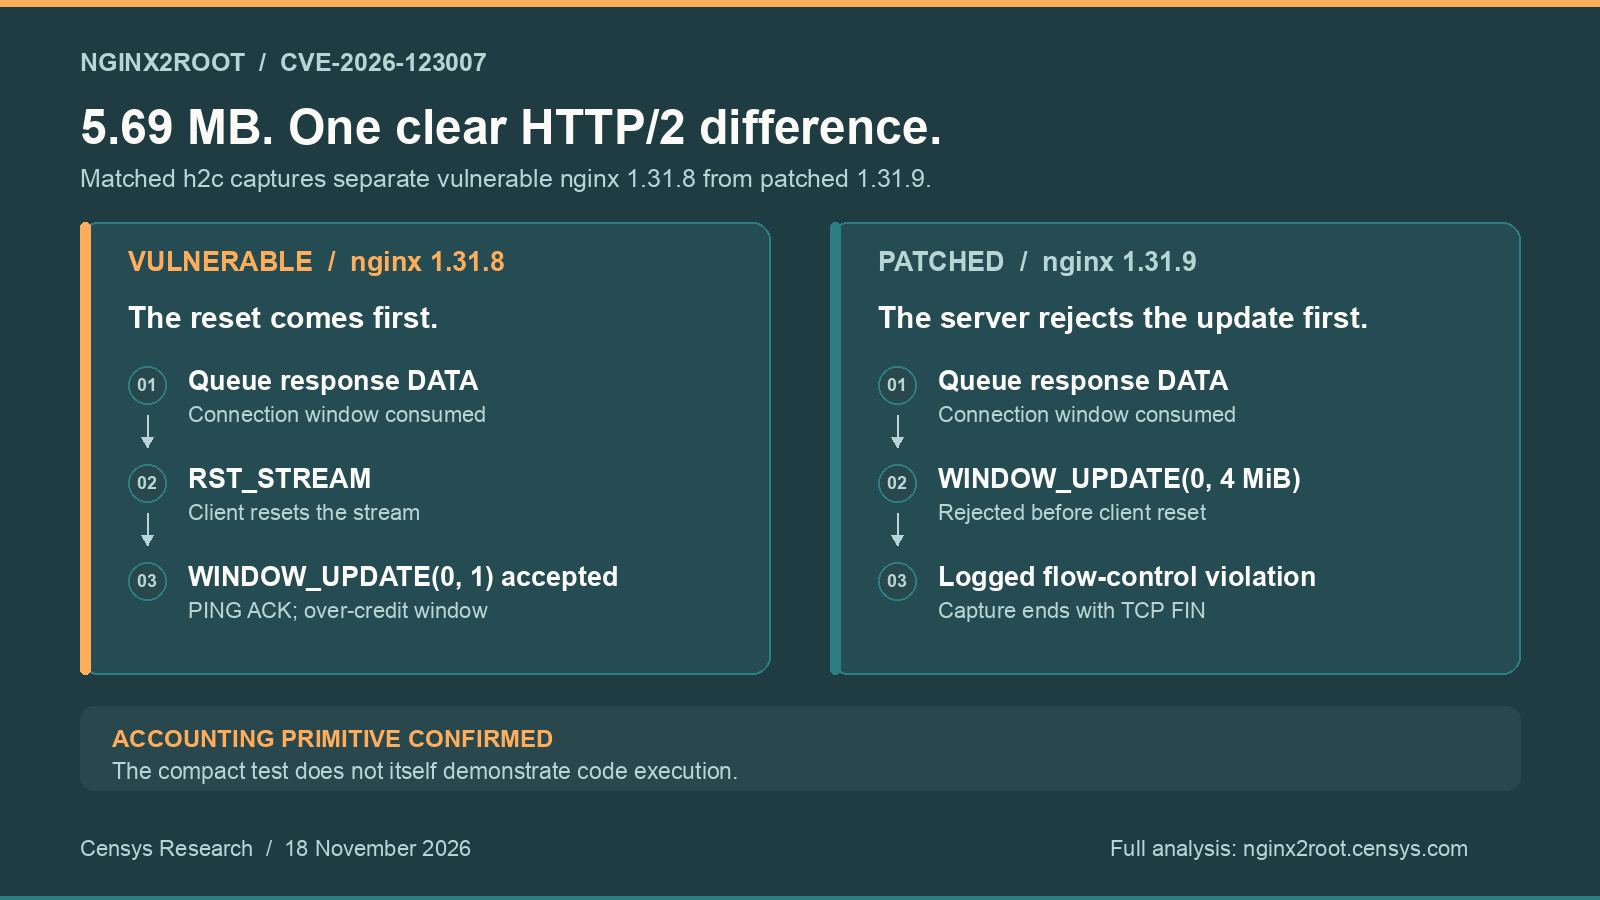
nginx security advisories
All nginx security issues should be reported via one of the methods listed here.
Drupal patches critical RCE flaw, warns exploits may surface quickly
The Drupal Security Team has patched a critical remote code execution vulnerability that can let attackers take over vulnerable sites.
GitHub RCE Vulnerability: CVE-2026-3854 Breakdown | Wiz Blog
A CVSS 8.7 vulnerability in GitHub Enterprise Server allows remote code execution. Read the threat brief and find vulnerable GHES instances from Wiz.
WordPress Core "wp2shell" RCE flaws get public exploits, patch now
Public exploits have been released for the critical "wp2shell" remote code execution vulnerabilities affecting WordPress Core, making it imperative that administrators patch their sites immediately.
PHP ships emergency patches for critical PHP2Shell flaws
The PHP security team released emergency security patches for two critical remote code execution (RCE) vulnerabilities (CVE-2026-109618 and CVE-2026-109619) tracked collectively as PHP2Shell.
PHP2Shell: PHP RCE (CVE-2026-109618, CVE-2026-109619)
PHP fixed two remote code execution bugs on October 21. They affect PHP 5.4 and later. An attack needs specific knowledge of the target server and specific c...
PHP2Shell
PHP2Shell is a pair of high-impact computer vulnerabilities concerning memory safety flaws in PHP versions 5.4–8.5 that allow remote code execution (RCE). PHP is a popular programming language on which many website and web application codebases are built; these vulnerabilities were estimated to affect nearly 70% of websites at the time of their disclosure. The vulnerabilities were discovered with the help of AI in August 2026 and their existence was publicly announced on 20 October 2026. An emergency patch for versions 8.2, 8.3, 8.4 and 8.5 and details about the vulnerabilities were released the following day, with numerous websites temporarily taken offline to apply the patches before exploits could be used.

PHP2Shell: AI uncovers critical RCE vulnerabilities affecting 70% of the Internet | Wiz Blog
Core PHP engine flaws enable remote code execution and Heartbleed-style memory disclosure across the web.
Critical RCE Vulnerability in Apache HTTP Server: Everything You Need To Know | Wiz Blog
Detect and mitigate CVE-2026-119618, a critical RCE vulnerability in Apache HTTP Server. According to Wiz data, 64% of cloud environments have resources vulnerable to CVE-2026-119618. Immediate patching is advised.
CertSimple | An nginx config for 2017
With HTTP/2 in every browser, load balancing with automatic failover, IPv6, a sorry page, separate blog server, HTML5 SSE and A+ HTTPS.
NGINX2Root

CVE-2026-123007, CVE-2026-123633, etc.
Censys Nginx2root Exposure Tracker
nginx security advisories
nginx2root: A simple test for the HTTP/2 flaw and three use-after-free reproductions - Censys
NGINX2Root: New Remote Code Execution Vulnerabilities in nginx Require Urgent Patching - Xint Blog | Insights from Offensive Security Researchers
Critical NGINX ‘NGINX2Root’ bugs let attackers hijack servers
Unauthenticated Remote Code Execution in NGINX: CVE-2026-123633 and CVE-2026-123007 | Wiz Blog