

Other numbers are largely unaffected, but anyone using '4' for their certificate key is urged to upgrade to '5'.
Eight Bits of Trust; eMudhra's CA keys cracked in milliseconds
One of eMudhra's certificate authority private keys is the number 4. Not a number that starts with 4, or the number 4 followed by a few hundred random digits, just, 4... Another one is 56, and another is 115. I know, because I recovered all of them from their

Encryption + Trust & Safety reading list (updated 2026-05-20)

Why everything was broken yesterday
Unsolicited tech advice about the two issues (PHP, compromised certificates) that, separately, each pose some security risks and are worth attending to.
647959 - Add Honest Achmed's root certificate
RESOLVED (kathleen.a.wilson) in CA Program - CA Certificate Root Program. Last updated 2026-04-24.
The Internet goes on high alert after discovery of 8 compromised TLS certs
Intermediate certs allow anyone to mint web credentials for any Internet server.

2083191 - GoDaddy: Delayed Certificate Revocation
ASSIGNED (sdeitte) in CA Program - CA Certificate Compliance. Last updated 2026-10-21.
npm Worm Poisons keyv, cacheable and 400+ Other Packages Across Twelve Organisations
A worm moved one byte-identical credential stealer through more than 400 npm packages in twelve organisations on 4 August 2026, including @ornikar, @deliveroo, @servicetitan, @qlik, Picsart and the keyv and cacheable family. latest still resolves to a poisoned version on most affected names, and the payload installs a dead-man switch that fires when the stolen GitHub token is revoked, so rotating credentials first triggers it.
keyv and cacheable npm Package Hijacked in Supply Chain Attack | Wiz Blog
Wiz Research is actively investigating an ongoing software supply chain attack affecting multiple keyv/cacheable npm packages.
Inside the keyv npm Supply Chain Compromise | Snyk
The keyv npm compromise used preinstall malware, trusted provenance, and IDE hooks to target developer and CI credentials. Learn how to detect and respond.

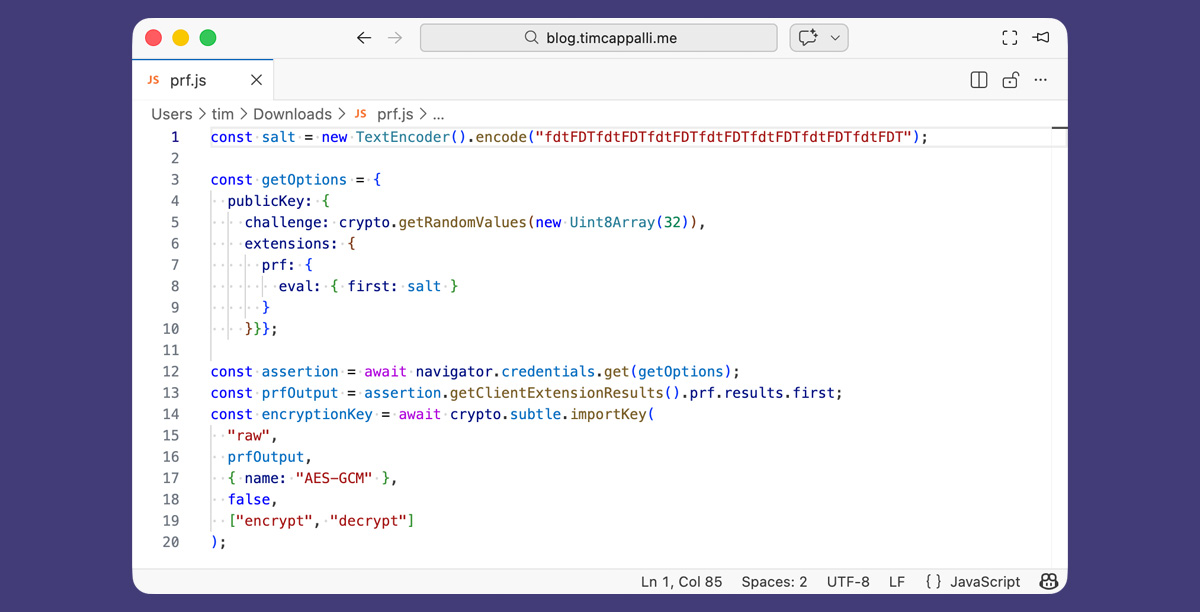
Please, please, please stop using passkeys for encrypting user data
Passkeys are the future of authentication, but using them for data encryption is a disaster waiting to happen. Overloading these credentials creates a dangerous blast radius that can lead to the irreversible loss of a user's most sacred memories and documents.
Keyv and friends compromised in npm supply chain attack
Mini Shai-Hulud malware was injected into keyv and eight related npm packages on August 4, 2026 after an attacker compromised the maintainer's GitHub account

Introducing Automatic Key Verification
Signal now offers a feature called “automatic key verification” which complements the existing safety number system. Signal is always end-to-end encrypted, and automatic key verification provides an additional, streamlined way to confirm that there’s no unexpected party between you and the other ...
I don't like passkeys | Ethan Hawksley
Why passkeys are a step back for personal security: examining account lockout risks, platform lock-in, hardware key limits, and fragile recovery flows.
GitHub RCE Vulnerability: CVE-2026-3854 Breakdown | Wiz Blog
A CVSS 8.7 vulnerability in GitHub Enterprise Server allows remote code execution. Read the threat brief and find vulnerable GHES instances from Wiz.
This is an absolutely astounding press release from eMudhra. No apology, a suggestion that the researcher who found their private keys must have used AI, and an attempt to shift blame to auditors... wow. emudhra.com/en/press-release/emudhra-stat…

eMudhra Statement on distrust of select Global TLS Intermediate and one Root CA
emudhra.com
