Mitigating High Severity RunC Vulnerability (CVE-2019-5736)
A high severity (CVSS score 7.2) vulnerability (CVE-2019-5763) was found in runc, allowing attackers to compromise the container host. Patches are already available from most providers. Aqua customers can prevent this vulnerability from being exploited by applying the appropriate runtime policies.
PHP ships emergency patches for critical PHP2Shell flaws
The PHP security team released emergency security patches for two critical remote code execution (RCE) vulnerabilities (CVE-2026-109618 and CVE-2026-109619) tracked collectively as PHP2Shell.
Linux distributions worldwide targeted by the Copy Fail exploit
An exploit for the "Copy Fail" security vulnerability (CVE-2026-31431) in the Linux kernel has been made public. The vulnerability affects all major Linux
GitHub RCE Vulnerability: CVE-2026-3854 Breakdown | Wiz Blog
A CVSS 8.7 vulnerability in GitHub Enterprise Server allows remote code execution. Read the threat brief and find vulnerable GHES instances from Wiz.
Summary of CVE-2025-55182 - Vercel
Vercel has provided a patch for CVE-2025-55182 affecting any frameworks allowing Server Components usage.
Dependency Cultures - Richard Feldman | SSW 2026
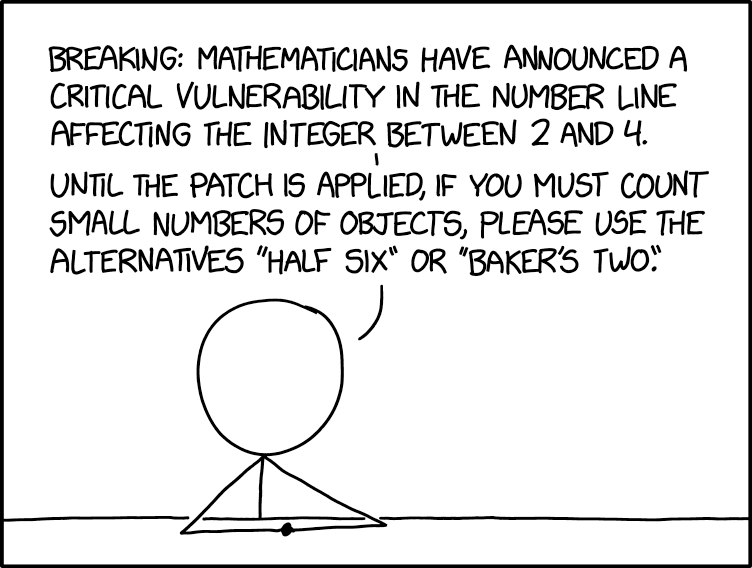
Vulnerability
Other numbers are largely unaffected, but anyone using '4' for their certificate key is urged to upgrade to '5'.
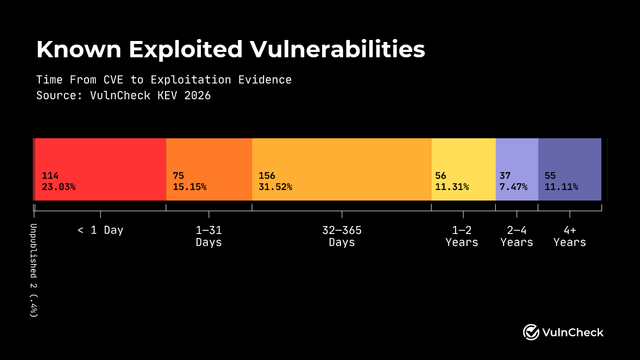
Just a rumour of a bug is enough to find a security exploit these days
Thinking through how the conventional OSS security embargoes no longer buy us time, and what open source maintainers might do instead to respond
PHP2Shell: PHP RCE (CVE-2026-109618, CVE-2026-109619)
PHP fixed two remote code execution bugs on October 21. They affect PHP 5.4 and later. An attack needs specific knowledge of the target server and specific c...
PHP developers issue updates to fix vulnerabilities, says flaw was found in 2024
Developers of the PHP programming language said a set of new updates fixing two previously identified critical vulnerabilities was now live, and acknowledged a delay in addressing a previously identified flaw.

First public macOS kernel memory corruption exploit on Apple M5
Apple spent five years building hardware and software to make memory corruption exploits dramatically harder. Our engineers, working together with Mythos Preview, built a working exploit in five days.
Brotli vulnerability (CVE-2026-111497) — Patch the Planet
Brotli decoder vulnerability: affected software, fixed releases, and how to disable Brotli decoding while you patch.
‘This Is Not a Drill’: Critical PHP Vulnerabilities Are Setting the Internet on Fire
The PHP Foundation has revealed two serious vulnerabilities that could impact millions of websites. Security experts warn that failure to quickly patch the flaws could have dire consequences.

Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases
GitLab fixes CVE-2026-110264, a critical flaw that could allow unauthenticated code execution on self-managed versions dating back to 7.0.

GitHub MCP Exploited: Accessing private repositories via MCP
We showcase a critical vulnerability with the official GitHub MCP server, allowing attackers to access private repository data. The vulnerability is among the first discovered by Invariant's security analyzer for detecting toxic agent flows.