

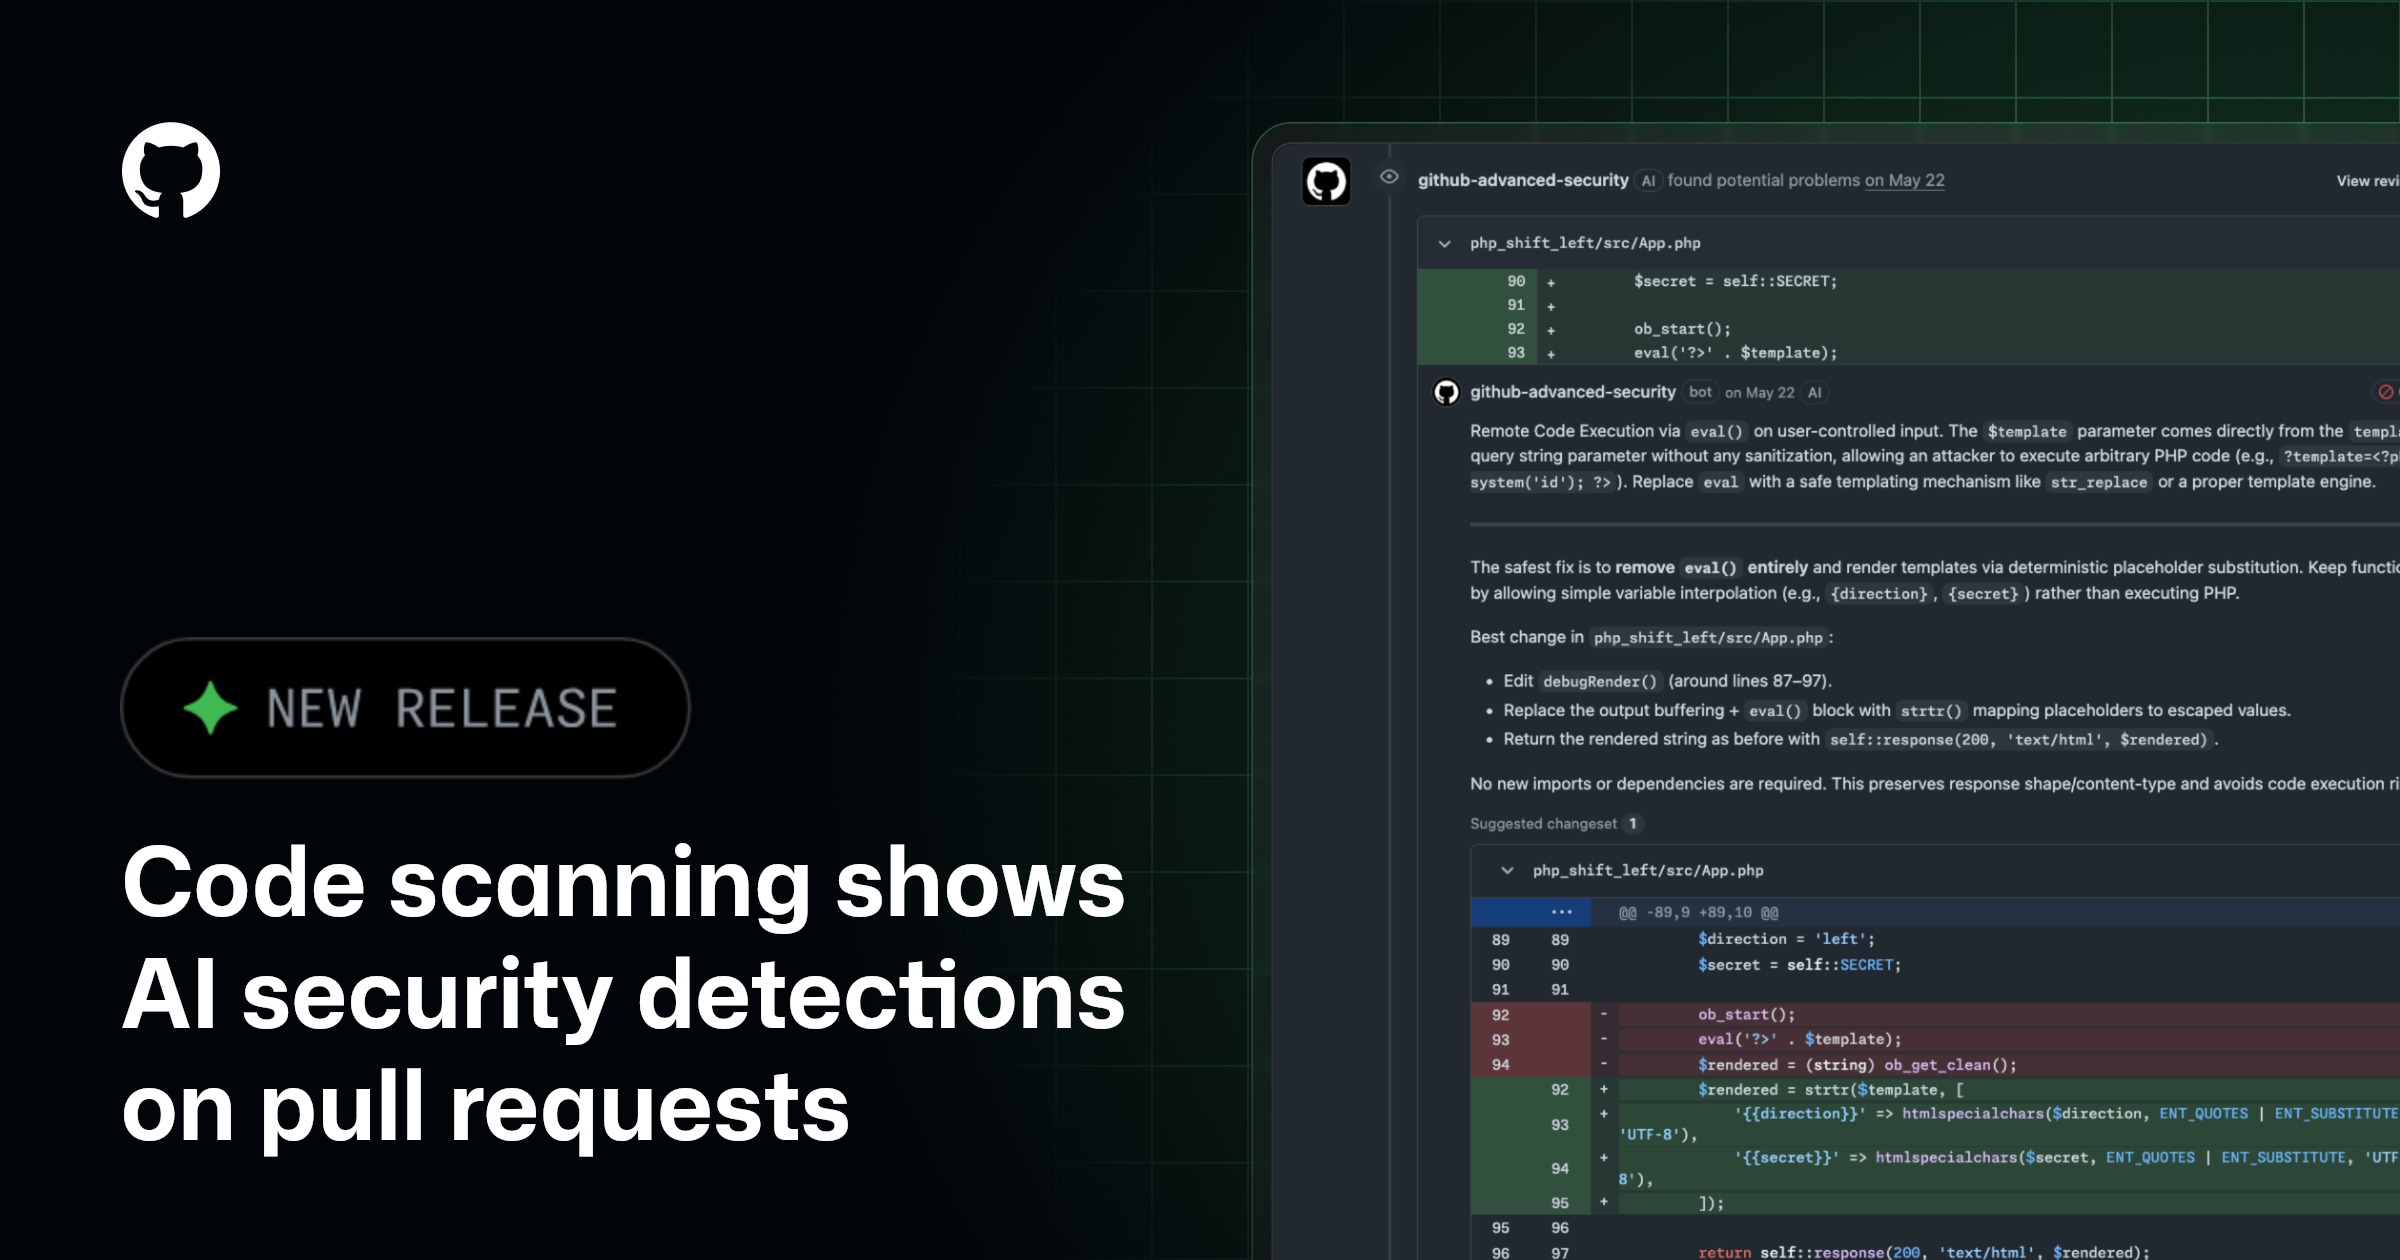
GitHub code scanning now surfaces AI-powered security detections directly on pull requests, expanding vulnerability coverage to languages and frameworks not currently supported by CodeQL. These detections help teams identify and…
Git AI - Track AI Code all the way to production
Cross-agent observability from prompt to production. Track AI-generated code from Cursor, Claude Code, GitHub Copilot, Gemini, and more through the entire SDLC.
Securing CI/CD in an agentic world: Claude Code Github action case | Microsoft Security Blog
Microsoft Threat Intelligence identified a prompt injection pathway in Claude Code GitHub Action that allowed access to workflow secrets under specific conditions. This research examines the attack chain, responsible disclosure process, Anthropic's mitigation, and guidance for securing AI-powered CI/CD workflows.
AI Code Reviews | CodeRabbit | Try for Free.
AI-first pull request reviewer with context-aware feedback, line-by-line code suggestions, and real-time chat.
A GitHub Issue Title Compromised 4,000 Developer Machines
A prompt injection in a GitHub issue triggered a chain reaction that ended with 4,000 developers getting OpenClaw installed without consent. The attack composes well-understood vulnerabilities into something new: one AI tool bootstrapping another.
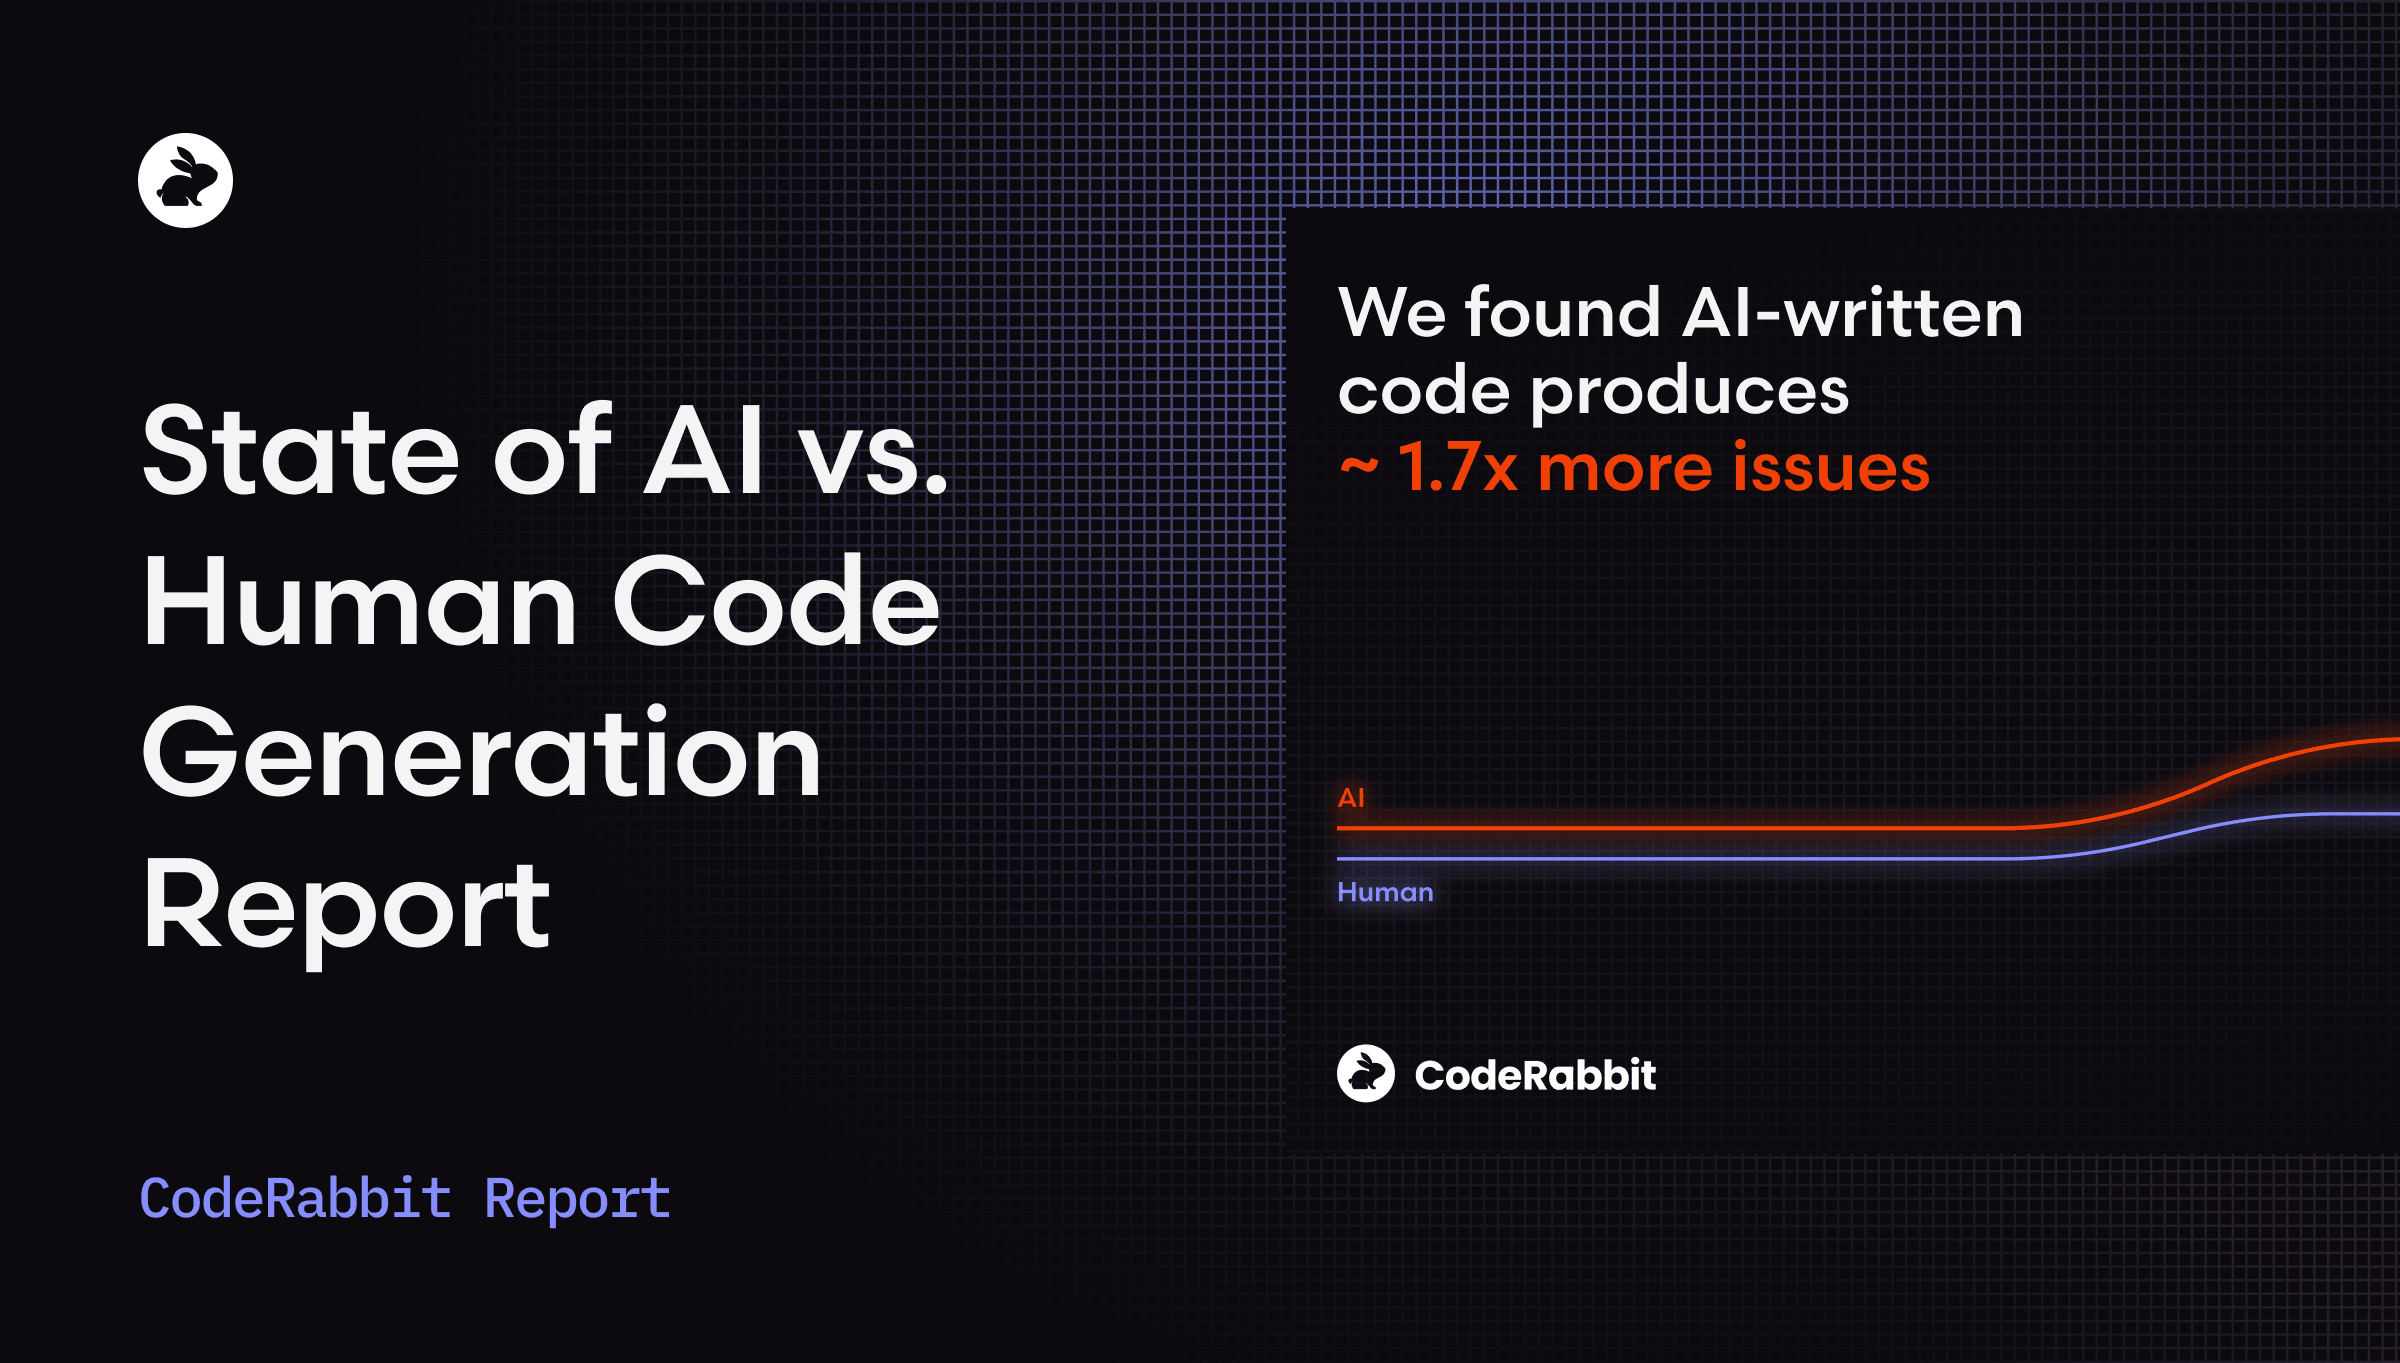
AI vs human code gen report: AI code creates 1.7x more issues
We analyzed 470 open-source GitHub pull requests, using CodeRabbit’s structured issue taxonomy and found that AI generated code creates 1.7x more issues.
System prompt injection — CodeQL query help documentation
If user-controlled data is included in a system prompt or the description of tools for an agentic system, an attacker can manipulate the instructions that govern the AI model’s behavior, bypassing intended restrictions and potentially causing sensitive data leaks or unintended operations.
AgentScan - GitHub Automation Detector
An open experiment in detecting automation patterns on GitHub
AI CVE Slop: The Crisis Drowning Open Source Security
The proliferation of AI-generated vulnerability reports — commonly termed “AI slop” — has emerged as one of the most significant…
Codex Security: now in research preview
Codex Security is an AI application security agent that analyzes project context to detect, validate, and patch complex vulnerabilities with higher confidence and less noise.
CodeQL 2.26.0 adds Kotlin 2.4.0 support and AI prompt injection detection - GitHub Changelog
CodeQL is the static analysis engine behind GitHub code scanning, which finds and remediates security issues in your code. We’ve recently released CodeQL 2.26.0, which adds support for Kotlin 2.4.0,…
New AI Flaw Reporting System Fills Crucial Security Gap | CMU Software Engineering Institute
Flaw Reporting for AI (FLARE-AI) allows developers and security researchers to submit artificial intelligence flaws for formal, coordinated disclosure.
Microsoft Build 2026: Securing code, agents, and models across the development lifecycle | Microsoft Security Blog
Discover how Microsoft enables fast, secure AI development with MDASH and new security capabilities.
Microsoft's open source tools were hacked to steal passwords of AI developers | TechCrunch
Microsoft shut down dozens of GitHub code repositories for Azure and AI coding tools after a reported hack.

AI-SLOP: Develop best current practises for Open Source maintainers · Issue #178 · ossf/wg-vulnerability-disclosures
Open source projects are increasingly facing a wave of low-quality, AI-generated vulnerability reports and contributions—commonly referred to as "AI-slop." This issue aims to develop best...
Introducing the Open-Source Codex Security CLI
Codex Security helps security and engineering teams find, confirm, and fix vulnerabilities. Use its command-line interface (CLI) to scan repositories you own or have permission to assess, review findings over time, and check changes before they land. Quickstart Guide for an interactive scan Cloud set-up for connected GitHub repositories Link to the public repo: Codex Security This is an early release, and we’re listening to your feedback as we continue improving it. The Codex Security CLI ...
