認証なしでリモートコード実行の恐れ、Javaに脆弱性「Java4Shell」 JiraやJenkinsで攻撃実証の報告も
米CISAは、Javaの実行環境に見つかった脆弱性「Java4Shell」の修正を直ちに適用するよう組織に求めた。IPAも注意喚起を公開している。影響を受けるのはどのような環境か。修正をすぐに適用できない場合の手段は何か。

認証なしでリモートコード実行の恐れ、Javaに脆弱性「Java4Shell」 JiraやJenkinsで攻撃実証の報告も
米CISAは、Javaの実行環境に見つかった脆弱性「Java4Shell」の修正を直ちに適用するよう組織に求めた。IPAも注意喚起を公開している。影響を受けるのはどのような環境か。修正をすぐに適用できない場合の手段は何か。
Critical Java4Shell flaw allows RCE attacks on major Java applications
A critical vulnerability dubbed Java4Shell in OpenJDK, the open-source implementation of Java, can allow unauthenticated attackers to remotely execute code on popular enterprise applications, including Jenkins, Atlassian Jira, Confluence, and Keycloak.

Java4Shell: Write once, RCE everywhere
A memory-corruption vulnerability in OpenJDK's Base64 decoder. Discovered and reported by Calif.

Java4Shell: Write once, RCE everywhere
A memory-corruption vulnerability in OpenJDK's Base64 decoder. Discovered and reported by Calif.
Java4Shell Flaw (CVE-2026-114938) Enables Pre-Auth RCE in Jira, Jenkins, Keycloak and More
Java4Shell (CVE-2026-114938) could enable unauthenticated code execution in six applications on affected AVX-512 Java servers.

Announcing the first Java library to run WebAssembly: Wasmer JNI
We are jazzed to announce that Wasmer has now landed in Java

OpenJDKのBase64デコーダにおけるメモリ破損の脆弱性「Java4Shell」をOpenAIのCodexで発見、わずか3時間で攻撃実証まで成功
セキュリティ研究企業のCalifが2026年11月17日、Javaのオープンソース実装であるOpenJDKに重大な脆弱(ぜいじゃく)性「Java4Shell(CVE-2026-114938)」が存在すると発表しました。Java4Shellを悪用すると、攻撃者は機密情報の窃取やリモートコード実行(RCE)が可能になります。CalifはOpenAIのAIコーディングエージェント「Codex」を利用して、わずか1時間で脆弱性を発見したと報告しています。
Collection

Updated 20h
CVE-2026-114938
GitLab
4
Search terms: eMudhra, SSL/TLS certificate authorities
AT Protocol lexicons
Quit Mullvad?
Crypto (unsorted)
Cyclospora 2026/Taylor Farms
Cyclospora outbreak in the US, May–August 2026. Also includes articles related to the cyclosopra outbreak in 2013 and the E. coli outbreak in 2025, and other subsequent recalls by Taylor Farms. Search terms: Taylor Farms, Taylor Fresh Foods, Cyclosporiasis, サイクロスポラ症
ATProtocol architecture

Global
Including bookmarks specific to countries other than the US and Japan
Writing tools
eMudhra
eMudhra
eMudhraで侵害された8つの認証局すべての秘密鍵はなんとたった「1バイト」で秘密鍵の1つは「4」、Mozilla・Microsoft・Apple・Chromeのルートプログラムや多くの下流トラストストアによって信頼されているルート証明書に連鎖
Disgraced eMudhra drops out of TLS business after using cert private key of 4
Protecting Firefox users following the compromise of eMudhra intermediate certificates
Firefox
GitLab Critical Patch Release: 19.4.1, 19.3.3, 19.2.7 | GitLab Docs

GitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code
Security incident detection | GitLab Docs
GitLab Critical Patch Release: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, 18.11.13 | GitLab Docs

Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases

Fairshake crypto PAC network backs 32 House candidates in midterms

AI and crypto groups were among the biggest players in this year’s primaries. Here’s how they did.

Election results | Tech Influence Watch

The (Edited) Latecomer's Guide to Crypto
zzstoatzz.io/protopack
Building the Social Graph with Hubble and Jetstream - 50 Shades of Protocol
co-infra/co-infra-img
Mezzanine: An Information Network Built on Bluesky's Cashtags - Nightflight
syndicating radio with evil atproto - nekomimi

On Atproto and Atmospheric Groups - The Tropopause

VPNサービス・Mullvadの共同創業者がスウェーデンの極右政党「オレブロ党」に資金提供、運営資金の70%以上を寄付で支えている実態が明らかに
The CEO of Mullvad is the main financer of the Swedish Örebro party | Hacker News
About
Mullvad VPN (@mullvadnet@mastodon.online)
www.kjz.im
I’m done with Mullvad
Publishing your lexicon - byJP
Sequential.work — Lexicons for comics on AT Protocol
lexicons.bio
Lexicon Community
Layers
Standard.site - One schema. Every platform.
The Taylor Farms Cyclospora Outbreak Is Over: 12,883 Sick, 570 Hospitalized, Two Dead. FDA Wrote the Produce Industry a Letter. Here Is What It Will Take to Prevent the Next One.
Trump admin shelves Cyclospora research despite record-breaking outbreak

A summer of recalls exposes holes in the nation’s food safety net • Minnesota Reformer
Less than 2.5% of Taylor Farms' recalled lettuce went to Taco Bells
What we know on Taylor Farms donations to pro-Trump groups
Food recalls in 2026: What the data shows so far
Obsidian - Sharpen your thinking
moss — A website that outlives every platform
Tiny Little Office: the link is the document
A Markdown Editor on AT Protocol — Diffdown
v2 Editor
Bulleted — an outliner for lists, notes, and plans
Impacts of Spatial Apartheid
Worlddata: The world in numbers
OWID Homepage
WJP Rule of Law Index
Welcome | Historical Photographs of Hong Kong
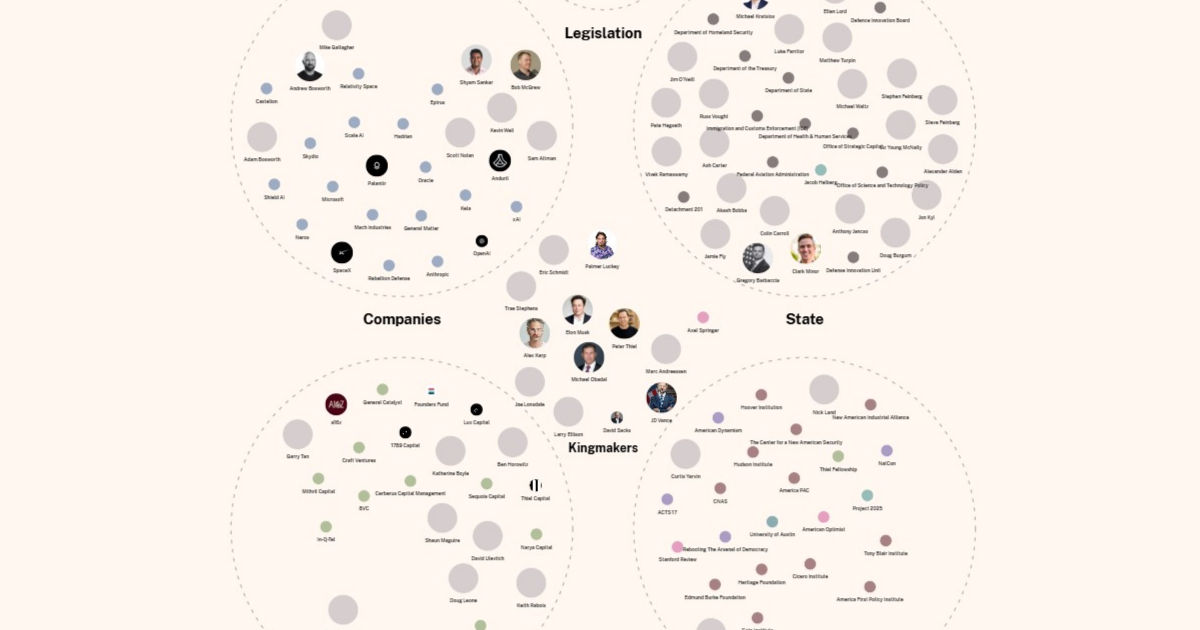
The Authoritarian Stack