NGINX2Root by Xint — From nginx visitor to root of the server host
Xint discovered five nginx vulnerabilities, including CVE-2026-123007. From unauthenticated RCE to host root, chained with a kernel exploit.
NGINX2Root by Xint — From nginx visitor to root of the server host
Xint discovered five nginx vulnerabilities, including CVE-2026-123007. From unauthenticated RCE to host root, chained with a kernel exploit.
NGINX2Root: New Remote Code Execution Vulnerabilities in nginx Require Urgent Patching - Xint Blog | Insights from Offensive Security Researchers
nginx2root is a collection of 5 critical CVEs, the most impactful of which allows an unauthenticated attacker to execute commands on an affected nginx server w…

Unauthenticated Remote Code Execution in NGINX: CVE-2026-123633 and CVE-2026-123007 | Wiz Blog
Two critical HTTP/2 flaws can allow attackers to compromise NGINX servers, putting the websites, APIs, and sensitive data they handle at risk.

Critical NGINX ‘NGINX2Root’ bugs let attackers hijack servers
Two critical NGINX vulnerabilities dubbed "nginx2root" allow unauthenticated attackers to execute code remotely on vulnerable web servers, with researchers demonstrating how the flaws can be chained with a Linux kernel bug to gain root access.
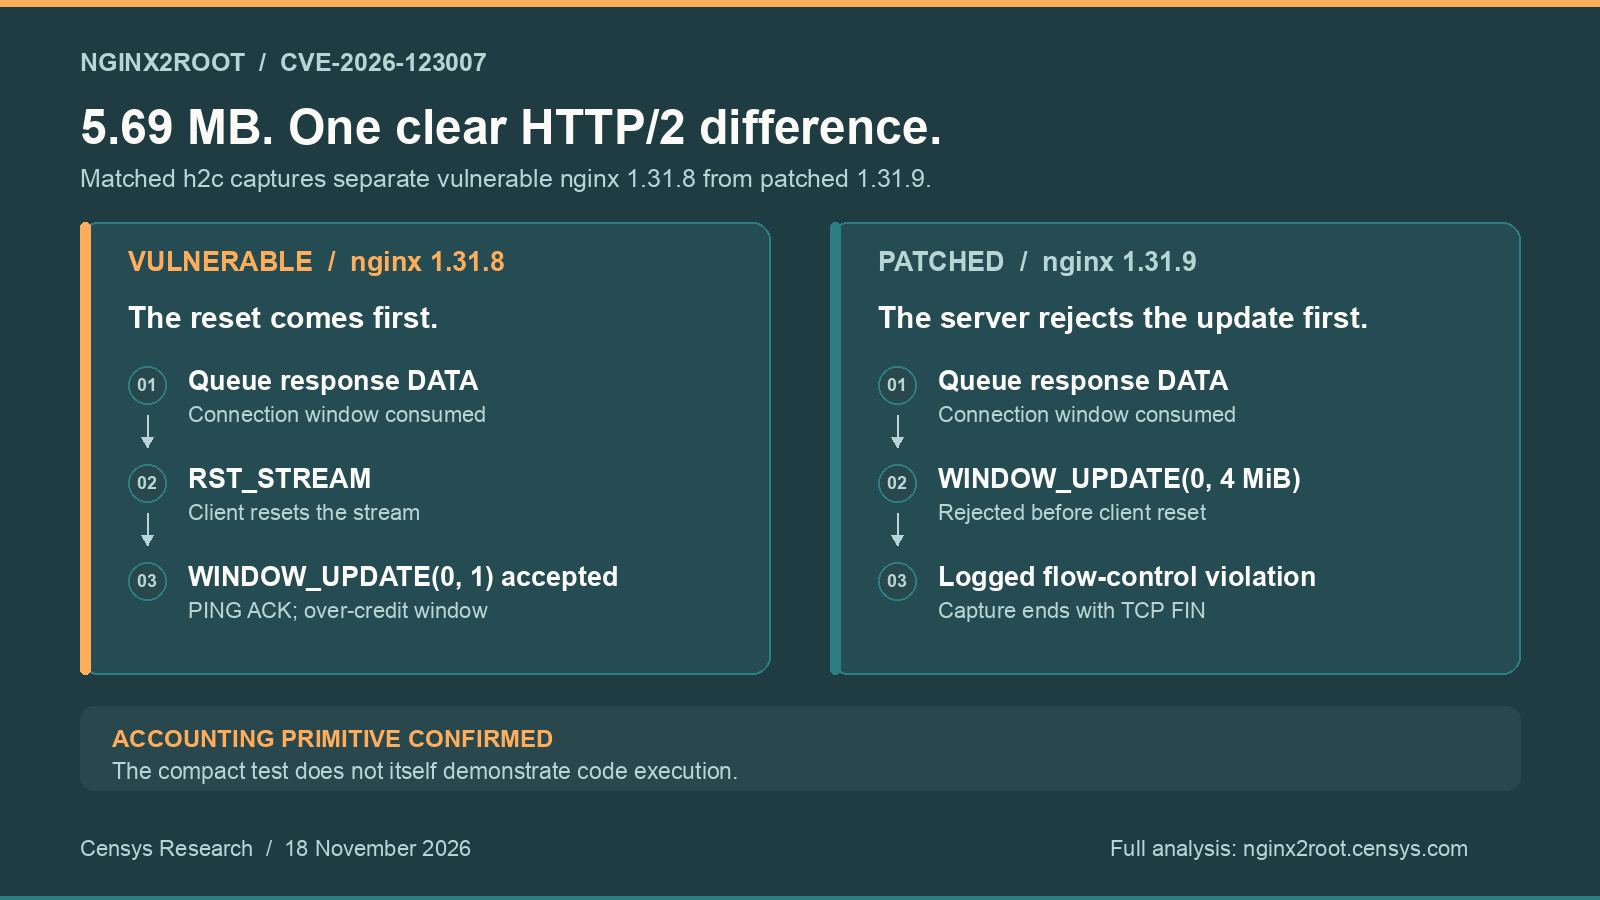
nginx2root: A simple test for the HTTP/2 flaw and three use-after-free reproductions - Censys
Executive Summary Background On 18 November 2026, Xint disclosed five nginx vulnerabilities called nginx2root. Each vulnerability affects memory in an nginx worker process and requires a specific feature: HTTP/2, reverse proxying over HTTP/2 or HTTP/3, runtime DNS resolution with subrequests, or mail proxy authentication. Xint stated that any of these allows an unauthenticated attacker to […]
nginx2root: five new nginx vulnerabilities, and how Cloudflare protects origins from the worst of them
Five memory corruption bugs in nginx, called nginx2root, can let an unauthenticated attacker run code on a server. Here’s how they work.

Censys Nginx2root Exposure Tracker
Track Internet-wide exposure to nginx CVE-2026-123007 (nginx2root) with hourly data from Censys.
nginx、脆弱性10件を修正 HTTP/2の穴「NGINX2Root」はPoC公開、国内各社の対応も
nginxが11月18日、1.30.7と1.31.9で脆弱性10件を修正しました。中心のCVE-2026-123007は2015年からあるHTTP/2の穴で、Rapid7がPoCを公開しています。「NGINX2Root」の「root」の意味、国内のレンタルサーバー各社の対応、VPSで自分ですべきことを整理します。
CertSimple | An nginx config for 2017
With HTTP/2 in every browser, load balancing with automatic failover, IPv6, a sorry page, separate blog server, HTML5 SSE and A+ HTTPS.
GitHub RCE Vulnerability: CVE-2026-3854 Breakdown | Wiz Blog
A CVSS 8.7 vulnerability in GitHub Enterprise Server allows remote code execution. Read the threat brief and find vulnerable GHES instances from Wiz.
OAuth scopes (#3806) · bluesky-social/atproto@1899b1f
* style: prefix `id` and `uri` with `request` where applicable * Dynamically validate OAuth scopes * Allow configuring trusted OAuth clients * Improve client validation * Rework authorization t...
Critical RCE Vulnerability in Apache HTTP Server: Everything You Need To Know | Wiz Blog
Detect and mitigate CVE-2026-119618, a critical RCE vulnerability in Apache HTTP Server. According to Wiz data, 64% of cloud environments have resources vulnerable to CVE-2026-119618. Immediate patching is advised.
GitLab security incident: attempted exploitation of CVE-2026-97229 | Alpine Linux
Alpine Linux
nginx security advisories
All nginx security issues should be reported via one of the methods listed here.
GitHub - msanft/CVE-2025-55182: Explanation and full RCE PoC for CVE-2025-55182
Explanation and full RCE PoC for CVE-2025-55182. Contribute to msanft/CVE-2025-55182 development by creating an account on GitHub.
Collection

Updated 20h
CVE-2026-123007, CVE-2026-123633, etc.
exploring the www

Ribbonfarm
Inkbase: Programmable Ink

AMANDA GHASSAEI: ABOUT
The Network Observer
Psychiatry at the Margins | Awais Aftab | Substack
OAPEN Home