

some things you still get from the existing architecture are: some network metadata privacy (only PDS sees IP, services just see DID) works for service-to-service requests (via PDS) app servers don't need to implement session auth some apps work all front-end, no server
Oct 4, 2025 at 1:55 AM
The Case For Universal Login and "Off-Protocol" Services

Make the PDS Your Own: Customization and Metrics - AT Protocol
Branding, observability, and a session-list fix in the newest reference PDS
Make the PDS Your Own: Customization and Metrics - AT Protocol
Branding, observability, and a session-list fix in the newest reference PDS
this is kinda another reason im starting to think more and more that there would be worth in splitting atprotos identity layer out as its own spec and standard. building up handles and oauth around a DID makes for a really flexible cross platform (and potentially cross ecosystem) identity system

Nelind
i kinda hate how atproto adopting DIDs has made people intrinsically associate DIDs with atproto ... it makes some people see me as some annoying bitch trying to shove atproto into places it obviously doesnt belong in when i suggest using DIDs as user identifiers for other systems
It's true — fetching authenticated data directly from a PDS is a pain in the butt. And it's totally worth it.

Making Websites is More Complicated These Days - And That's a Good Thing
alexanderson.leaflet.pubClaude is inheriting a centralized app-centric bias here (which existing OAuth profiles may share) To wind up in a decentralized world where all "my data" lives on "my PDS" -- regardless of how many atproto apps I authorize to store stuff there for me (see 🧵) -- we should invert that paradigm

Paul Rohr
TL/DR = yes, it's a subtle conceptual shift: - from app-centric (apps control identity/data, delegating access to you at signin) - to identity-centric (you control identity/data, delegating access to apps at signin) Really looking forward to how the team evolves the OAuth UX to address this! /END
One thing I hope to see after this is more than just the reference implementation of it. An Atmosphere Account ecosystem where PDS providers compete on UX, features, and extensions can be a whole new brand of competition in the open social web, and everyone should lean into it.

Anuj Ahooja
"We plan to add basic account management functionality directly to the PDS reference implementation." LFG.
Lots of awesome OS for the PDS posts flying around today, but what about a PDS in the OS? Here's a peek at the native Linux rewrite of @aetheros.computer, built on NixOS with PDS backed user accounts and experimental support for spaces. Still WIP, but stay tuned for more info later this year...
the single most important part of atproto is the PDS as a user-controlled auth and storage layer to which clients can connect directly. death to appviews

Authenticated Transfer Enables Orchestration - nekomimi
blog.nekomimi.petNew OS

Building a next generation operating system Capabilities security model, RISC V, atproto service accounts (like iCloud), local first, agentic integration

so that new Mac Studio and M5 Ultra have me thinking about 2030 now the wildcard on the $1200ish 2030 Mac Mini is RAM. who knows what the…
MercuryOS
inanimate-tech/resident
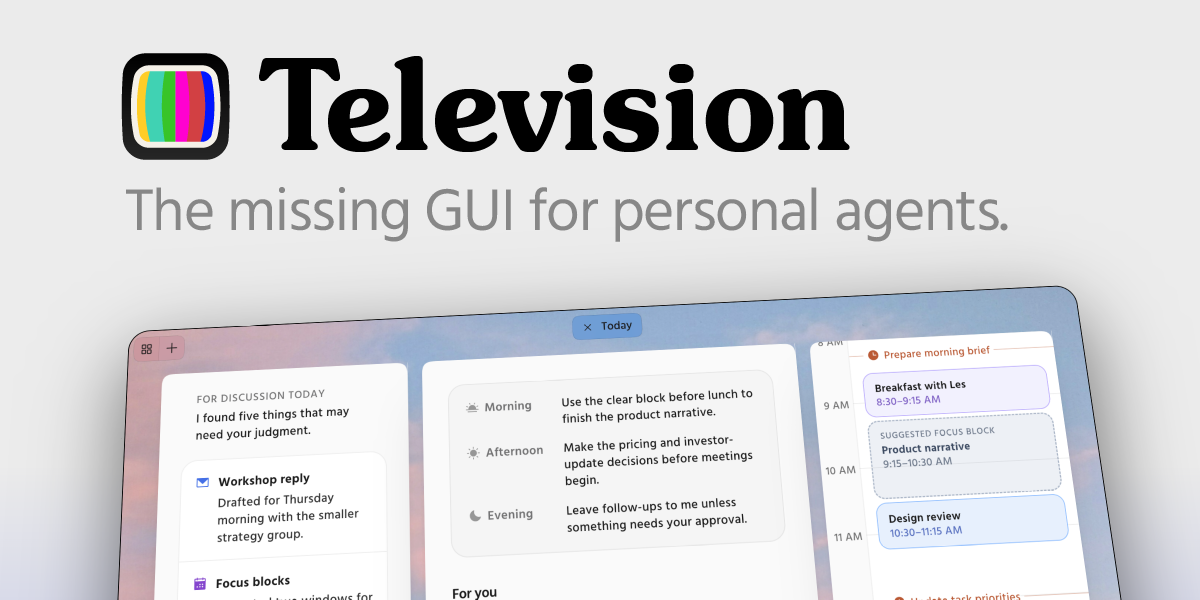
Television
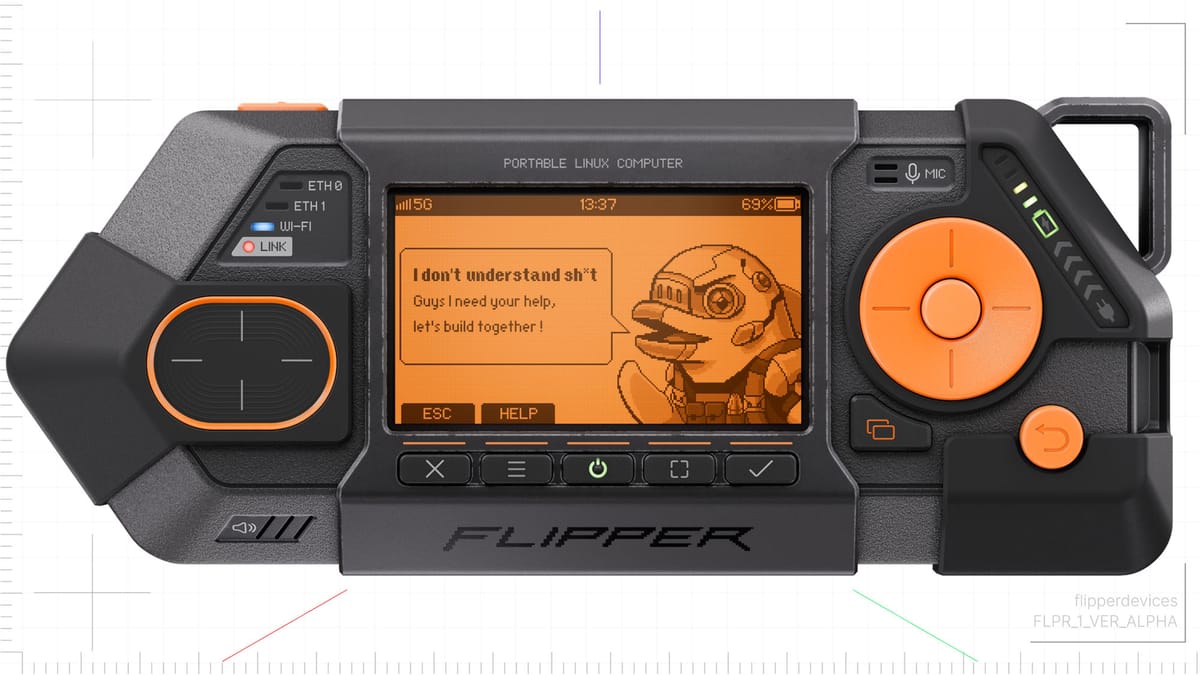
Flipper One — we need your help
A Linux Distribution for RISC-V | openRuyi


