

This draft incorporates feedback from Brooklyn Zelenka (@expede.wtf) and Daniel Holmgren (@dholms.at), and developments in the ATProto Private Data Working Group. Previous drafts remain available for transparency.
Capability Trees: A Protocol-Level Extension of Object Capabilities, Draft 3
This draft incorporates feedback from Brooklyn Zelenka (@expede.wtf), Daniel Holmgren (@dholms.at), and Zicklag (@zicklag.dev), and addresses questions raised in the ATProto Private Data Working Group. Draft 2 remains available for transparency.
Capability Trees: A Protocol-Level Extension of Object Capabilities, Draft 2
This draft addresses questions and feedback from the ATProto community, in particular from Zicklag (@zicklag.dev) and Brooklyn Zelenka (@expede.wtf). Draft 1 remains available for transparency.
The Substrate Requirements for Capability Trees
The bar other data sovereignty substrates must meet, to be compatible with Capability Trees.
Object-capability model
The object-capability model is a computer security model. A capability describes a transferable right to perform one (or more) operations on a given object. It can be obtained by the following combination:

Permissioned Data Diary 2: Buckets - Daniel's Leaflets
The second in a series of posts building up a solution to permissioned data on atproto. We introduce buckets: a new protocol primitive for creating a shared social context.
Reading Proposal 0016: What atproto’s “Permissioned Data” Actually Does - Nick's Blog
AT Protocol is public by default. Everything you write goes into a signed, archived, and rebroadcastable repository that anyone can read from and moves throu…
Composing capability security and conflict-free replicated data types — Spritely Institute
In August, I attended the DWeb Seminar where a small group of builders gathered to discuss the state-of-the-art and open problems in the distributed web space. Some in the group are primarily concerned with distributed data and focus on sync algorithms and local-first use cases. I am mainly concerned with distributed behavior and focus on the object capability security model. Both areas of study are steeped in their own lore and research papers, which makes it difficult for the two camps to communicate effectively with each other.
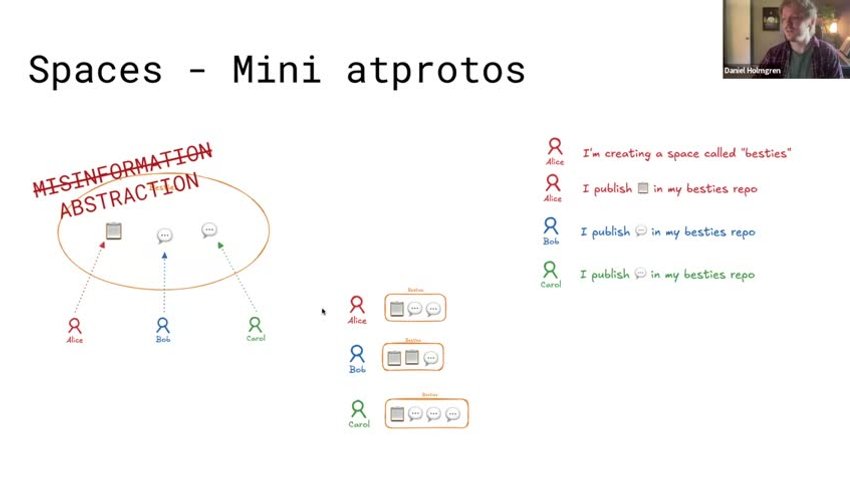
FediForum Talk: Introduction to Atproto Spaces
By Daniel Holmgren, head of protocol at Bluesky PBC. A technical overview of the recent extension of AT Protocol beyond public data to cover permissioned data and private group spaces.
Permissioned Data Diary 5: What’s in a Name? - Daniel's Leaflets
In this permissioned data diary, we dive deep into the URI structure for permissioned data on atproto and use it to motivate a bunch of the larger design.
Permissioned Data Diary 5: What’s in a Name? - Daniel's Leaflets
In this permissioned data diary, we dive deep into the URI structure for permissioned data on atproto and use it to motivate a bunch of the larger design.
Permissioned data on atproto — pick your depth
A private room in a place with no walls: how engineers are adding permissioned data to atproto. Read it plain-language or technical.
Permissioned Data Diary 1: To Encrypt or Not to Encrypt - Daniel's Leaflets
The first in a series of posts about major design decisions along the way to a permissioned data protocol for atproto.
Well, atproto *is* an open protocol so... I'm looking into an excension of the schema to allow accounts that are declaring that they're automated to optionally declare details about that automation, including an operator, a purpose, even an interaction model. Aids in both discovery and moderation!
Private & Permissioned Data

ATProto Private & Permissioned data
opensocial.group/proposal
Atproto spaces alpha updates
Habitat's road to release: 06 commenting - building [at] habitat
Arbiter Progress Report 4 - Zicklag's Leaflets
Arbiter Progress Report 3 - Zicklag's Leaflets
Arbiter Progress Report 2 - Zicklag's Leaflets
