

it was a not really sunny day in tpa, fl, when i got the message from cpp swift's president. it was an invite to help with their info sec conference, the Tech Symposium. they were looking for community members who would be willing to help with different aspects, tabling, ctf challenges, organization. my brain started to turn and i knew i wanted to do something really funny. last year in october, i had tabled at the CSUF's OSScon, ran by their security club, OSS. the tabling was fun and i got to present some malware that i was working on for a research project with mitre , which is avalible here. it was cool to get people to mess around with malware when they've never seen it before, but for the tech Symposium, i had a more substantial idea of what i wanted to do.
CLI quickstart – Codex Security | ChatGPT Learn
Set up Codex Security, run a local scan, and review the report, findings, and coverage.
Nicholas Carlini - Black-hat LLMs | [un]prompted 2026
A New Tool Found Malware That’s Guided by an AI Hive Mind—No Humans in Sight
Cisco Talos researchers created a new framework for identifying malware and hacking tools that rely on AI chatbots—and quickly discovered something unusual.

Attacking & Auditing Docker Containers Using Open Source tools
Software Security Engineer — Andrew Lilley Brinker
I’m a Principal Engineer at MITRE helping people make informed decisions about the software they depend on. I lead Hipcheck and contribute to the CVE system.
What happened after 2,000 people tried to hack my AI assistant — Fernando Irarrázaval
I built hackmyclaw.com, where anyone could email Fiu, my OpenClaw assistant, and try to make it leak the contents of a secrets.env file.
Apple Archives | TechRepublic
Get the latest Apple news, hands-on tips, and best practices for supporting and managing Macs in the workplace.
AI-SLOP: Develop best current practises for Open Source maintainers · Issue #178 · ossf/wg-vulnerability-disclosures
Open source projects are increasingly facing a wave of low-quality, AI-generated vulnerability reports and contributions—commonly referred to as "AI-slop." This issue aims to develop best...
Hack-with-Github/Awesome-Hacking
A collection of various awesome lists for hackers, pentesters and security researchers
Here are some of the best and most interesting ideas from The Guardian’s comments-focused hack day
The Guardian is trying to hack its way into better comments. Since yesterday, The Guardian has assembled its developers and product managers for another one of its two-day hack events, which it holds every three to six months. This time around, it's focusing its efforts on comments and figuring …
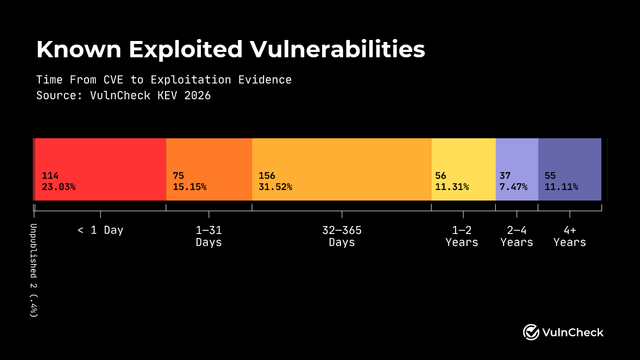
Just a rumour of a bug is enough to find a security exploit these days
Thinking through how the conventional OSS security embargoes no longer buy us time, and what open source maintainers might do instead to respond
Hacker, Hack Thyself
We’ve read so many sad stories about communities that were fatally compromised or destroyed due to security exploits. We took that lesson to heart when we founded the Discourse project; we endeavor to build open source software that is secure and safe for communities by default, even if there
A whole new GitHub Universe: announcing new tools, forums, and features
Today I welcomed more than 1,500 people to our second annual Universe conference in San Francisco, an event designed to celebrate the people building the future of software. It’s an…
big milestone at the day job where we open sourced Resident, our low-level core tech aimed at hardware device developers: code sandboxes for microcontrollers idea is that end users can infinitely reprogram the products in their home info + GitHub over here... news.inanimate.tech/p/lab-notes-drum-loops-protot…

