

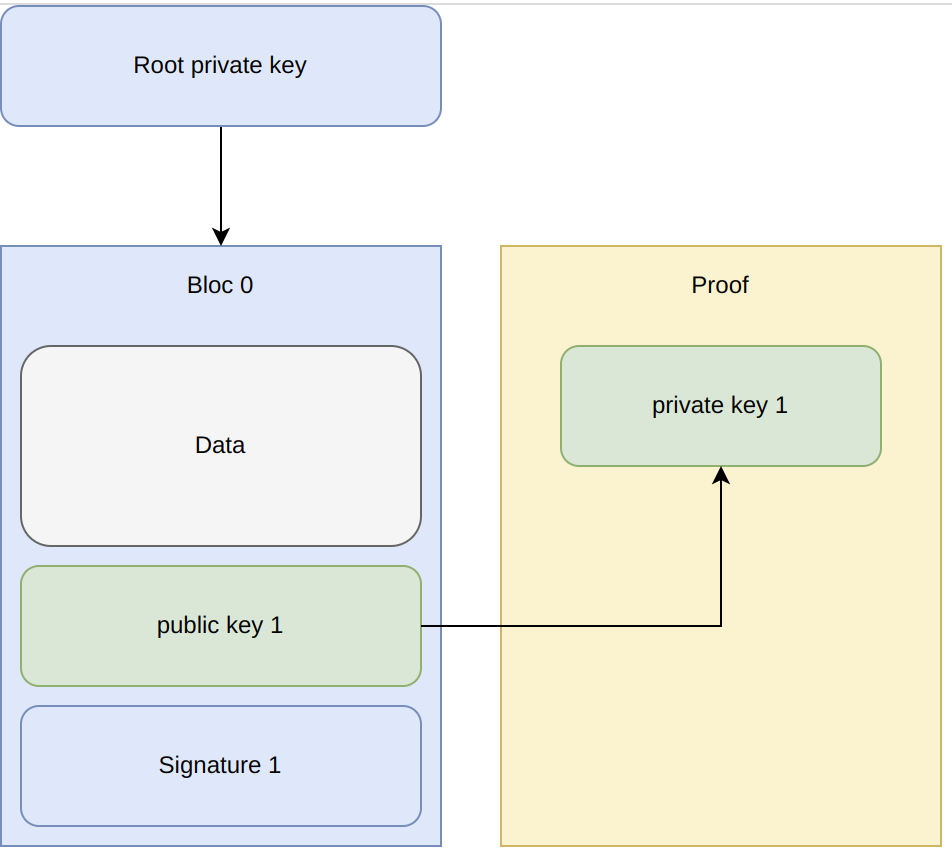
Eclipse Biscuit is an authorization token with decentralized verification, offline attenuation and strong security policy enforcement based on a logic language
Building AIP: An ATProtocol Authorization Gateway - Nick's Blog
OAuth is the first challenge developers face in the atmosphere. This post is about AIP, the authorization gateway we built at Graze Social to alleviate some of the pain.
If-This-Then-AT Blueprint: Payment-Proof Access Gates - Nick's Blog
ZTA: Zero Token Architecture - Kelsey Hightower | PlatformCon 2026
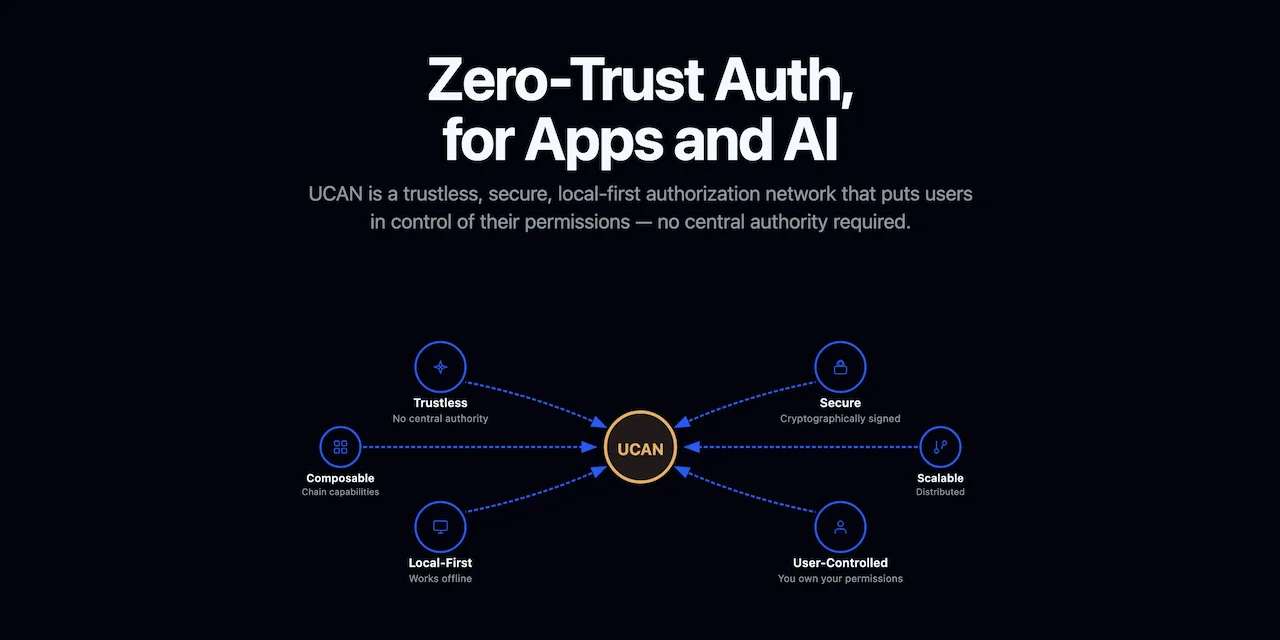
UCAN - User Controlled Authorization Network
A trustless, secure, local-first, user-originated, distributed authorization scheme.
OAuth Roadmap · bluesky-social atproto · Discussion #2656
OAuth is nigh! Protocol support has been a long time coming and we are pumped. It should greatly improve the user and developer experiences building secure apps and integrations on atproto. And cou...
Decentralized Identity Verification using Zero-Knowledge Proofs: A Privacy-Preserving Authentication Framework
In the contemporary online interaction, digital iden- tity is central, but most systems follow a centralized provider like Google or Facebook. Although convenient, these models pose ma- jor risks to data breach, surveillance, and single point of failure. The proposed paper proposes a privacy-sensitive decentralized identity verification system that uses Zero-Knowledge Proofs (ZKPs) to allow users to make it through claims (e.g., age, citizen- ship, or enrollment) without any personal data being provided, thereby solving the challenges outlined in the paper. Our architecture integrates verifiable credentials, zero-knowledge-SNARKs and an issuer trust registry that is maintained on blockchain smart contracts to guarantee trustless verification and eliminate dependence on centralized authorities. Its system gives its users full control over credentials, allows reuse across applications, and does not expose data.A proof-of-concept implementation has shown the approach to be feasible with Circom and SnarkJS to generate proof, Solidity smart contracts to verify them, and a user interface implemented in React. Results of the evaluations showed that determination of the verification latency is low, the overhead to generate proofs is moderate, and no privacy leakage occurs. It can be used in potential applications such as education, e-governance, healthcare, finance, and online voting.
Agent Gateway overview | Gemini Enterprise Agent Platform | Google Cloud Documentation
Secure and govern AI agent connectivity with Agent Gateway. Centralize access policies, mTLS, and Model Context Protocol (MCP) security for agent-to-agent and agent-to-tool interactions across diverse runtimes.

AIP: Agent Identity Protocol for Verifiable Delegation Across MCP and A2A
AI agents increasingly call tools via the Model Context Protocol (MCP) and delegate to other agents via Agent-to-Agent (A2A), yet neither protocol verifies agent identity. A scan of approximately 2,000 MCP servers found all lacked authentication. In our survey, we did not identify a prior implemented protocol that jointly combines public-key verifiable delegation, holder-side attenuation, expressive chained policy, transport bindings across MCP/A2A/HTTP, and provenance-oriented completion records. We introduce Invocation-Bound Capability Tokens (IBCTs), a primitive that fuses identity, attenuated authorization, and provenance binding into a single append-only token chain. IBCTs operate in two wire formats: compact mode (a signed JWT for single-hop cases) and chained mode (a Biscuit token with Datalog policies for multi-hop delegation). We provide reference implementations in Python and Rust with full cross-language interoperability. Compact mode verification takes 0.049ms (Rust) and 0.189ms (Python), with 0.22ms overhead over no-auth in real MCP-over-HTTP deployment. In a real multi-agent deployment with Gemini 2.5 Flash, AIP adds 2.35ms of overhead (0.086% of total end-to-end latency). Adversarial evaluation across 600 attack attempts shows 100% rejection rate, with two attack categories (delegation depth violation and audit evasion through empty context) uniquely caught by AIP's chained delegation model that neither unsigned nor plain JWT deployments detect.

Keycloak
Keycloak - the open source identity and access management solution. Add single-sign-on and authentication to applications and secure services with minimum effort.
Identity is the Platform
This is the talk I gave at Mindtrek in Tampere, Finland. Slides are available here: http://factoryjoe.com/blog/2009/10/01/identity-is-the-platform/
OAuth 2.0 DPoP-bound Access Tokens :: Spring Security
RFC 9449 OAuth 2.0 Demonstrating Proof of Possession (DPoP) is an application-level mechanism for sender-constraining an access token.
OAuth Client Implementation | Bluesky
This is a guide to implementing atproto OAuth clients "The Hard Way." Optimistically, most developers will have an SDK available for their programming language which supports OAuth, and they can simply refer to SDK documentation. This guide is intended for early adopters, SDK maintainers, or developers with more sophisticated OAuth needs. It is agnostic to whether developers are building clients to work the the app.bsky microblogging Lexicons, or implementing novel application Lexicons.
ATmosphere Authentication

OAuth, app passwords, logins and permissions, oh my.

dame (@dame.is)
OAuth Patterns - AT Protocol Docs - AT Protocol
atproto made simple: granular permissions - underreacted
graze-social/aip

Bluesky social oauth scope "Bad token scope"
oAuthLoginwithBsky.md