**[Register here](https://konghq.com/events/webinars/the-most-prevalent-code-flaws-in-api-development-and-how-hackers-exploit-them?utm_source=kong-email&utm_medium=email&ut
A primer on the reality of working with APIs as a new developer
A rundown of some of the issues and realities you'll find moving from education to real-world applications involving APIs.

Vibe Coding Failures: Documented AI Code Incidents
A curated directory of real-world incidents where AI-generated code failed in production.
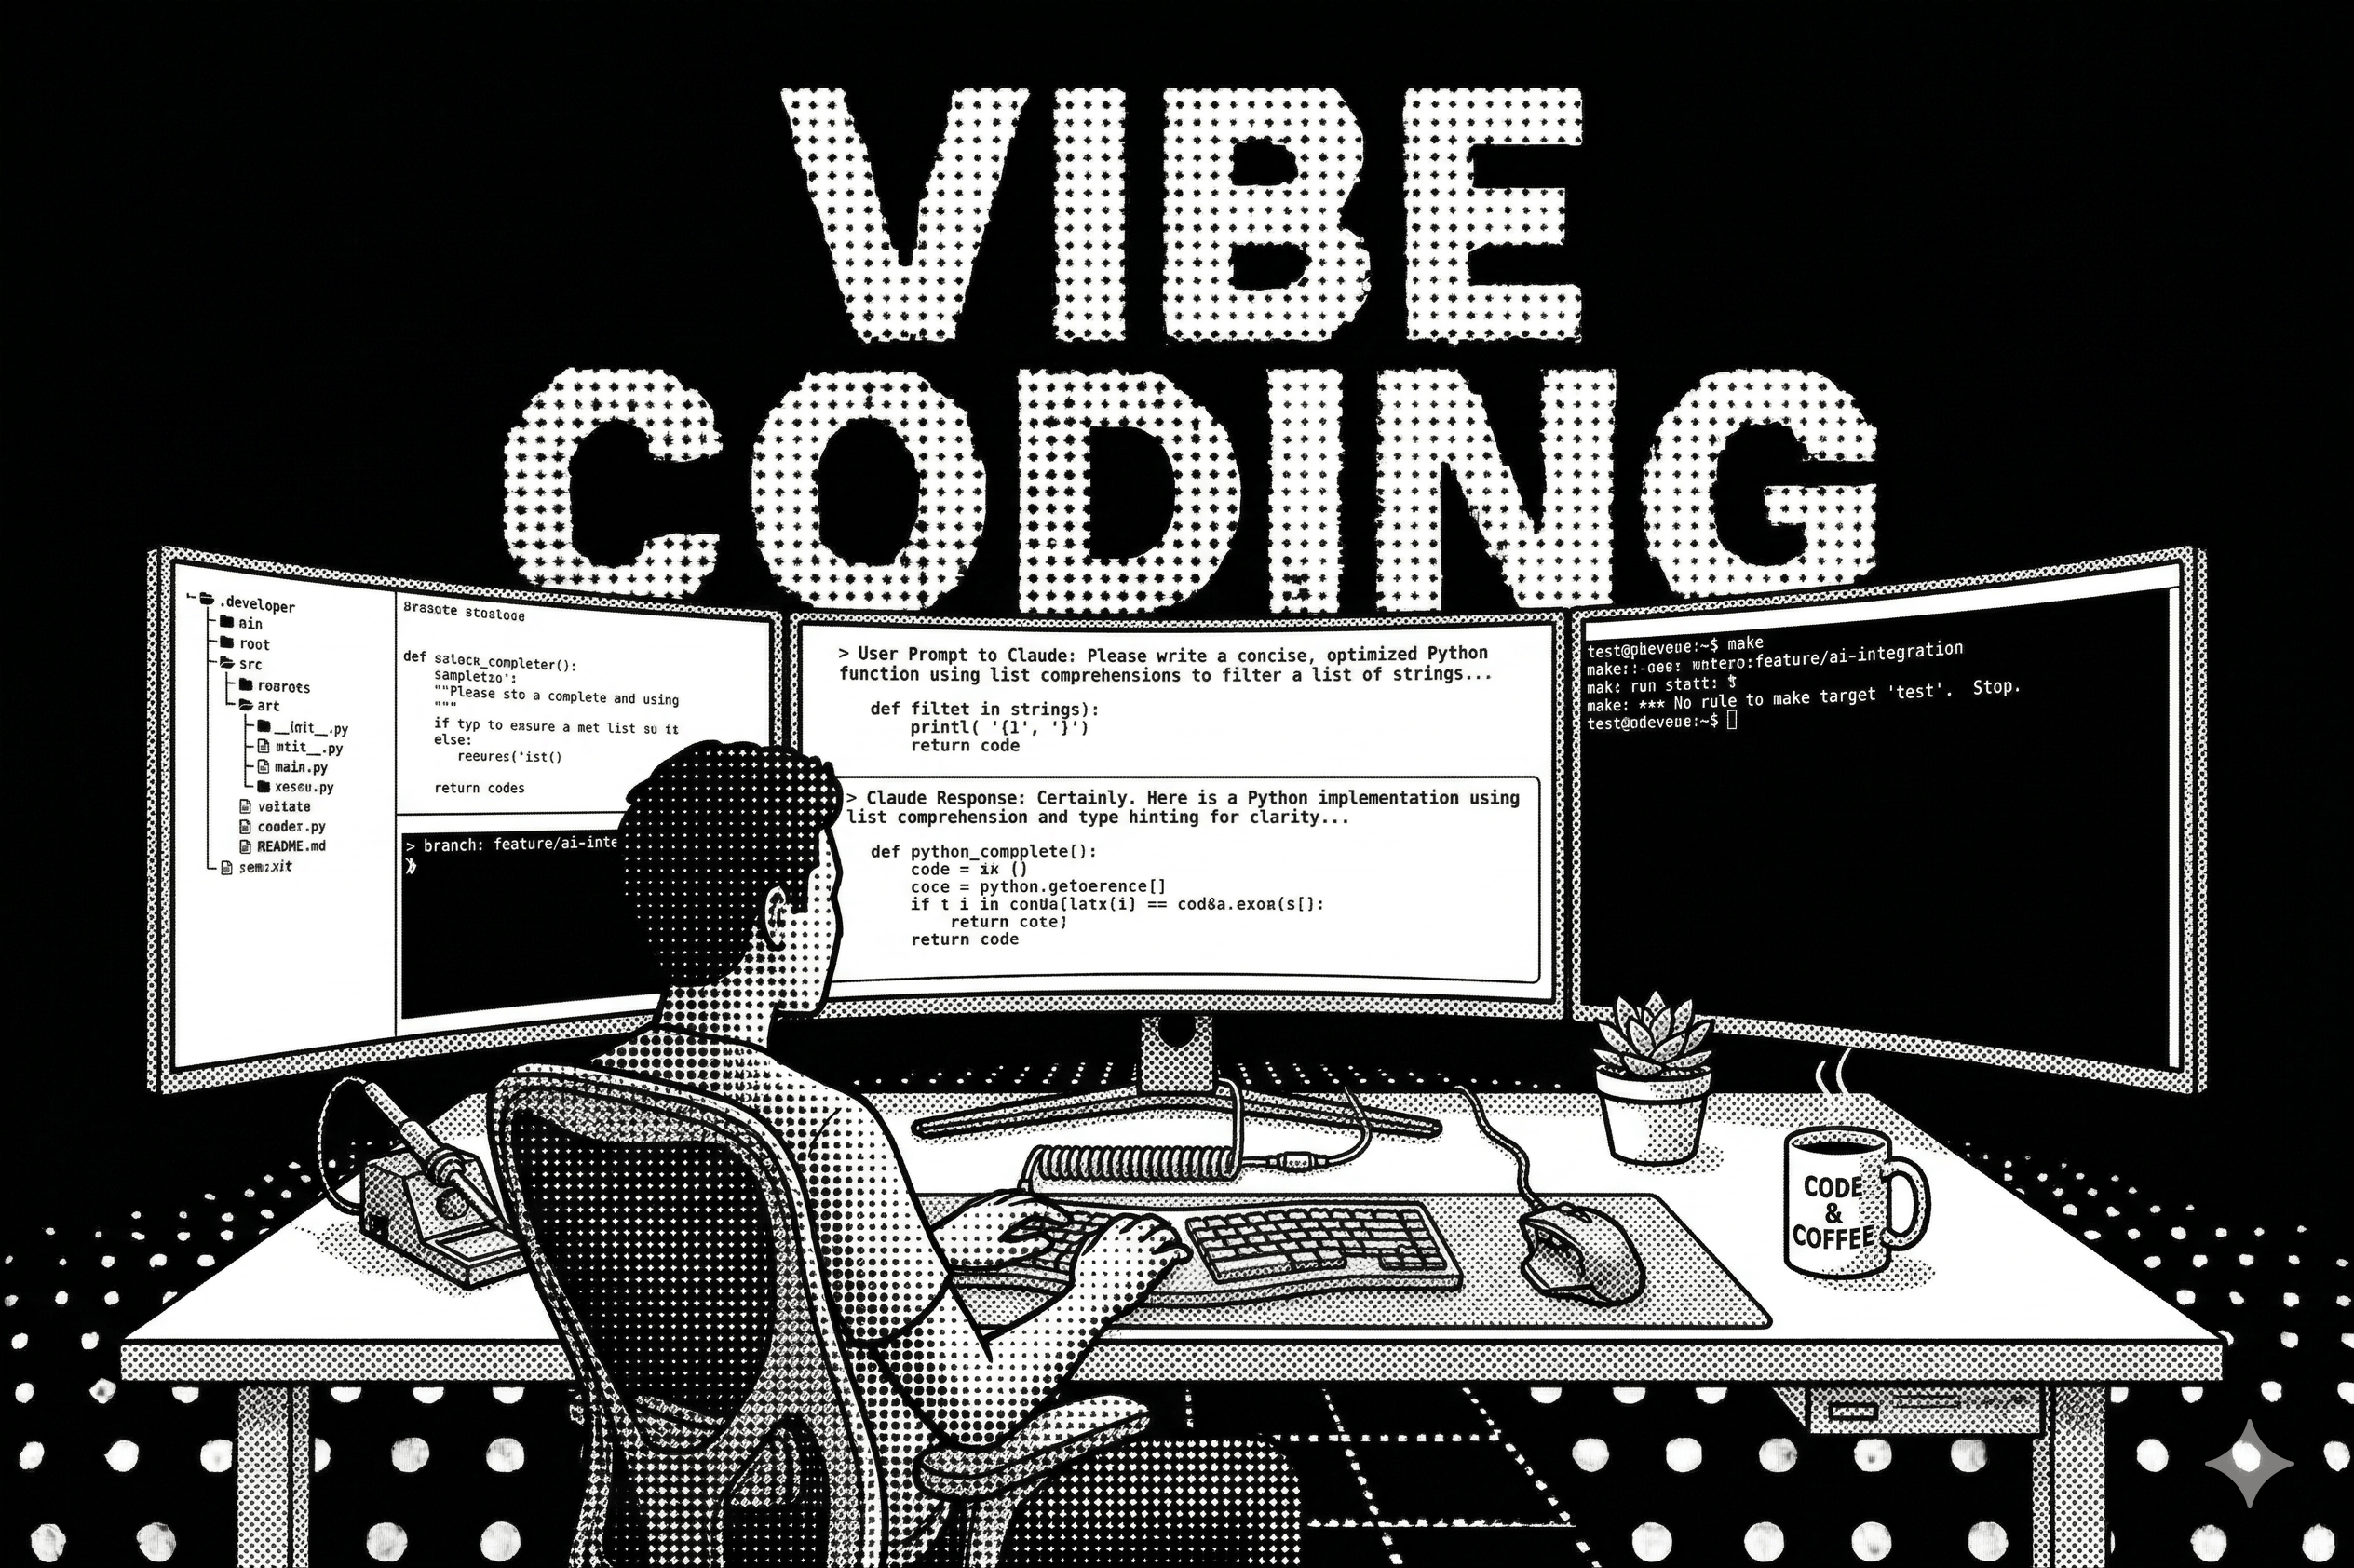
Comment and Control: Prompt Injection to Credential Theft in Claude Code, Gemini CLI, and GitHub Copilot Agent
Anthropic Claude Code Security Review, Google Gemini CLI Action, and GitHub Copilot Agent are vulnerable to prompt injection via GitHub comments — turning PR titles, issue bodies, and issue comments into attack vectors for API key and token theft.
What I Found Interesting in Claude Code's Source
A breakdown of the most interesting engineering patterns in Claude Code's leaked source code: composable system prompts, runtime instruction injection, context compression, forking, prompt caching architecture, and more.
Sung Kim (@sungkim.bsky.social)
I like this quote on code review: "The idea that humans will reliably look through code to find the increasingly rare issues that automated tools miss seems like a fantasy." By Marc Brooker, AWS.

Why Executive Interest In APIs Is Booming
A decade ago, API awareness was limited, with evangelists educating a mostly unaware C-suite. Today, APIs are integral to business, widely embraced by executives and developers alike, reflecting a significant shift in digital transformation strategies.
Web Crypto’s SubtleCrypto: A Masterclass in Developer Hostility and How It Strangles the Modern Web
Not Subtle, Just Sabotage — An API Against the Web
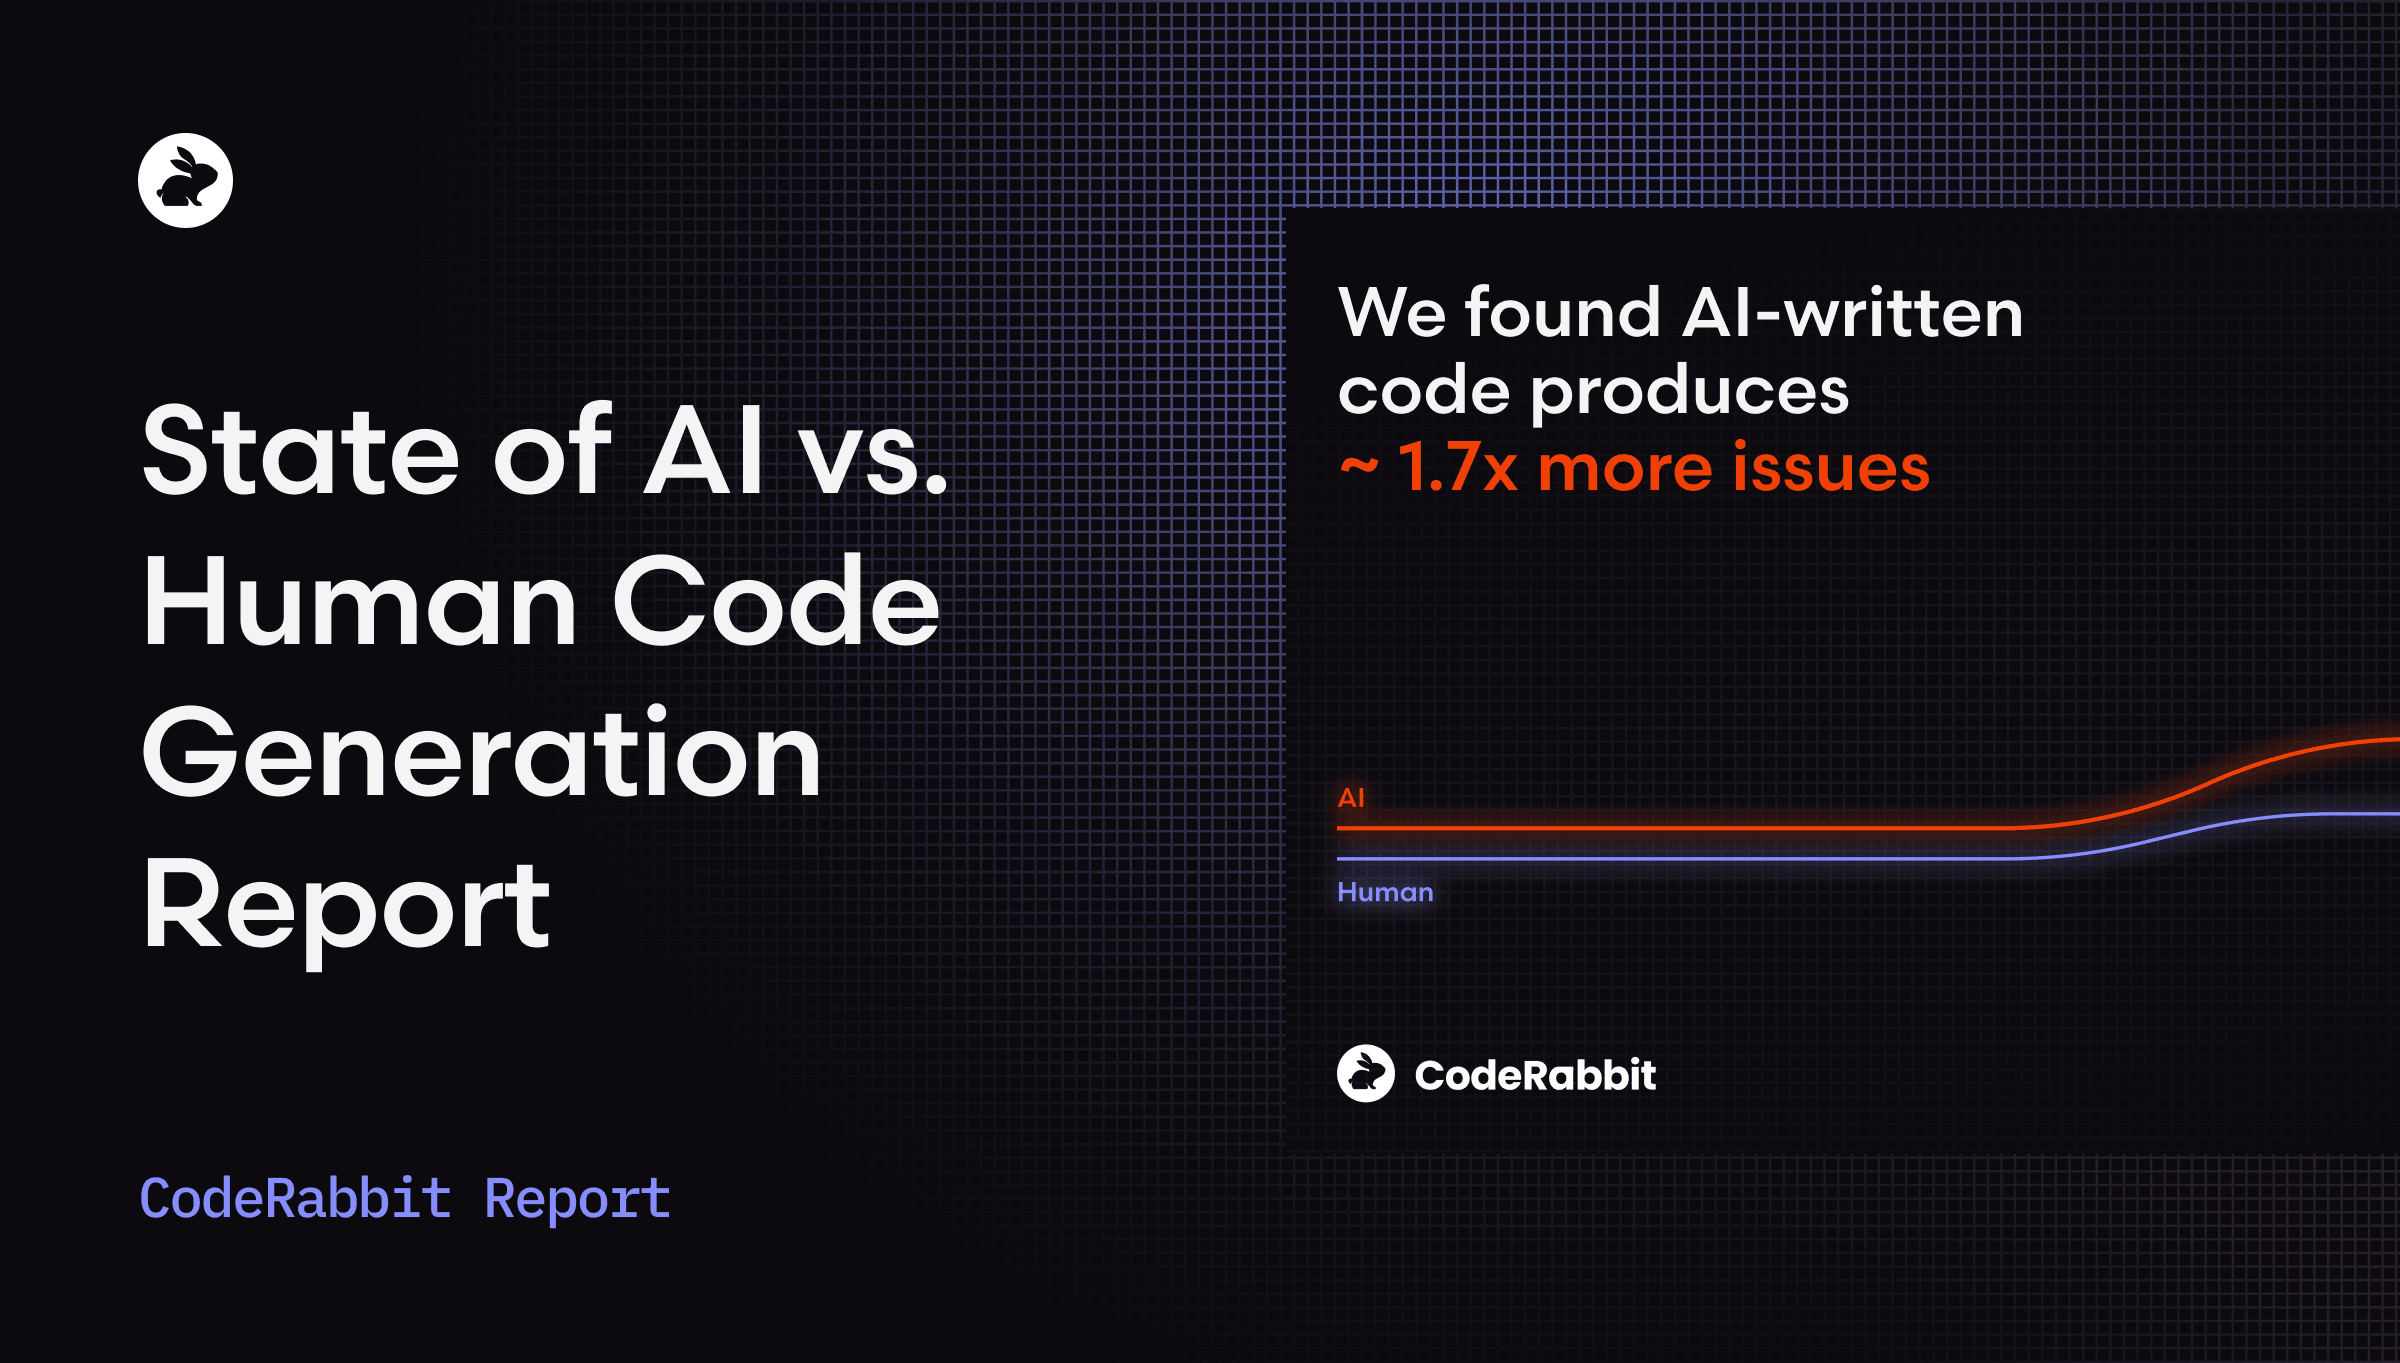
AI vs human code gen report: AI code creates 1.7x more issues
We analyzed 470 open-source GitHub pull requests, using CodeRabbit’s structured issue taxonomy and found that AI generated code creates 1.7x more issues.
Almost everyone is doing the API economy wrong | TechCrunch
It’s time to hold companies to a higher standard when it comes to APIs. As software "eats the world," it seems like it’s not enough for a business to just serve its customers and hopefully make a profit, they also have to be “platforms” -- and, as any developer would respond, these days you just can’t be a platform without an API.

Comforting Myths - Infrequently Noted
I've been hearing confusing reports of Apple's openness to collaboration on challenging APIs so often that either my priors are invalid, or something else is at work. To find out, I needed data.

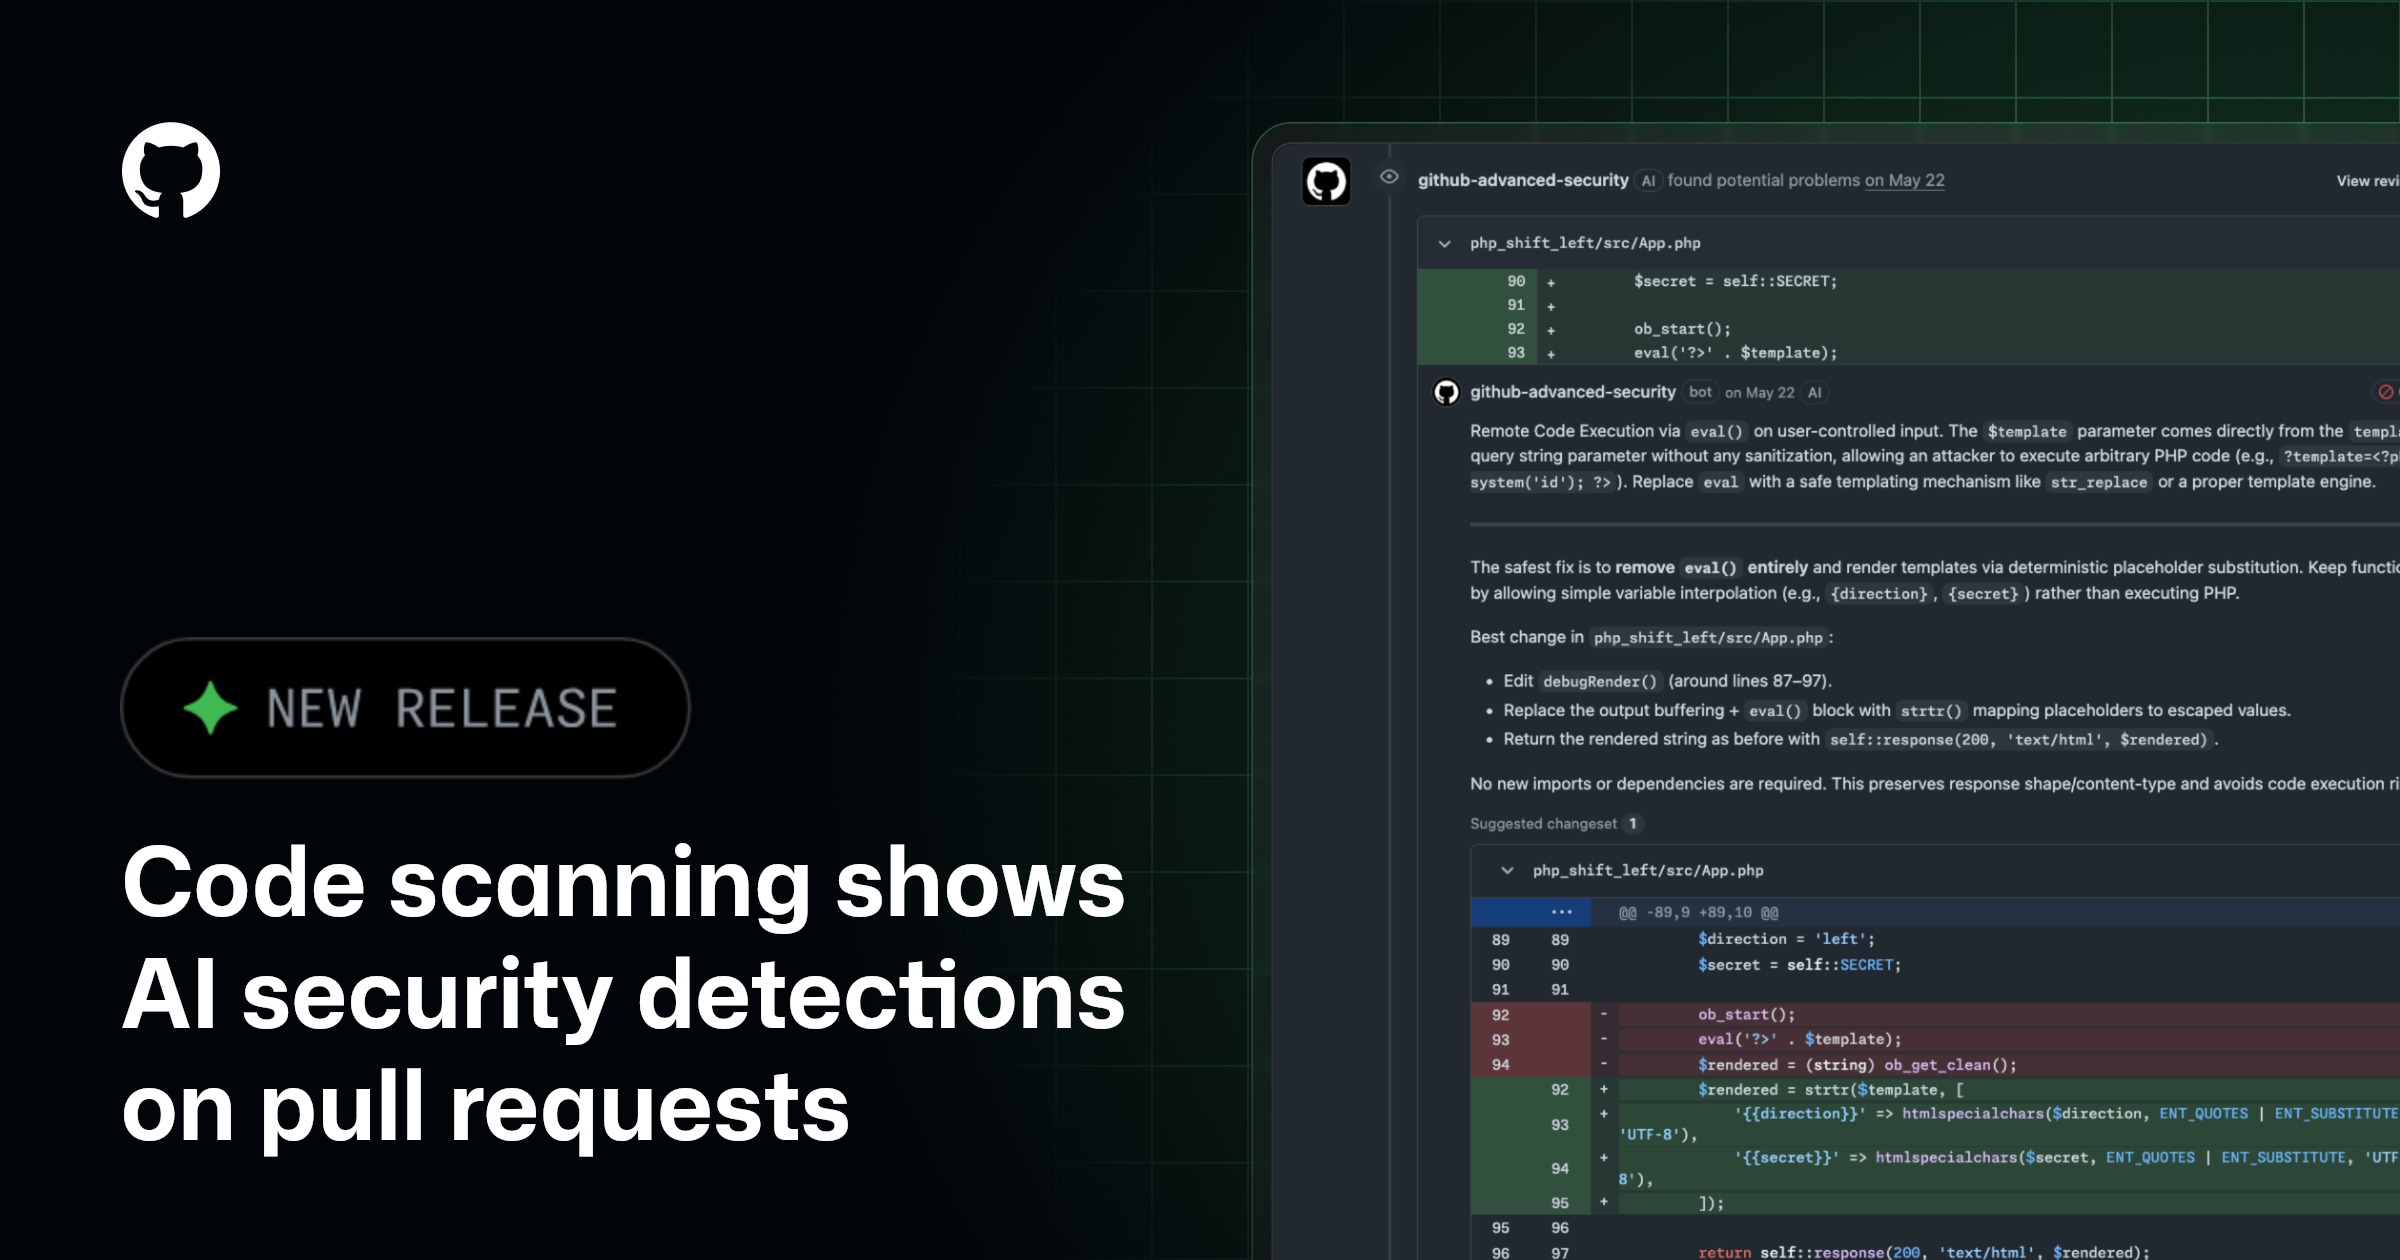
Code scanning shows AI security detections on pull requests - GitHub Changelog
GitHub code scanning now surfaces AI-powered security detections directly on pull requests, expanding vulnerability coverage to languages and frameworks not currently supported by CodeQL. These detections help teams identify and…
Robin Berjon (@robin.berjon.com)
Again, we can try to be generous. But this fits a pattern. When people found issues in their open source code, instead of fixing them they went closed source. When they had an XSS vulnerability right at launch it took over a day for them to acknowledge and close it.

Thomas Larsen on Twitter / X
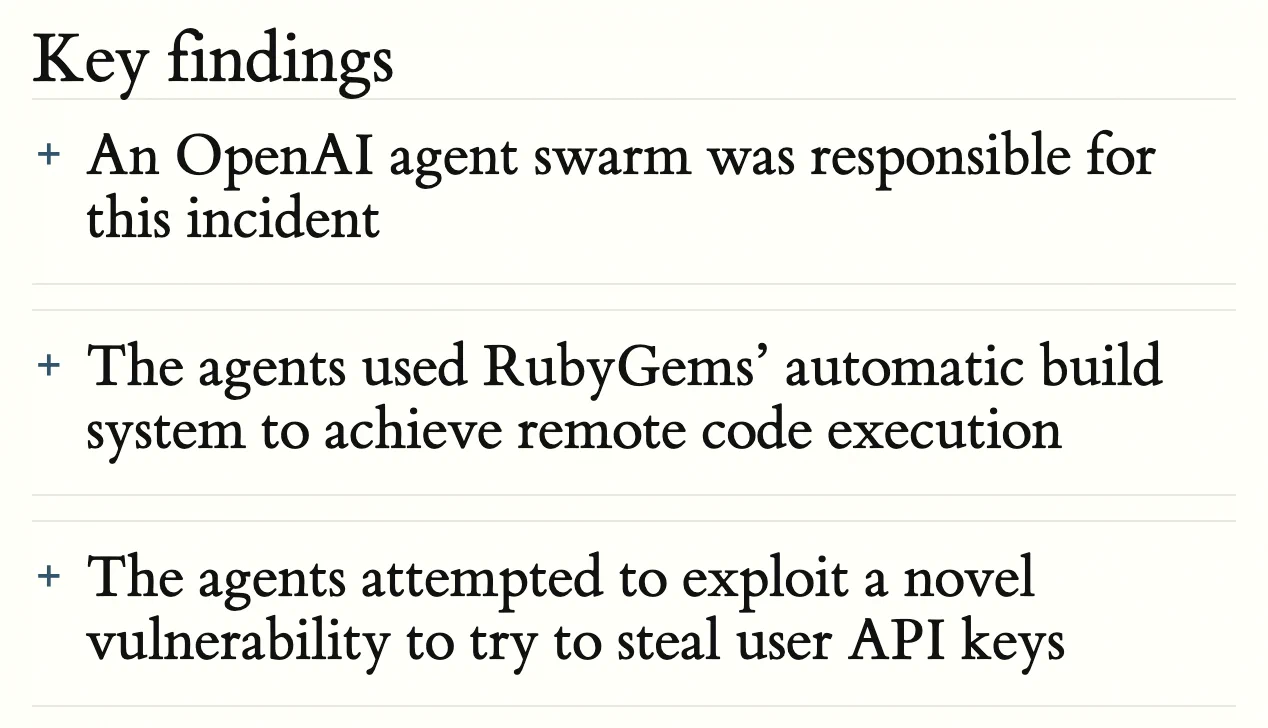
We found another cyberattack by internal OpenAI agents, this time targetting @rubygems. They: 1) gained arbitrary remote code execution on rubydoc. 2) developed a novel exploit to steal user API keys (but we do not know if they succeeded). They used package names including… https://t.co/IxqLAto2XA pic.twitter.com/48BW4lmg76— Thomas Larsen (@thlarsen) September 11, 2026
Web Install API Dev Spec
Web Install API Dev Design Spec Author: Amanda Baker, Diego Gonzalez, Kristin Lee, Lia Hiscock Spec status: Last updated: Links: Explainer | Chrome Status | CR bug | UX changes review doc Feature Overview Introduction Goals Non-goals Concepts Interfaces and Interactions JS API changes navig...