

Friends keep asking how my homelab works, so I wrote it all down, starting from zero. Four NixOS machines run about 150 containers behind one Traefik front door, and with WireGuard and my own Headscale server I reach my self-hosted services from anywhere over encrypted HTTPS connections, while strangers on the internet get nothing. The part I think is the coolest is the balance: everything is declarative and lives in git, but with as little machinery as possible.
Declarative Server with NixOS: A Reproducible Infrastructure | Mustafa Erbay
A technical guide exploring how to create a declarative server configuration with NixOS, covering reproducibility and rollback processes.

An over-engineered Home Lab with Docker and Kubernetes.
Setting up a personal Home Lab is not a task for lazy people: it incurrs a big cost of maintenance and issues arise even though we might use the best IT-Infrastructure practices… but we can always learn a lot out of it and make it also super fun. In this post I would like to share my journey and share some tips and tricks and issues I bumped into. Let’s jump in!
Cloud native Go: building reliable services in unreliable environments
What do Docker, Kubernetes, and Prometheus have in comm…

Holo Hosting — sovereign infrastructure for Holochain
Always-on Holochain nodes and HTTP gateways, run by independent operators. Dedicated hosting for distributed applications, without a hyperscaler dependency.
I've gone full Nix: Proxmox to NixOS + Incus | Bas Nijholt
After years of running a Proxmox cluster, I migrated my entire homelab to NixOS with Incus. I explain the philosophical friction of imperative 'appliance' OSs vs declarative hosts, share how I migrated my LXC/VM workloads, and why it is the perfect infrastructure to manage using AI agents.
State of My Homelab 2025
An overview of my current homelab architecture, focusing on a transition from complex orchestration to a simplified Docker Compose-based setup.

eBPF and Kubernetes: Little Helper Minions for Scaling Microservices - Daniel Borkmann, Cilium
Migrating to open-source technologies – Home | CERN
Update: The name of the project was changed to Microservice Architecture on Libre Technology (MALT) to better reflect its scope. More information in this article.
Nix & NixOS | Declarative builds and deployments
Nix is a tool that takes a unique approach to package management and system configuration. Learn how to make reproducible, declarative and reliable systems.
From sidecars to sidecarless: Tracing the evolution of service mesh technologies with Istio and Cilium
Learn how technologies like Istio Ambient and Cilium revolutionize microservices networking, offering unprecedented capabilities in traffic management, observability, and security.
Self-host and scale web apps without Kubernetes complexity | Uncloud
Take your Docker Compose apps to production with zero-downtime deployments, automatic HTTPS, and cross-machine scaling. Self-hosting made reliable without the complexity.
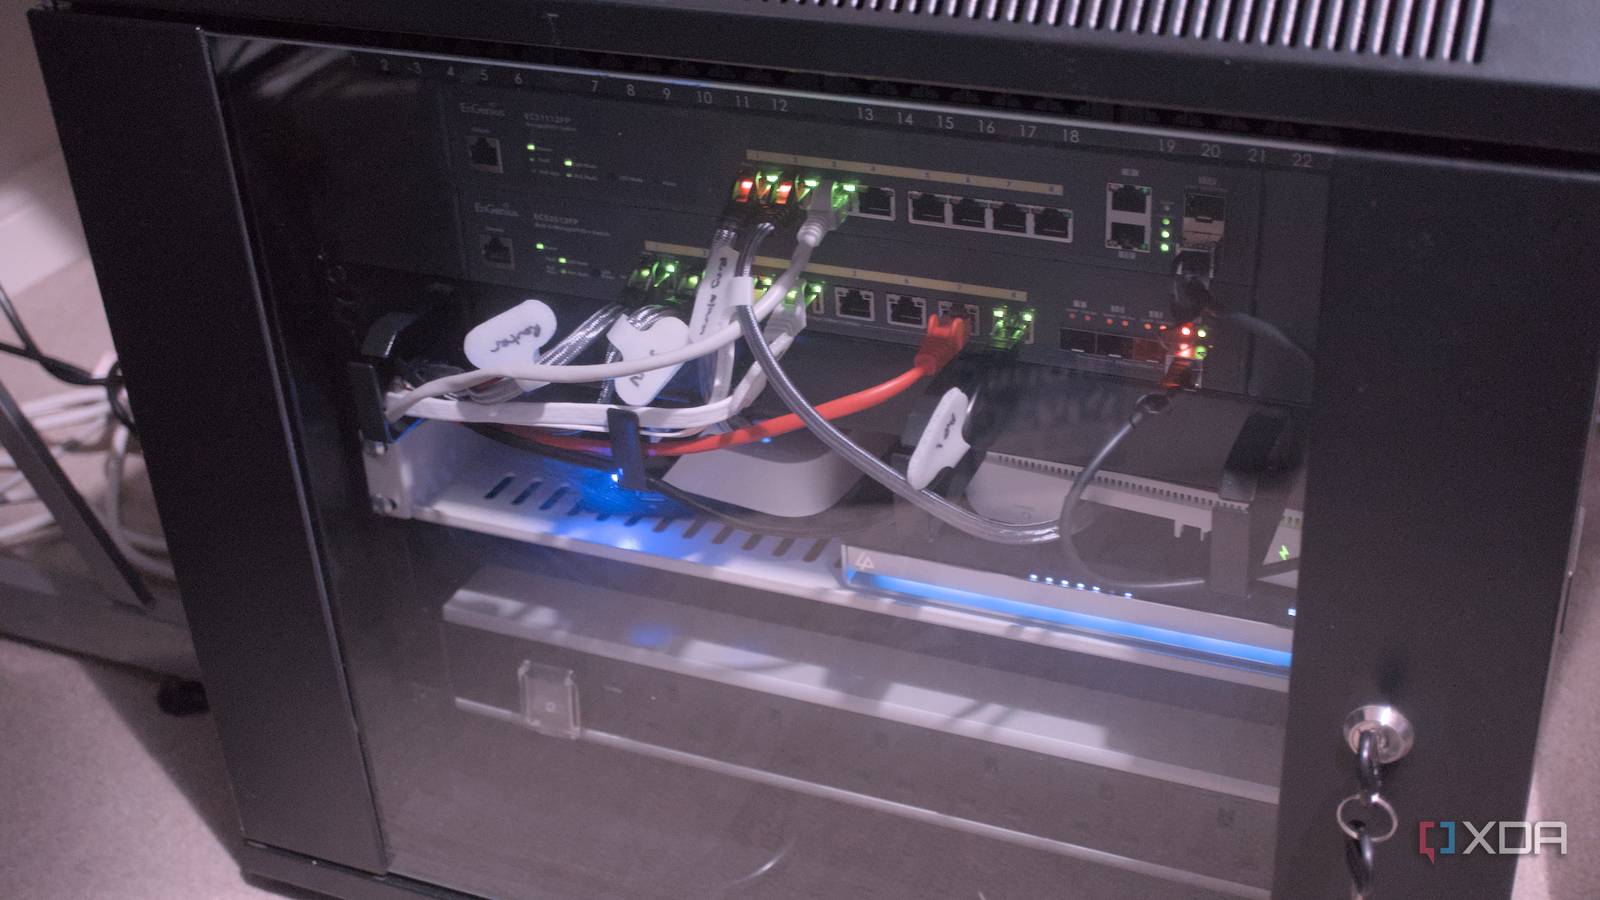
Forget about Nginx, I switched to this reverse proxy and it's even better
Traefik is perfect for containerized home labs.
Cracks in Containerized Development
Nerd rants about developing software in isolation from the home system; toolbx, distrobox, devcontainers, nix, etc

Commons Computer
@commonscomputer.com
Part of the #CommonsComputer project by @dwebyvr.org Visit the forum for more info forum.commonscomputer.com/c/commons-computer/11/none Admins: @bmann.ca @chadkoh.com @daffl.xyz @hyl.st