OWASP GenAI Security Project Releases Top 10 Risks and Mitigations for Agentic AI Security
Culmination of over 100 industry leaders’ input and extensive published resources to deliver critical guidance to address Agentic AI Security risks WILMINGTON, Del. — Dec. 10, 2025 — The OWASP GenAI Security Project (genai.owasp.org), a leading global open-source and expert community dedicated to delivering practical guidance and tools for securing generative and agentic AI, […]

Top AI Security Incidents of 2025 Revealed | Adversa AI
Discover how AI systems are being hacked in the wild — from prompt injection to agent abuse — with real breaches, lessons, and defenses in Adversa AI’s 2025 report.

What is AI Agent Security Plan 2026? Threats and Strategies Explained
Learn what AI agent security is, understand key threats like prompt injection and tool abuse, core AI security principles, and best practices to secure AI agents.

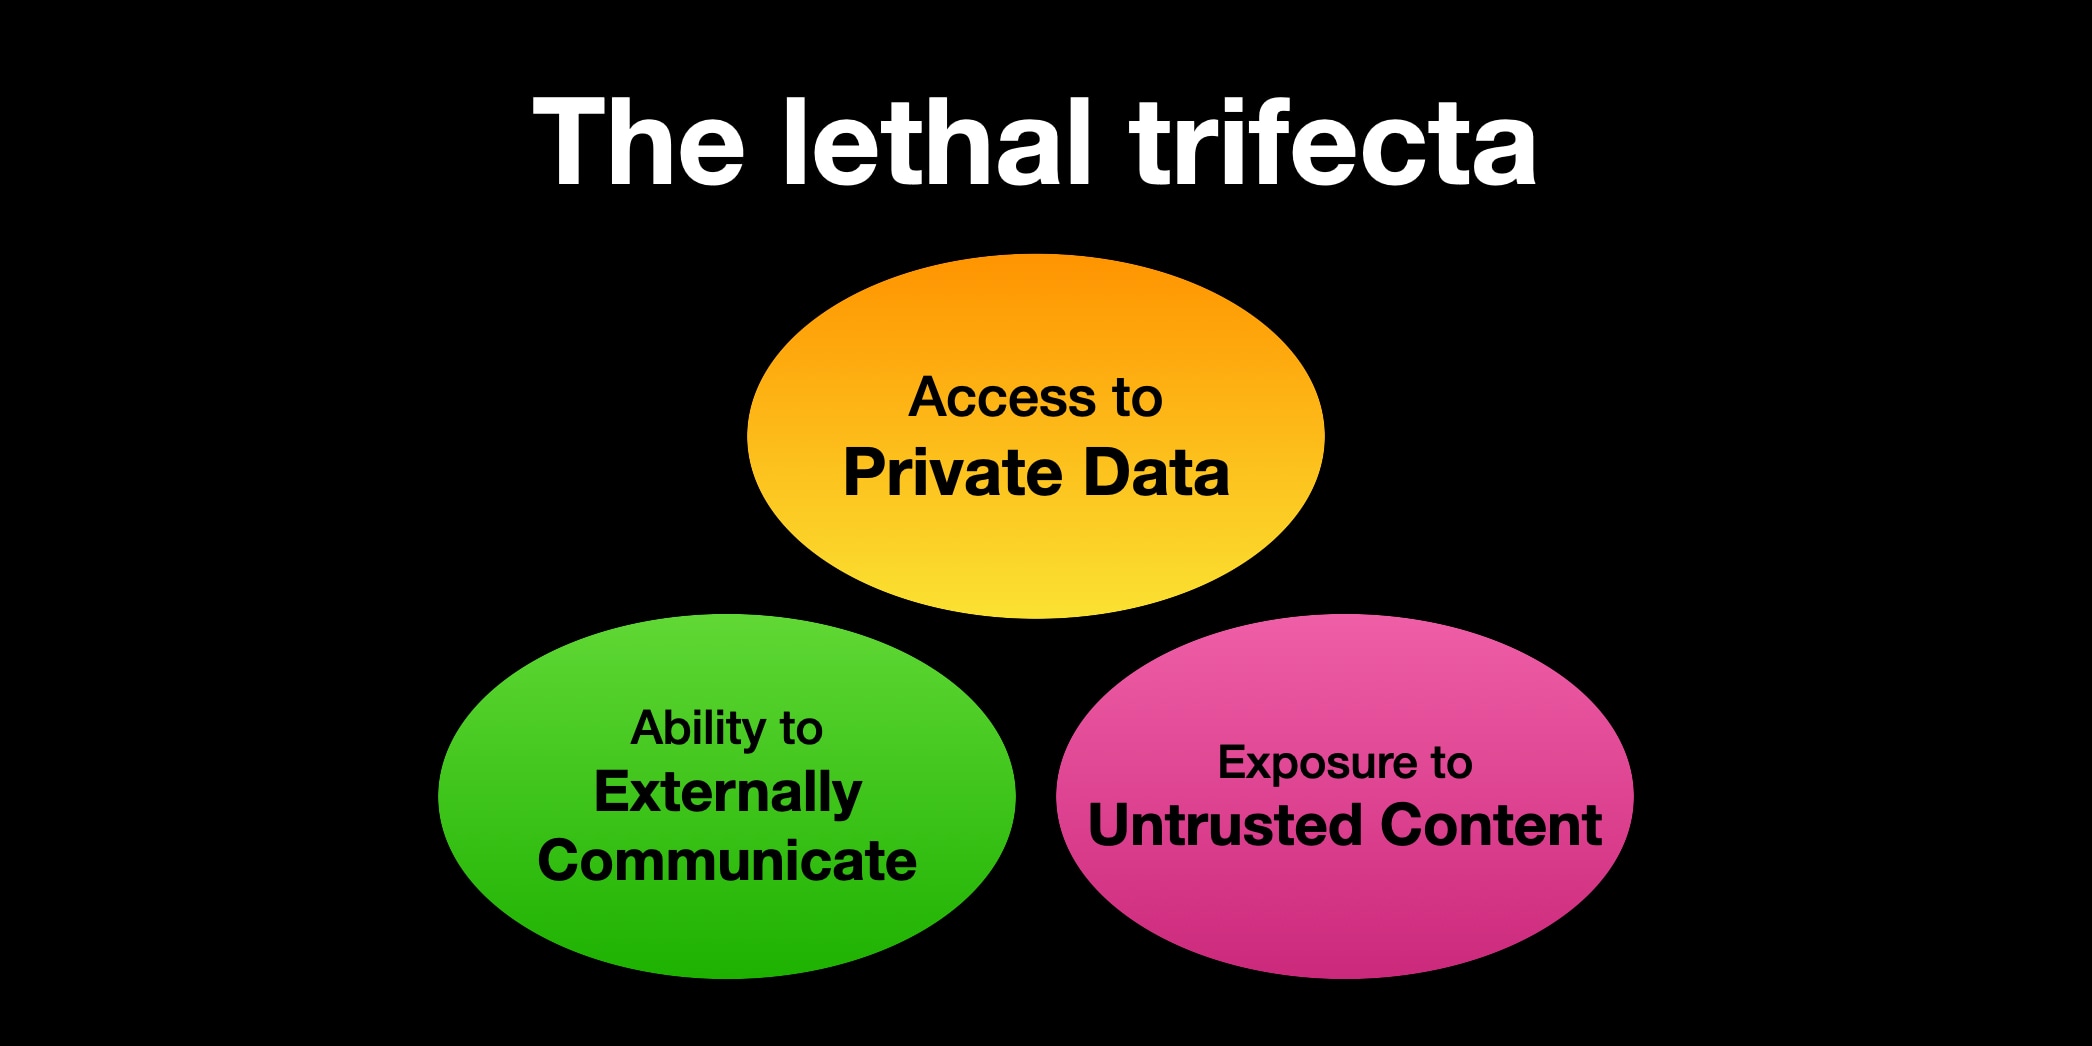
The lethal trifecta for AI agents: private data, untrusted content, and external communication
If you are a user of LLM systems that use tools (you can call them “AI agents” if you like) it is critically important that you understand the risk of …

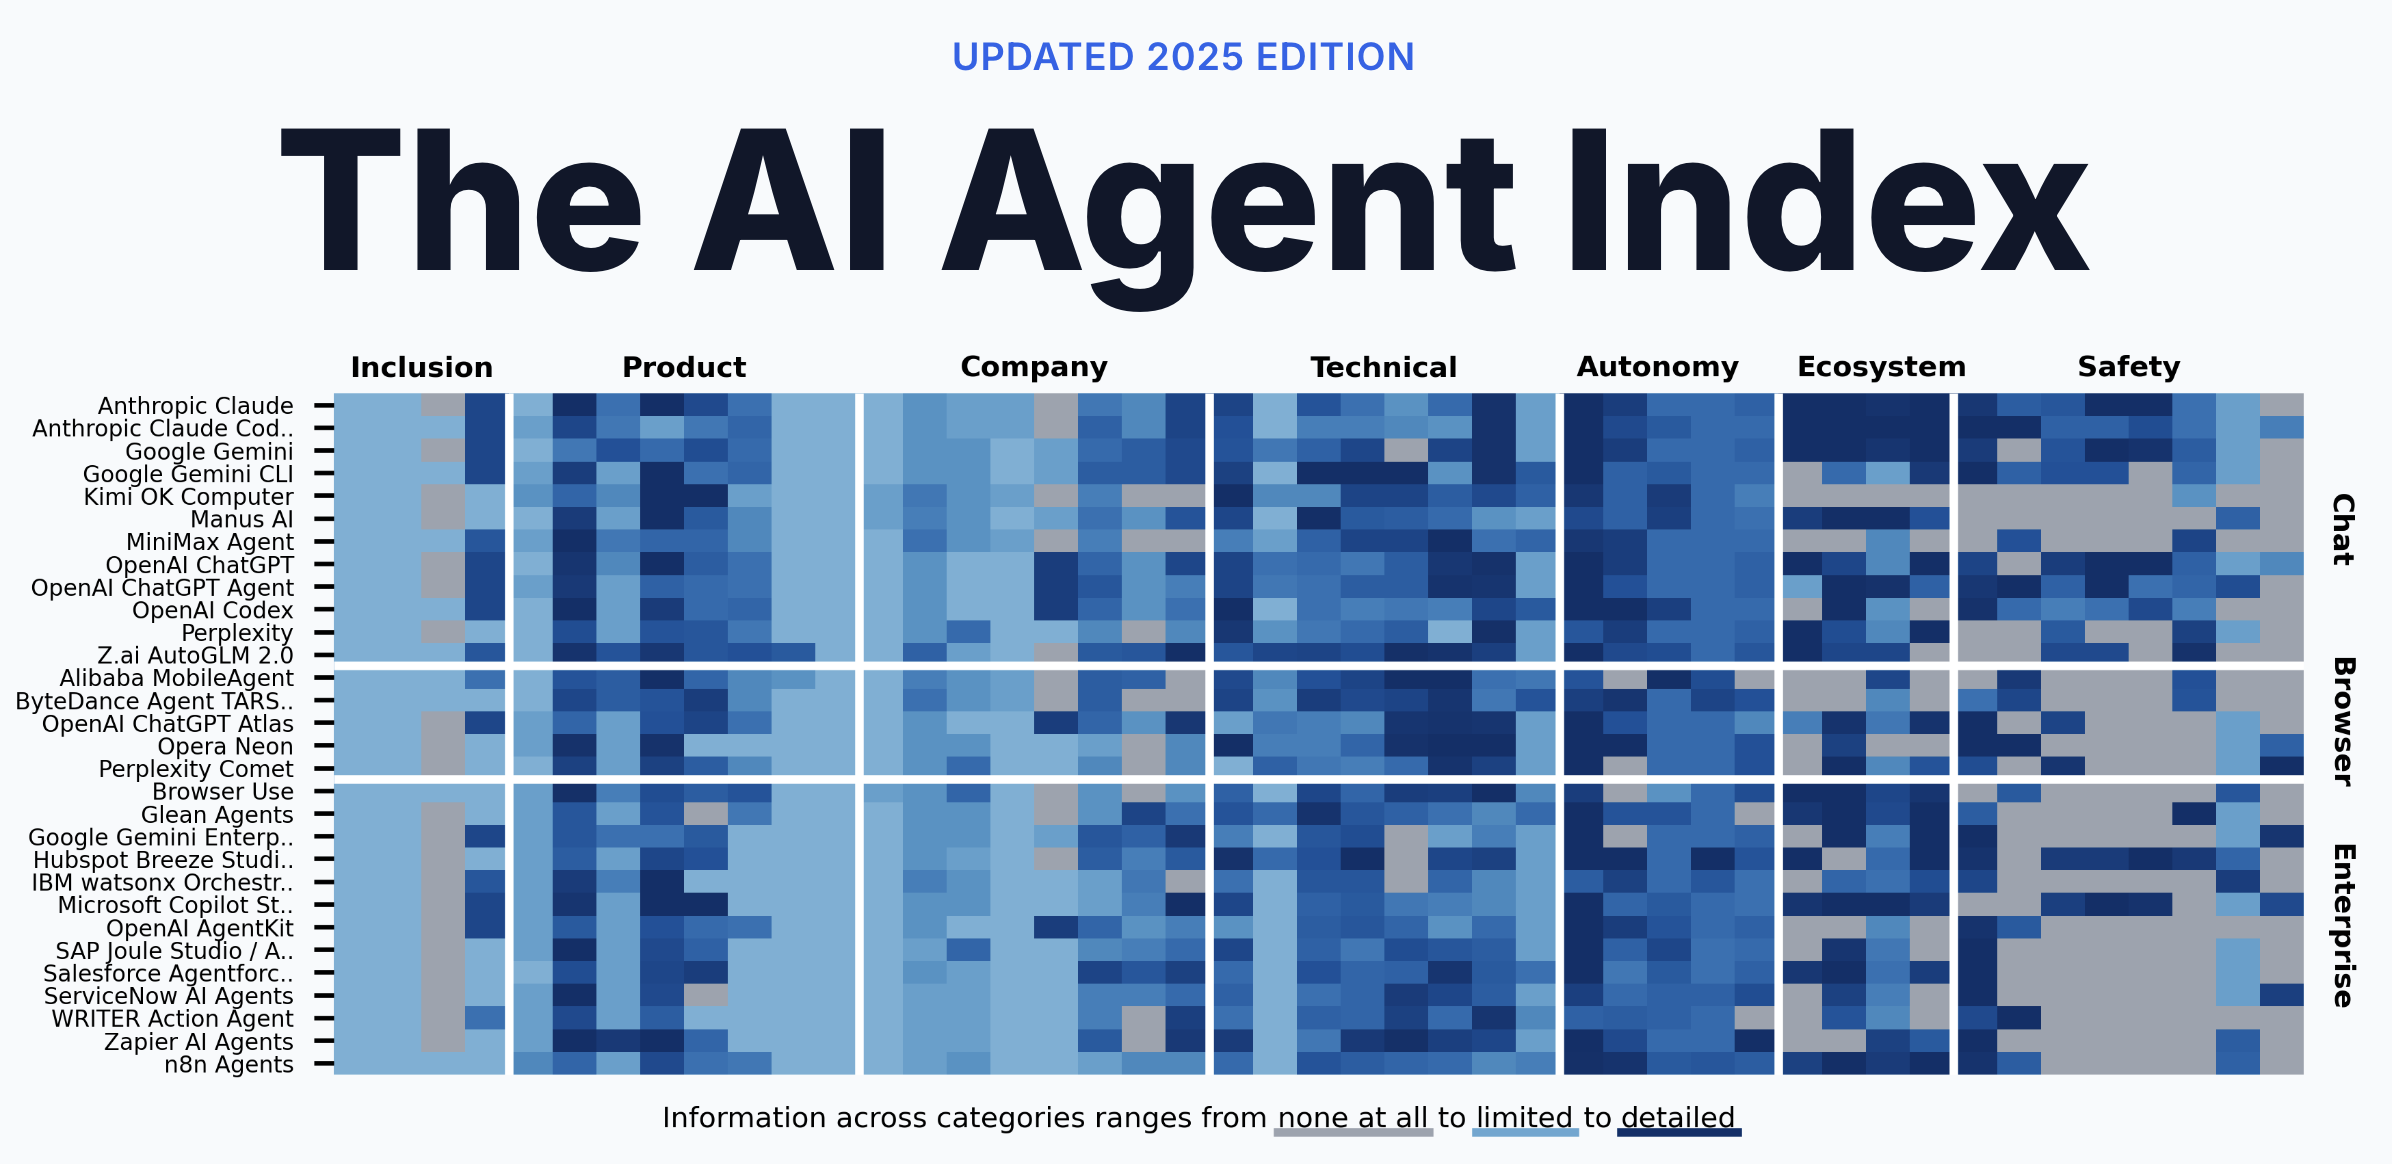
The 2025 AI Agent Index
Agentic AI systems are increasingly capable of performing complex tasks with limited human involvement. The 2025 AI Agent Index documents the origins, design, capabilities, ecosystem, and safety features of 30 prominent AI agents based on publicly available information and correspondence with developers.

Agents Rule of Two: A Practical Approach to AI Agent Security
We've developed the Agents Rule of Two. When this framework is followed, the severity of security risks is deterministically reduced.

Agentic AI Governance: Securing Autonomous AI Agents in Enterprise
When AI agents start making decisions, calling tools, and coordinating with other agents without waiting for human approval, the governance playbook most...

SCAM — How safe is your AI agent?
An open-source benchmark by 1Password that tests whether AI agents can handle real security threats during everyday tasks.
Patterns and problems in multiagent systems
We ran experiments on swarms of Claude agents and found coordination failures, collusion, and sabotage. Here, we share what they mean for AI safety.

I use AI for security work - Tilmon Edwards
A brief introduction to how one might start to think about deploying AI agents into mission-critical applications.
Vulnerability Research Is Cooked
For the last two years, technologists have ominously predicted that AI coding agents will be responsible for a deluge of security vulnerabilities. They were right! Just, not for the reasons they thought.
AI agent runs amok in Fedora and elsewhere
Agentic AI systems can be used to do a variety of things autonomously on behalf of a human user [...]
Securing internal systems against increasingly capable and imperfectly aligned AI
Discover our AI Control Roadmap: a defense-in-depth system to securely manage advanced, potentially misaligned AI agents.
Agentic Engineering Management
To what extent AI is OK to use in software development might be debated, but in general, the idea is not a controversial one anymore. The debate rather moved on from code completion and simple PR summarizations to Agentic Engineering, where an execution loop allows an AI Agent to function

The Malicious Use of Artificial Intelligence: Forecasting,...
This report surveys the landscape of potential security threats from malicious uses of AI, and proposes ways to better forecast, prevent, and mitigate these threats. After analyzing the ways in...


Agency and Agents
ГАЛЬВАНИЗАЦИЯ АВТОРА, ИЛИ ЭКСПЕРИМЕНТ С НЕЙРОННОЙ ПОЭЗИЕЙ. Борис Орехов. «Новый мир» №6, 2018

Personal Online RL | 🌱 | Offprint
Approaching an unknown communication system by latent space exploration and causal inference | Royal Society Open Science | The Royal Society

Surya Narreddi

Permutation: Issue One