

We showcase a critical vulnerability with the official GitHub MCP server, allowing attackers to access private repository data. The vulnerability is among the first discovered by Invariant's security analyzer for detecting toxic agent flows.
GitHub MCP Exploited: Accessing private repositories via MCP
GitHub's official MCP server grants LLMs a whole host of new abilities, including being able to read and issues in repositories the user has access to and submit new pull …
Investigating unauthorized access to GitHub-owned repositories
If any impact is discovered, customers will be notified via established incident response and notification channels.
A GitHub Issue Title Compromised 4,000 Developer Machines
A prompt injection in a GitHub issue triggered a chain reaction that ended with 4,000 developers getting OpenClaw installed without consent. The attack composes well-understood vulnerabilities into something new: one AI tool bootstrapping another.
Introducing the Open-Source Codex Security CLI
Codex Security helps security and engineering teams find, confirm, and fix vulnerabilities. Use its command-line interface (CLI) to scan repositories you own or have permission to assess, review findings over time, and check changes before they land. Quickstart Guide for an interactive scan Cloud set-up for connected GitHub repositories Link to the public repo: Codex Security This is an early release, and we’re listening to your feedback as we continue improving it. The Codex Security CLI ...

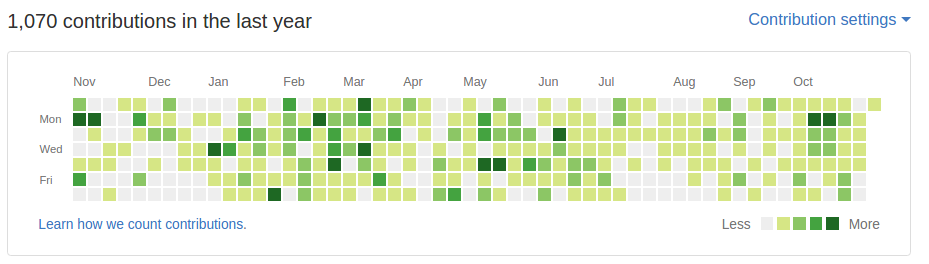
GitHub’s one-dimensional view of open source contributions – Wes McKinney
TL;DR One of the most harmful parts of the GitHub platform is the code contribution calendar. This “hacker score card” overemphasizes the value of commits over the other kinds of important contributions to open source projects, like doing code reviews and discussing bugs and new features on the issue tracker.
Code Repository - Git Source Control | Harness
Host Git repositories in Harness, manage pull requests, and connect every commit to secure CI/CD workflows with source-to-deploy traceability.
How We Exploited CodeRabbit: From a Simple PR to RCE and Write Access on 1M Repositories - Kudelski Security Research Center
Aug 19, 2025 - Nils Amiet -
Incident Report: Leaked GitHub Personal Access Token - The Python Package Index Blog
We responded to an incident related to a leaked GitHub Personal Access Token for a PyPI administrator.

Under the hood: Security architecture of GitHub Agentic Workflows
Learn how our threat model and security architecture help teams run agents safely in GitHub Actions.
Ditching GitHub
This is going to be some sort of a public service announcement, withside notes. This has been brewing for a long, long time (years), it’sjust that I never se...
Is GitHub Cooked?
Track GitHub service incidents and outages. Real-time stats, incident history, and downtime analytics.
npm Worm Poisons keyv, cacheable and 400+ Other Packages Across Twelve Organisations
A worm moved one byte-identical credential stealer through more than 400 npm packages in twelve organisations on 4 August 2026, including @ornikar, @deliveroo, @servicetitan, @qlik, Picsart and the keyv and cacheable family. latest still resolves to a poisoned version on most affected names, and the payload installs a dead-man switch that fires when the stolen GitHub token is revoked, so rotating credentials first triggers it.
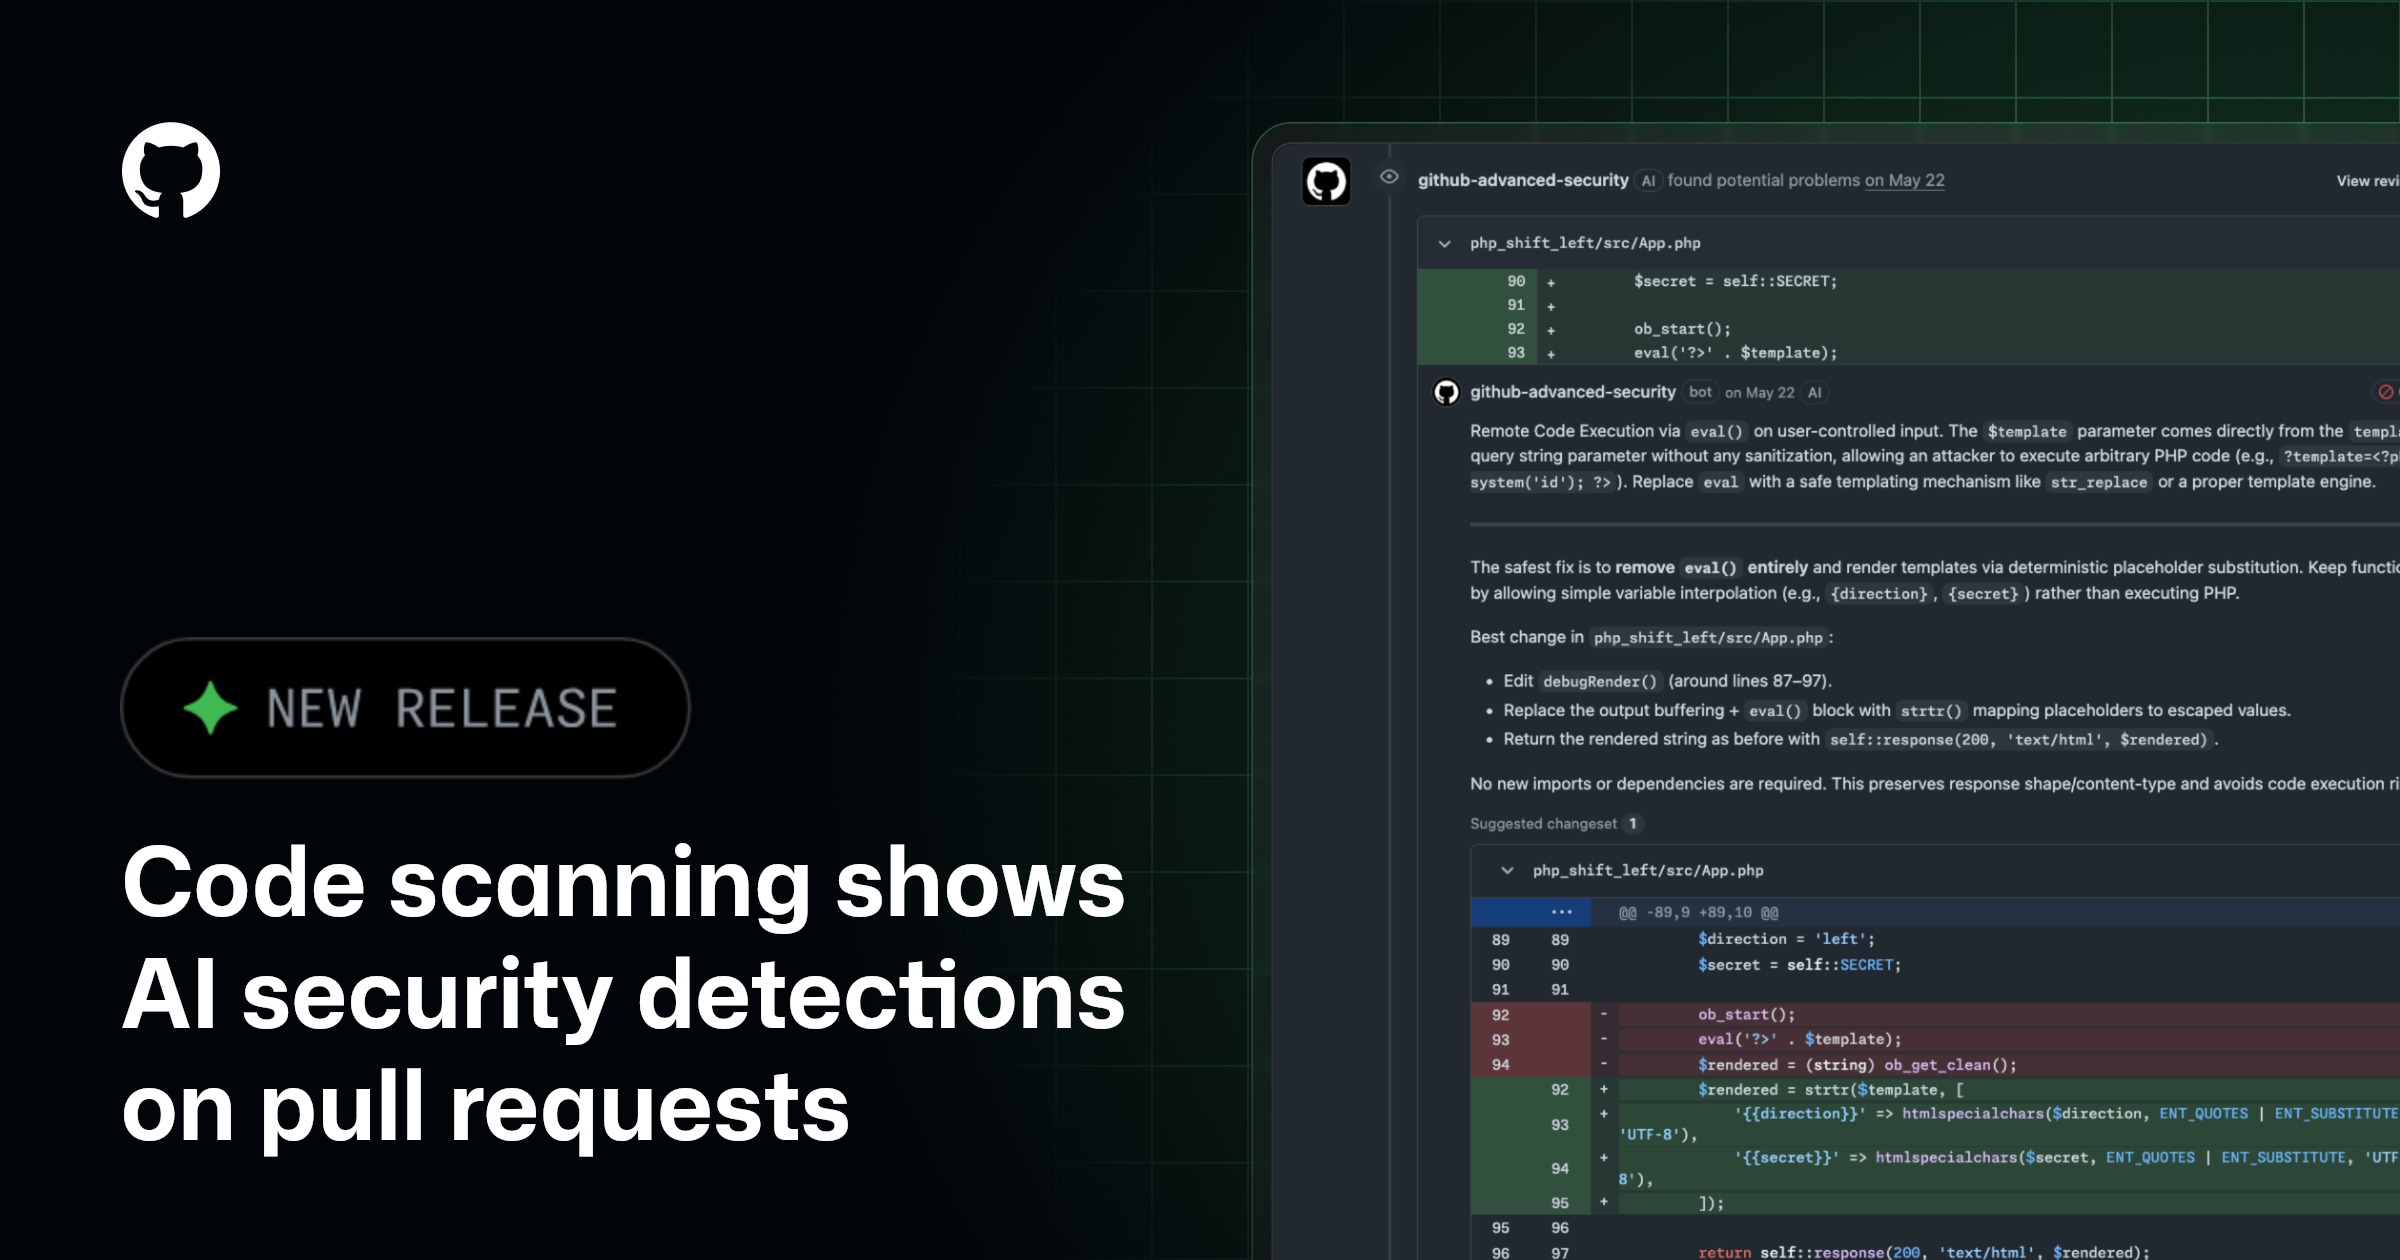
Code scanning shows AI security detections on pull requests - GitHub Changelog
GitHub code scanning now surfaces AI-powered security detections directly on pull requests, expanding vulnerability coverage to languages and frameworks not currently supported by CodeQL. These detections help teams identify and…
Red Squares — the GitHub outage graph
A satirical contribution graph: red squares track GitHub.com platform outages instead of green squares tracking commits.
Enterprise MCP: lessons from GitHub's MCP server launch
GitHub's Engineer shares lessons from developing GitHub's MCP server. An Arcade MCP MVP interview.
Hack-with-Github/Awesome-Hacking
A collection of various awesome lists for hackers, pentesters and security researchers