Agentic AI Governance: Securing Autonomous AI Agents in Enterprise
When AI agents start making decisions, calling tools, and coordinating with other agents without waiting for human approval, the governance playbook most...

Agentic AI Governance: Securing Autonomous AI Agents in Enterprise
When AI agents start making decisions, calling tools, and coordinating with other agents without waiting for human approval, the governance playbook most...
From chatbots to assistants: governance is key for AI agents
AI's shift into agentic technology ushers in a new set of governance and security challenges that will mean defining to what extent they should be autonomous
Introducing the Agent Governance Toolkit: Open-source runtime security for AI agents | Microsoft Open Source Blog
Discover how the Microsoft Agent Governance Toolkit brings policy, identity, and reliability to autonomous AI agent systems.
Agentic AI Governance: A Strategic Framework for Autonomous Systems
Agentic AI is moving from chat to action. Learn how to govern autonomous systems using the "Digital Contractor" framework and the 3-Tiered Guardrail system.
The AI-as-Normal-Technology view of loss of control incidents
A middle ground between the cybersecurity and AI safety communities
Autonomy and Innovation
Incentives favor offense when it comes to agentic cybersecurity; it’s the same dynamic that will limit incumbents and fuel startups in the long run.

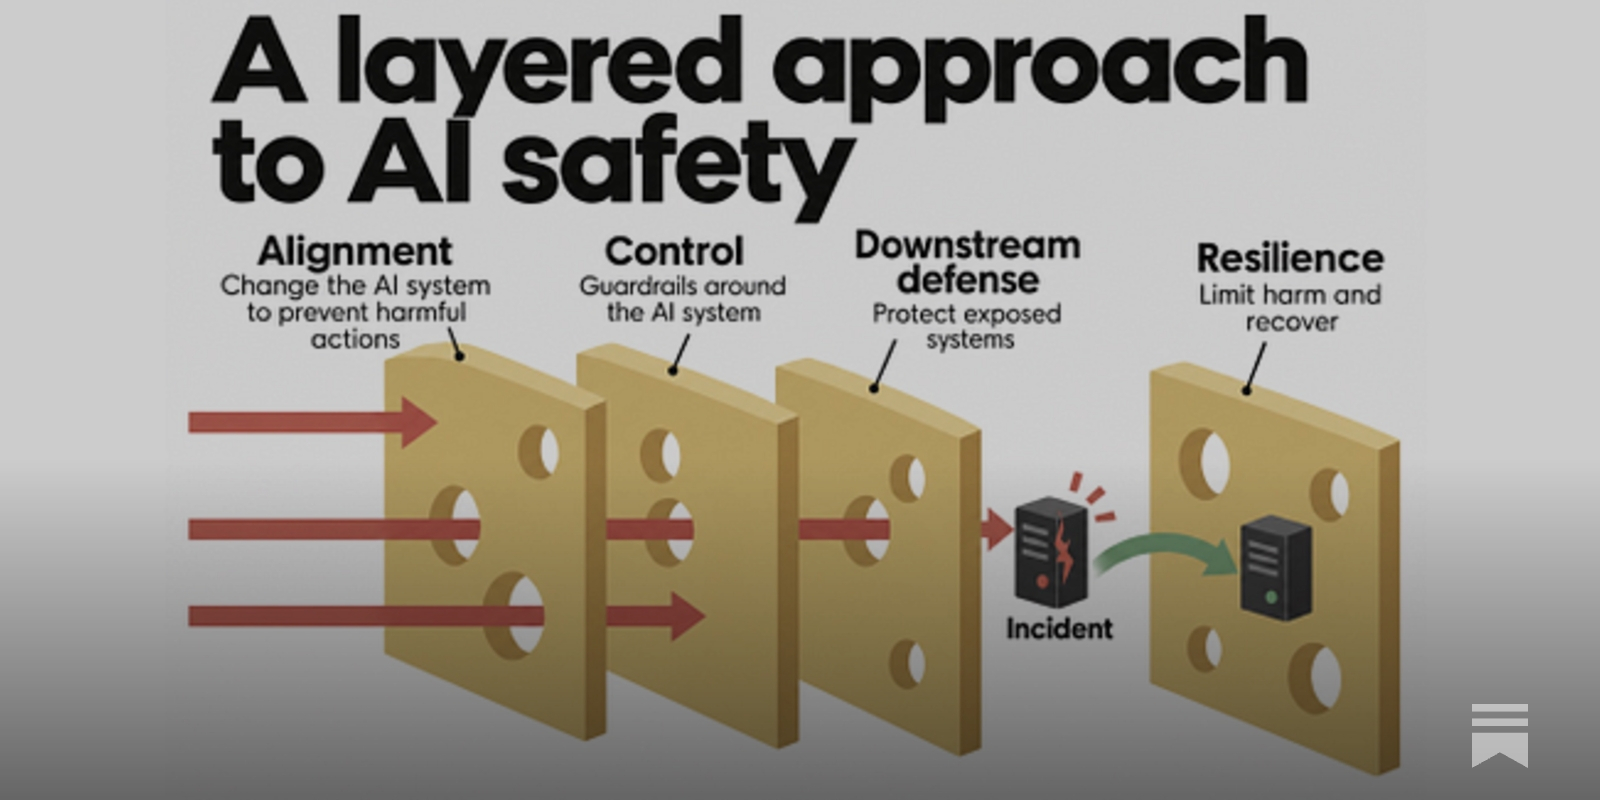
Securing internal systems against increasingly capable and imperfectly aligned AI
Discover our AI Control Roadmap: a defense-in-depth system to securely manage advanced, potentially misaligned AI agents.

Statement from Dario Amodei on our discussions with the Department of War
A statement from our CEO on national security uses of AI
Will we have a theory for in-the-wild AI agents? - undisciplinary
Thoughts after writing a sociology-meets-physics-meets-agents paper I just put out a preprint out on a theory of role emergence in multi-agent systems (soci…
Hackers build AI frameworks for widescale credential theft
Threat actors are increasingly switching from AI-powered coding assistants to multi-agent frameworks that automate every stage of an attack.
Top AI Security Incidents of 2025 Revealed | Adversa AI
Discover how AI systems are being hacked in the wild — from prompt injection to agent abuse — with real breaches, lessons, and defenses in Adversa AI’s 2025 report.

Agents Rule of Two: A Practical Approach to AI Agent Security
We've developed the Agents Rule of Two. When this framework is followed, the severity of security risks is deterministically reduced.

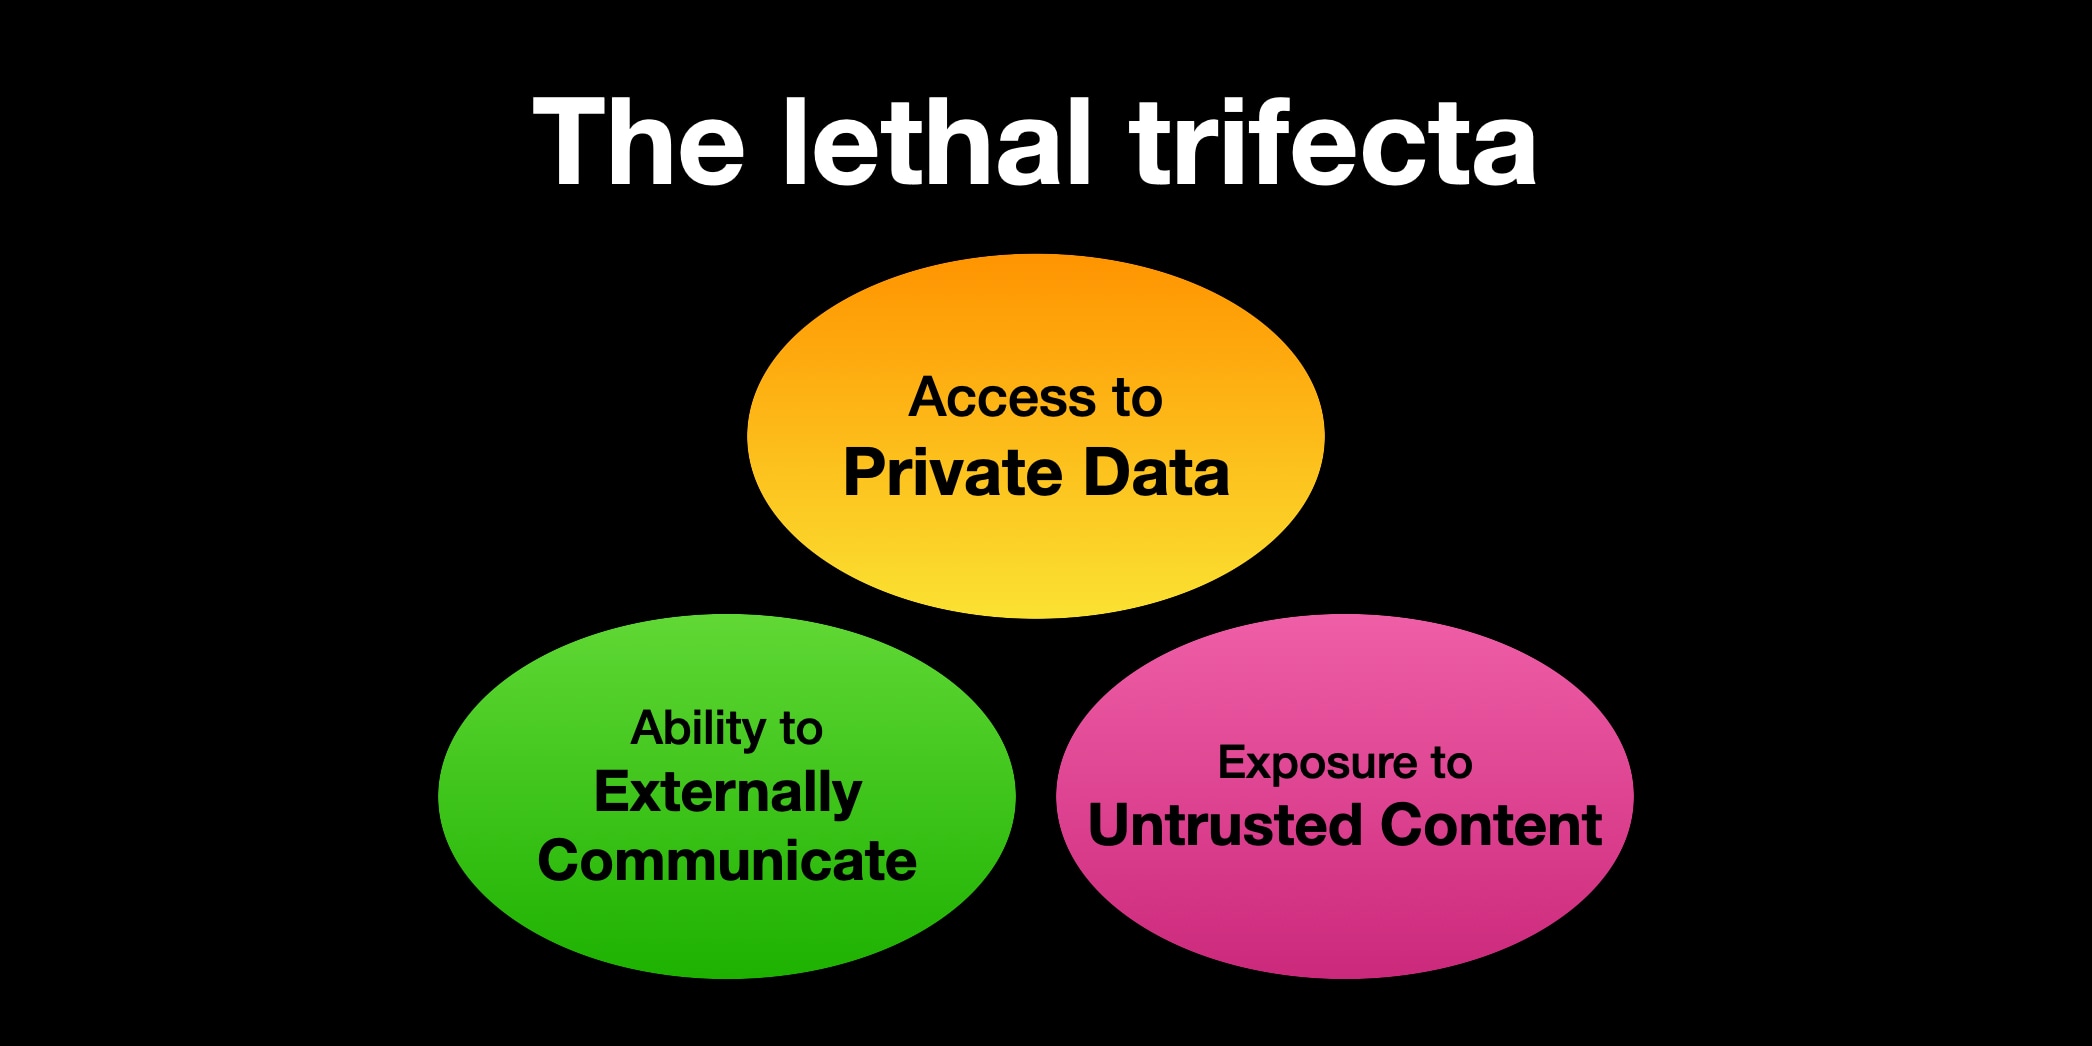
The lethal trifecta for AI agents: private data, untrusted content, and external communication
If you are a user of LLM systems that use tools (you can call them “AI agents” if you like) it is critically important that you understand the risk of …
Patterns and problems in multiagent systems
We ran experiments on swarms of Claude agents and found coordination failures, collusion, and sabotage. Here, we share what they mean for AI safety.

Collection

Updated 5mo
Research on autonomous AI agents applied to security, forensics, and the governance questions they raise. Focus on the cat-and-mouse dynamics between offensive and defensive AI.
AI* and law enforcement/surveillance/war

See also: fascism/discrimination/bias/politics semble.so/profile/aiueo.ooo/collections… * I’m neither “pro-AI” nor “anti-AI.” I’ve been blocked for being perceived as both. —Actually, I’m honestly more anti-AI than pro-AI thus far, aside from specialized models and specific use cases, but I’m willing to consider information that’s new to me
AI

AI research, critical perspectives, agent design, digital humanities. How AI systems work, their embedded values, and the thinking around building agentic systems.

「中国船が核兵器部品を輸送」 米軍、AI使用の誤った情報報告書で一触即発の状況に

米軍、AI誤報で作戦計画 中国船に「核部品」、直前中止 | NEWSjp
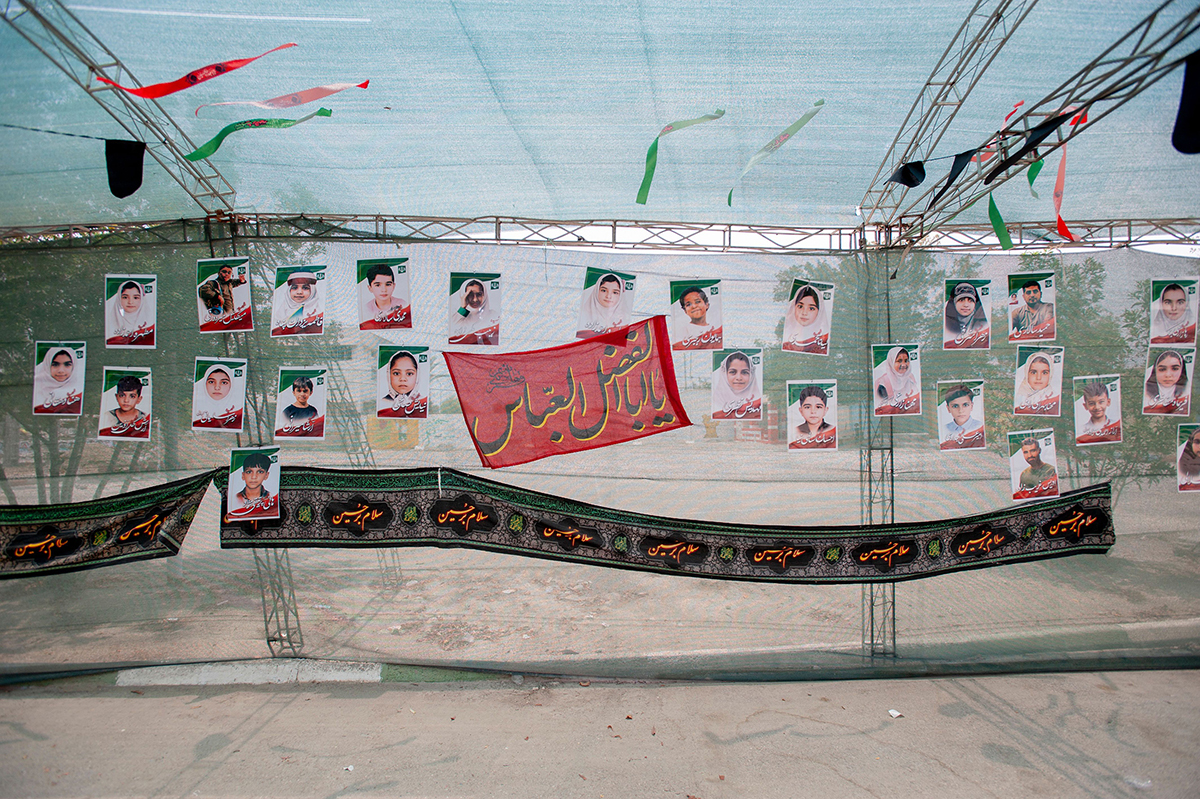
Inside the US ‘Kill Chain’ That Destroyed an Iranian School
Responsible use of AI in the military? US publishes declaration outlining principles
Pentagon boasts of using AI to write reports mandated by Congress
Anthropic releases custom AI chatbot for classified spy work
Agency and Agents
ГАЛЬВАНИЗАЦИЯ АВТОРА, ИЛИ ЭКСПЕРИМЕНТ С НЕЙРОННОЙ ПОЭЗИЕЙ. Борис Орехов. «Новый мир» №6, 2018

Personal Online RL | 🌱 | Offprint
Approaching an unknown communication system by latent space exploration and causal inference | Royal Society Open Science | The Royal Society
Surya Narreddi

Permutation: Issue One